Pierluigi Paganini
 May 16, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in Microsoft Exchange Server to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a flaw in Microsoft Exchange Server, tracked as CVE-2026-42897 (CVSS score of 8.1), to its Known Exploited Vulnerabilities (KEV) catalog. This week, Microsoft warned that threat actors are […]
 Pierluigi Paganini
May 15, 2026
Microsoft warned that attackers are exploiting a new Exchange Server zero-day vulnerability, tracked as CVE-2026-42897, in the wild. Microsoft warned that threat actors are actively exploiting a new Exchange Server zero-day vulnerability tracked as CVE-2026-42897 (CVSS score 8.1). The vulnerability is an improper neutralization of input during web page generation (‘cross-site scripting’) in Microsoft Exchange […]
 Pierluigi Paganini
May 15, 2026
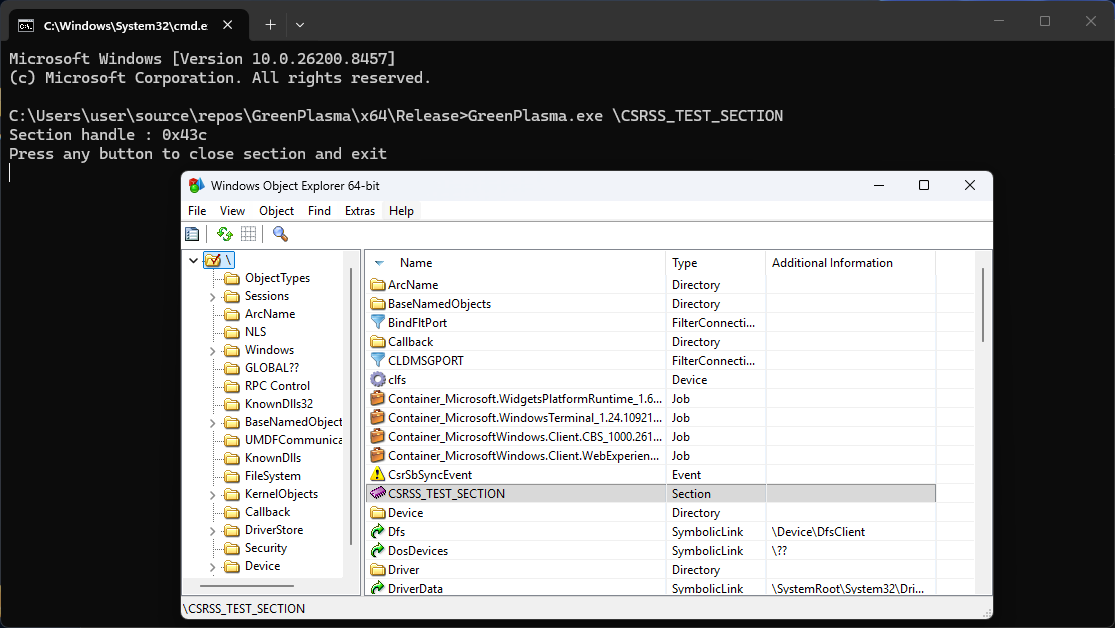
Researchers disclosed two new Windows zero-days named YellowKey and GreenPlasma affecting BitLocker and the CTFMON framework. A security researcher known as Chaotic Eclipse, also called Nightmare-Eclipse, disclosed two new Windows zero-day vulnerabilities named YellowKey and GreenPlasma. The flaws affect BitLocker and the Windows Collaborative Translation Framework (CTFMON). YellowKey could allow attackers to bypass BitLocker protections, […]
 Pierluigi Paganini
May 11, 2026
Google says hackers now use AI to create exploits, automate attacks, evade defenses, and target AI supply chains at scale. Artificial intelligence is rapidly changing the cyber threat landscape, and a new report from the Google Cloud Threat Intelligence team highlights how attackers already use AI to improve vulnerability exploitation and gain initial access to […]
 Pierluigi Paganini
April 18, 2026
Attackers exploit three Microsoft Defender zero-days, code-named BlueHammer, RedSun, and UnDefend, to gain elevated access. Attackers are exploiting three recently disclosed zero-day flaws in Microsoft Defender to gain higher privileges on compromised systems. The vulnerabilities, called BlueHammer, RedSun, and UnDefend, were revealed by a researcher known as Chaotic Eclipse after criticizing Microsoft’s handling of the […]
 Pierluigi Paganini
April 15, 2026
Microsoft Patch Tuesday security updates for April 2026 fixed 165 vulnerabilities, including an actively exploited SharePoint zero-day. Microsoft Patch Tuesday security updates addressed 165 vulnerabilities, making it one of the largest updates by CVE count. One of the most interesting flaws fixed by the IT giant is a critical SharePoint zero-day, tracked as CVE-2026-32201, already […]
 Pierluigi Paganini
April 09, 2026
Hackers used an Adobe Reader zero-day for months. Researcher Haifei Li found a malicious PDF and asks the community to help analyze it. Hackers used an Adobe Reader zero-day for months to deliver a sophisticated PDF exploit. Cybersecurity researcher Haifei Li, founder of Expmon, discovered the malicious file and warned the community. On March 26, […]
Pierluigi Paganini
April 07, 2026
A researcher leaked the unpatched Windows zero-day “BlueHammer,” letting attackers gain SYSTEM rights; no patch exists yet. A disgruntled researcher released the BlueHammer Windows zero-day, a privilege escalation flaw that allows attackers to gain SYSTEM or admin rights, Bleeping Computer reports. The researcher privately reported the vulnerability to Microsoft but criticized the way the Microsoft’s Security […]
 Pierluigi Paganini
March 13, 2026
Google addressed two high-severity vulnerabilities in the Chrome browser that have been exploited in attacks in the wild. Google has released security updates to address two high-severity vulnerabilities, tracked as CVE-2026-3909 and CVE-2026-3910, in the Chrome browser. The company is aware of attacks in the wild exploiting both flaws. “Google is aware that exploits for […]
 Pierluigi Paganini
March 06, 2026
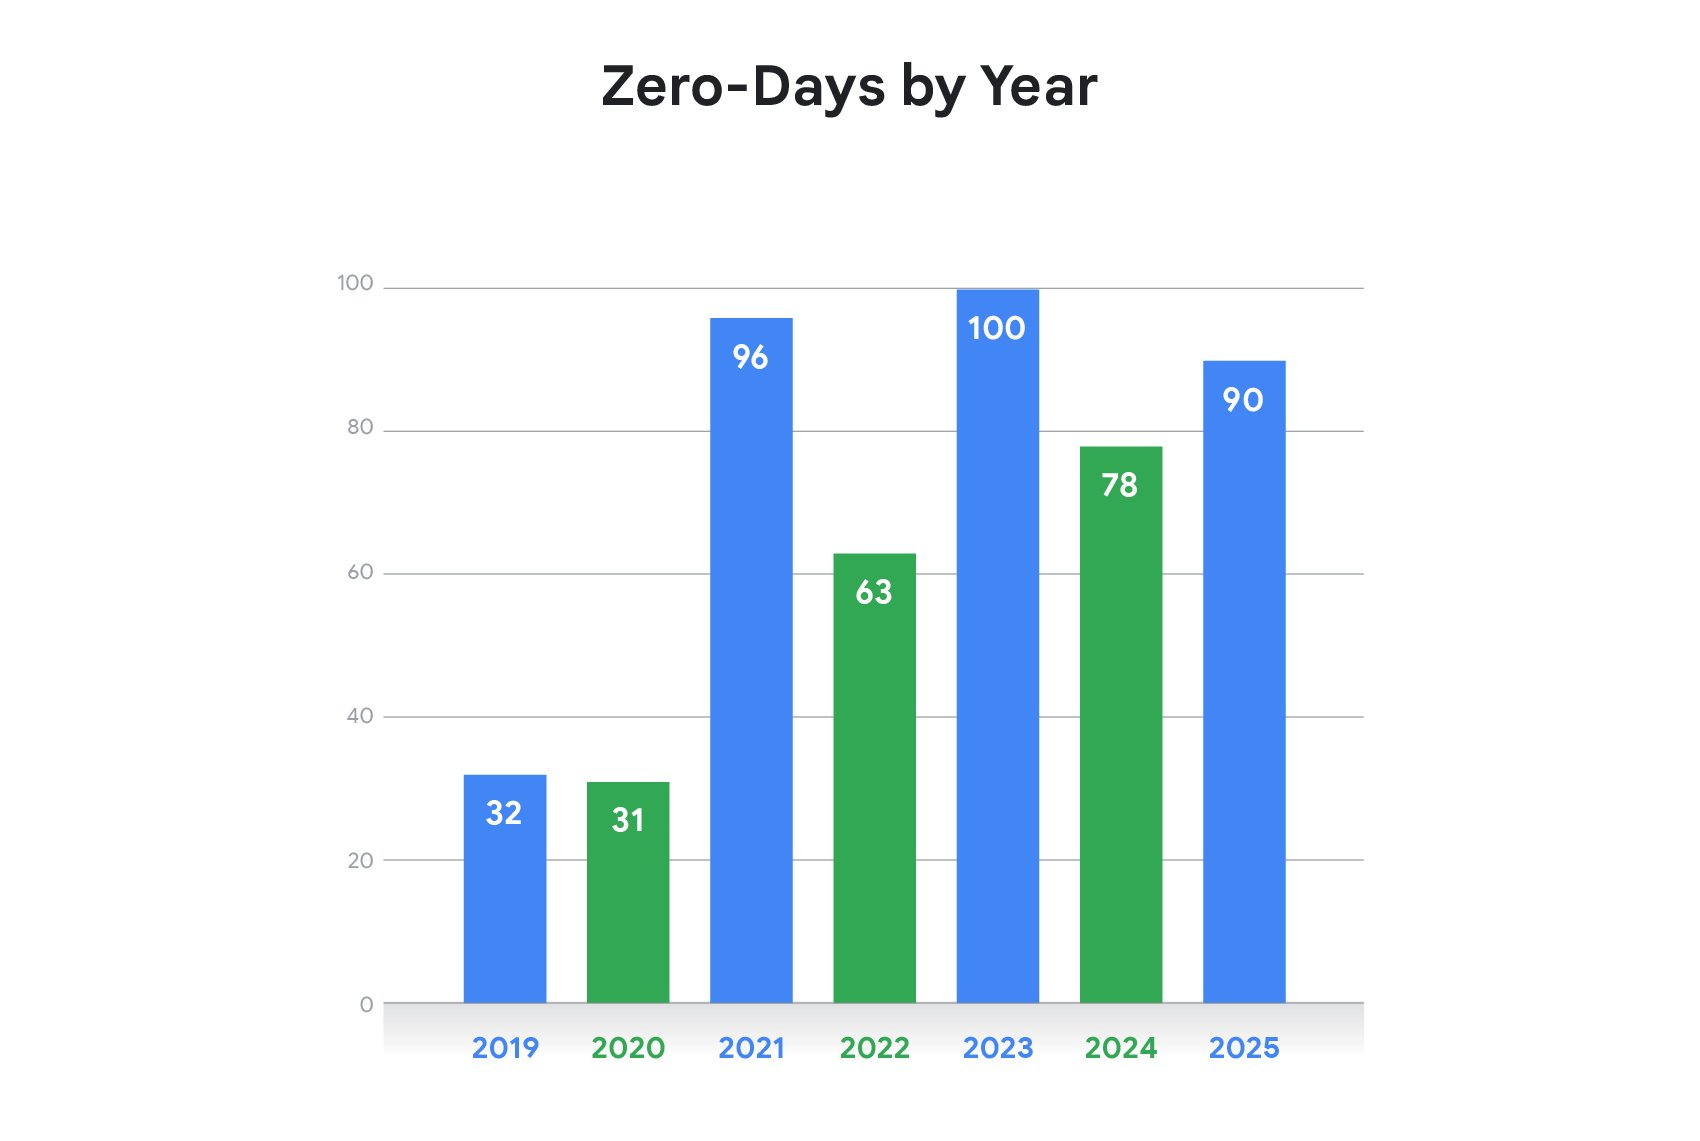
Google’s GTIG reports 90 zero-day vulnerabilities exploited in the wild in 2025, up from 78 in 2024, with a growing share targeting enterprise systems. Google’s Threat Intelligence Group (GTIG) identified 90 zero-day vulnerabilities exploited in the wild in 2025. While slightly below the 100 observed in 2023, the number increased from 78 in 2024, with […]