


 Pierluigi Paganini
 July 05, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Hijacked npm Packages Use Novel VSCode Autorun and Blockchain Dead Drops to Deploy a Credential/Crypto Stealer Building a CI/CD pipeline for Sigma rules Inside StegoAd: How a Threat Actor Evolved to Fuel Silent Ad […]
 Pierluigi Paganini
July 01, 2026
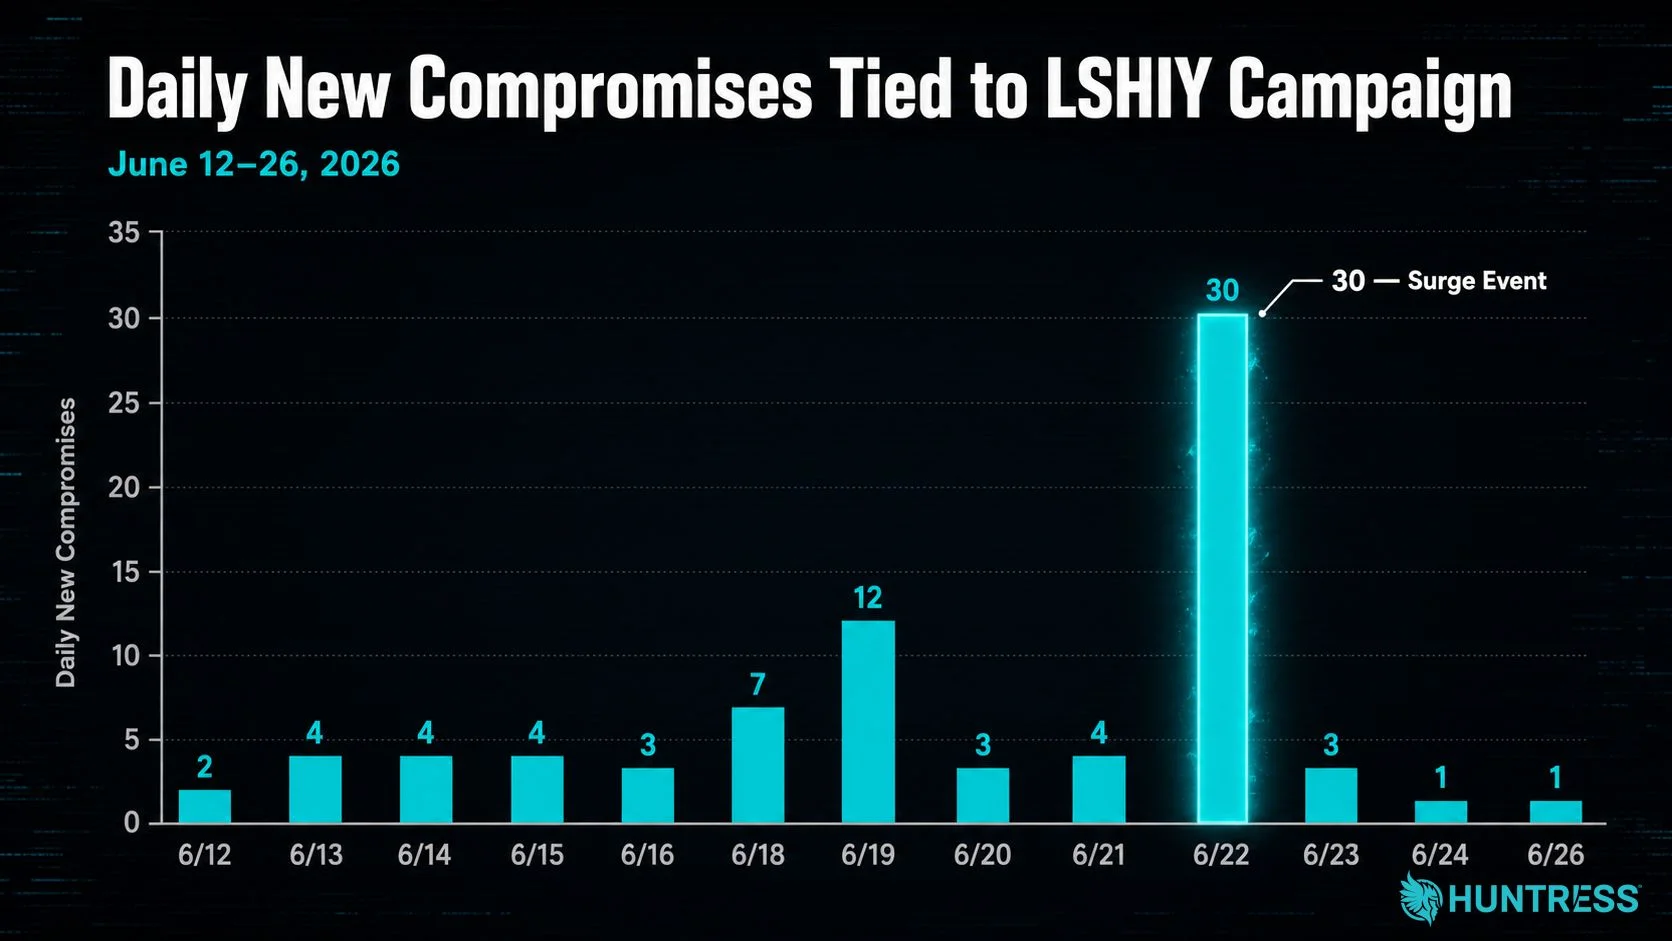
81 Million Login Attempts, 78 Compromised Accounts: The LSHIY Password Spray Hitting Azure CLI Huntress researchers have been tracking a massive automated password spray campaign against Microsoft Azure CLI environments since June 12, 2026. A password spray attack is when attackers try a small number of common passwords across many accounts instead of many passwords […]
 Pierluigi Paganini
June 27, 2026
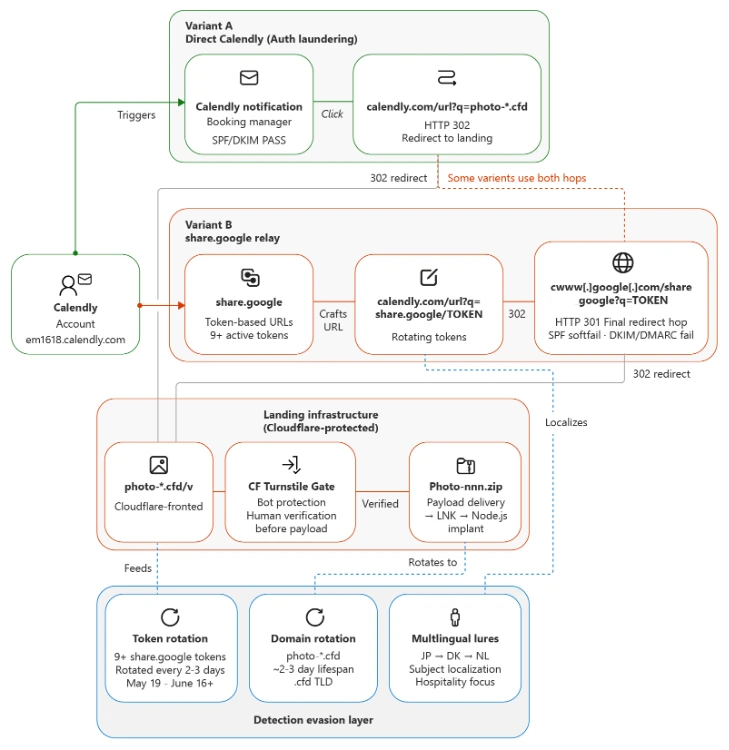
Microsoft warns of a phishing campaign targeting the hospitality sector with fake guest emails that install TonRAT using resilient persistence. Microsoft Threat Intelligence published a detailed analysis on an ongoing hacking campaign against hospitality organizations that has been running since April 2026. The targets are specific: device names observed across compromised environments include strings like […]
 Pierluigi Paganini
June 27, 2026
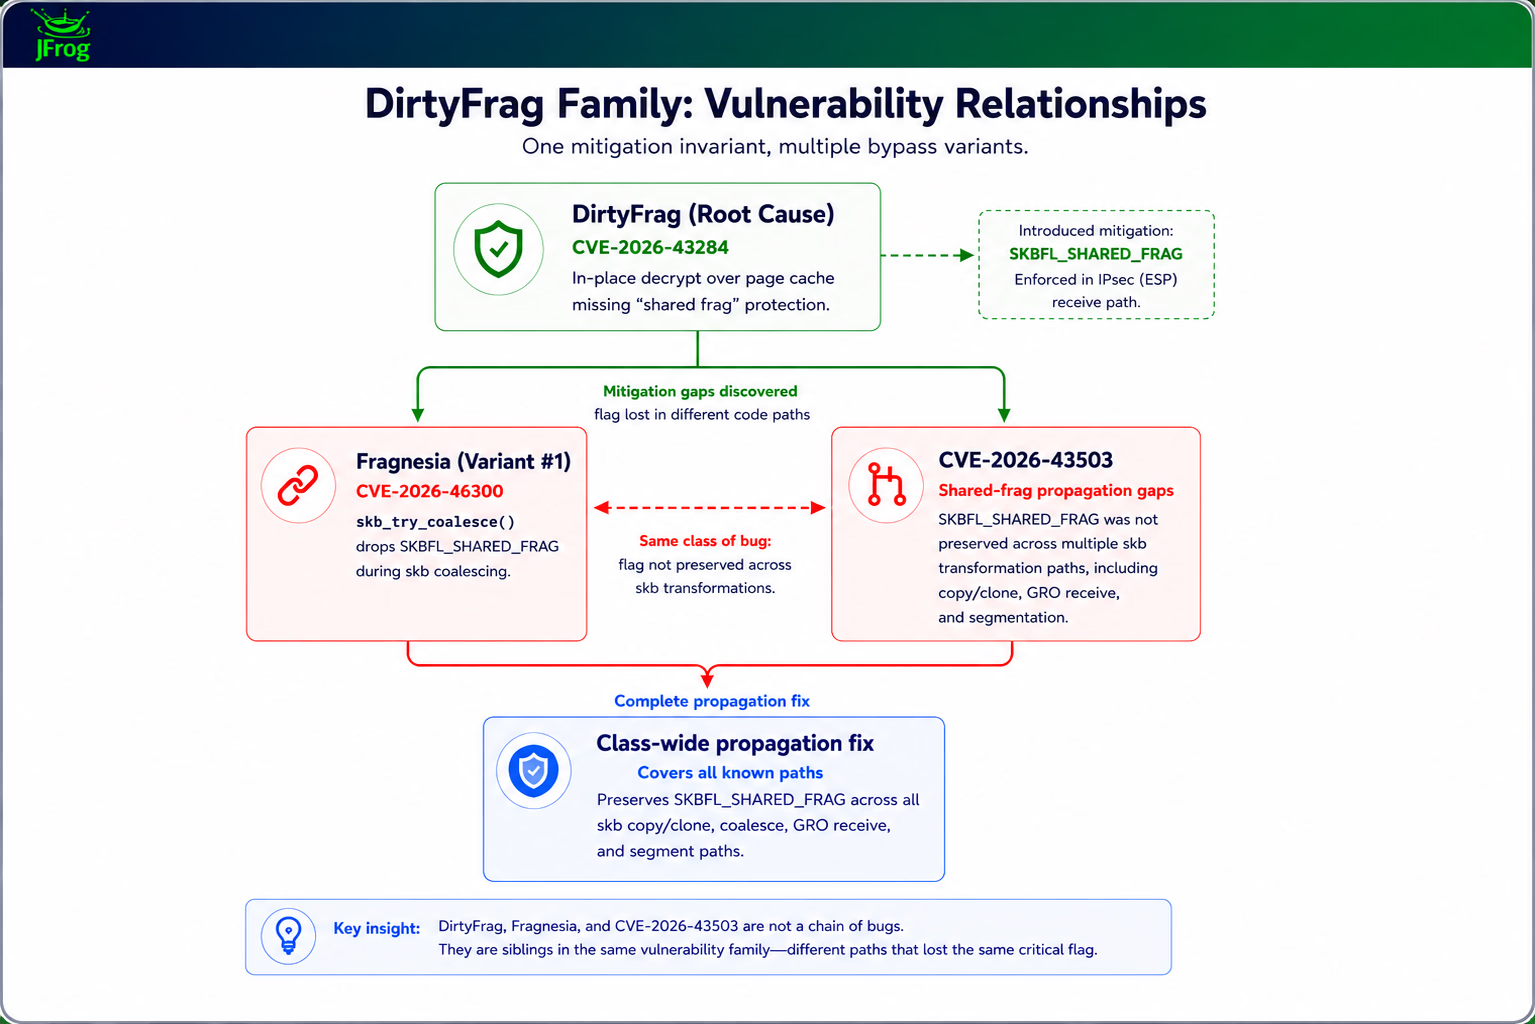
DirtyClone: a Linux kernel privilege escalation that silently rewrites executables in memory, leaving no disk trace. Patch now. JFrog Security Research published a working exploit walkthrough on June 25 for CVE-2026-43503 (CVSS score of 8.8), a Linux kernel privilege escalation they call DirtyClone. It’s the fourth vulnerability in the DirtyFrag family, all sharing the same […]
 Pierluigi Paganini
June 18, 2026
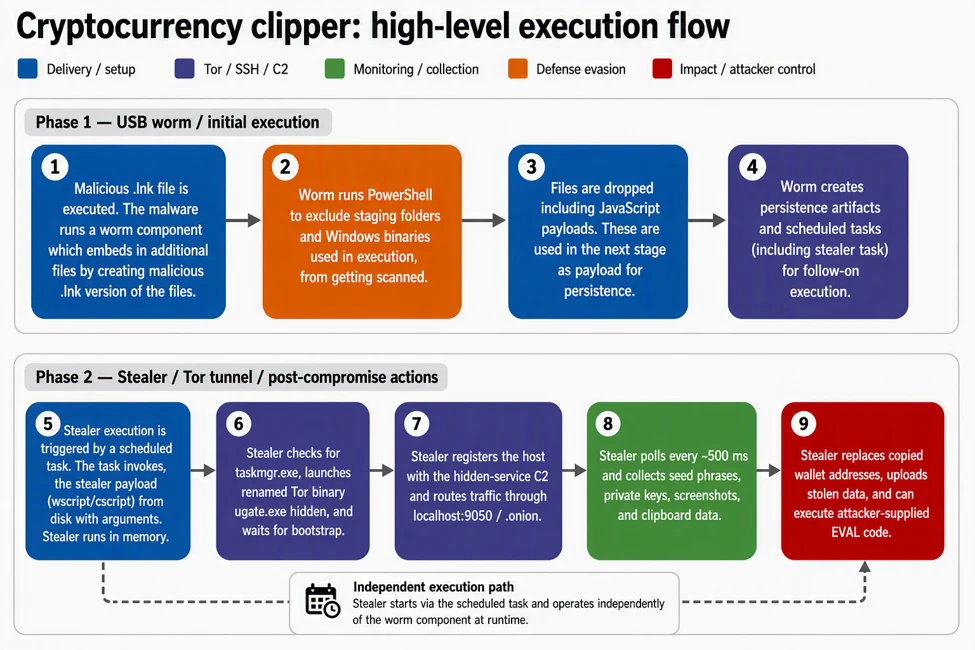
USB .lnk malware steals crypto via clipboard hijack, replaces wallet addresses, steals seed phrases, and screenshots. Microsoft Threat Intelligence has been tracking a clipboard-stealing malware (Clipper) campaign since February 2026 that targets cryptocurrency wallets. A clipper is a type of malicious software that monitors and manipulates your clipboard, the temporary memory where data is stored […]
 Pierluigi Paganini
June 12, 2026
Pro-Iran group Handala breached Cal Water via an exposed GPS tool, reaching billing data for 2M customers. 5GB leaked. On June 11, 2026, the Iran-linked threat group Handala posted a claim on its blog that it had compromised California Water Service, known as Cal Water, and published a 5GB proof-of-concept data dump to back it […]
 Pierluigi Paganini
May 30, 2026
Cybercrime group ShinyHunters leaked data allegedly stolen from Charter Communications, exposing millions of customer records after a failed extortion attempt. The ShinyHunters extortion group has published data allegedly stolen from Charter Communications after the company apparently refused to pay a ransom. Charter Communications is one of the largest telecommunications companies in the United States. It […]
 Pierluigi Paganini
May 28, 2026
Carnival disclosed a data breach affecting nearly 6 million people after hackers used social engineering to access employee accounts. Carnival Corporation is notifying nearly 6 million people after a data breach exposed personal information. According to the notification shared with the Maine Attorney General’s Office, the total number of persons affected is 5,995,277. The company said […]
 Pierluigi Paganini
May 24, 2026
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds a flaw in Drupal Core to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added a flaw in Microsoft Exchange Server, tracked as CVE-2026-9082 (CVSS score of 9.8), to its Known Exploited Vulnerabilities (KEV) catalog. Drupal issued a highly critical security patch on May […]
 Pierluigi Paganini
May 20, 2026
DirtyDecrypt (CVE-2026-31635): working PoC out for a Linux kernel LPE flaw. Missing COW guard in rxgk_decrypt_skb lets local attackers reach root. After Copy Fail, Dirty Frag, and Fragnesia, here comes DirtyDecrypt, another local privilege escalation vulnerability in the kernel, this time with a working proof-of-concept already out in the open. The flaw was discovered and […]

Security / October 08, 2026

