 Pierluigi Paganini
 October 03, 2026
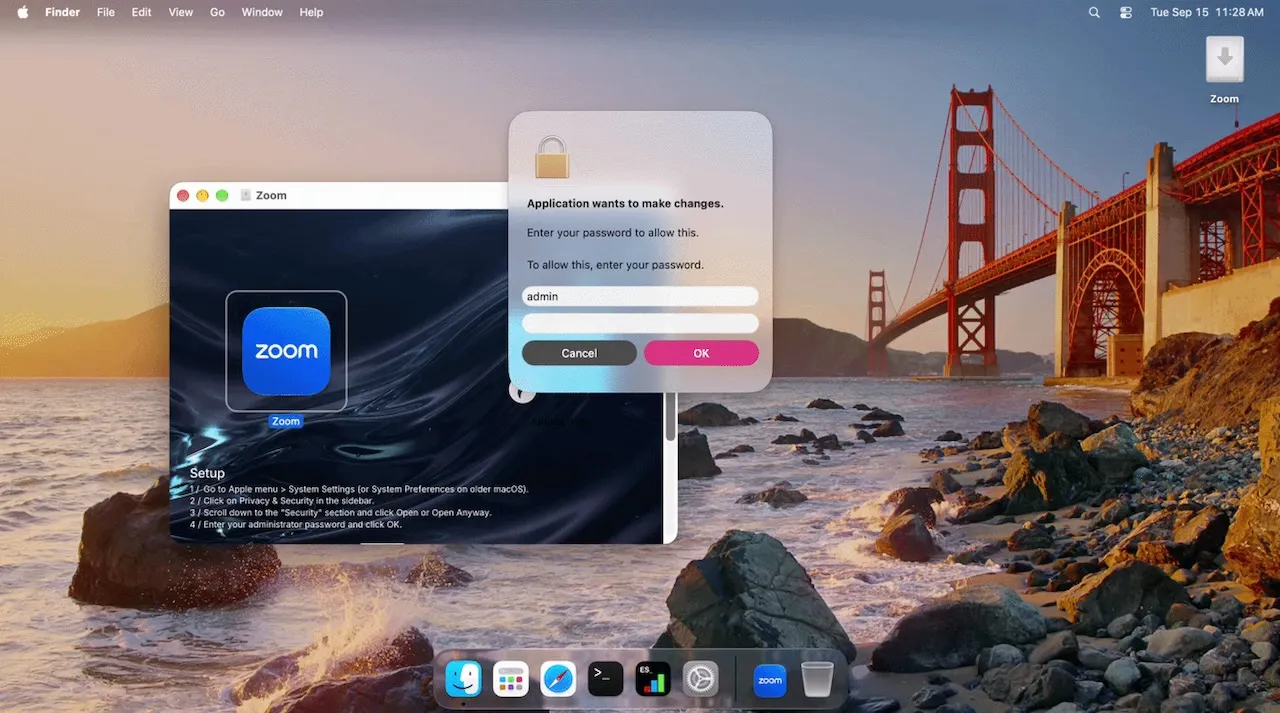
Jamf Threat Labs details CloudSyncD, a fake macOS Zoom installer that hides a phished password using invisible zero-width Unicode characters. Jamf Threat Labs found CloudSyncD while doing routine scanning on VirusTotal, buried inside a disguised Zoom client. They first spotted it on September 15, clearly still under construction, and within two days watched it move […]
 Pierluigi Paganini
October 03, 2026
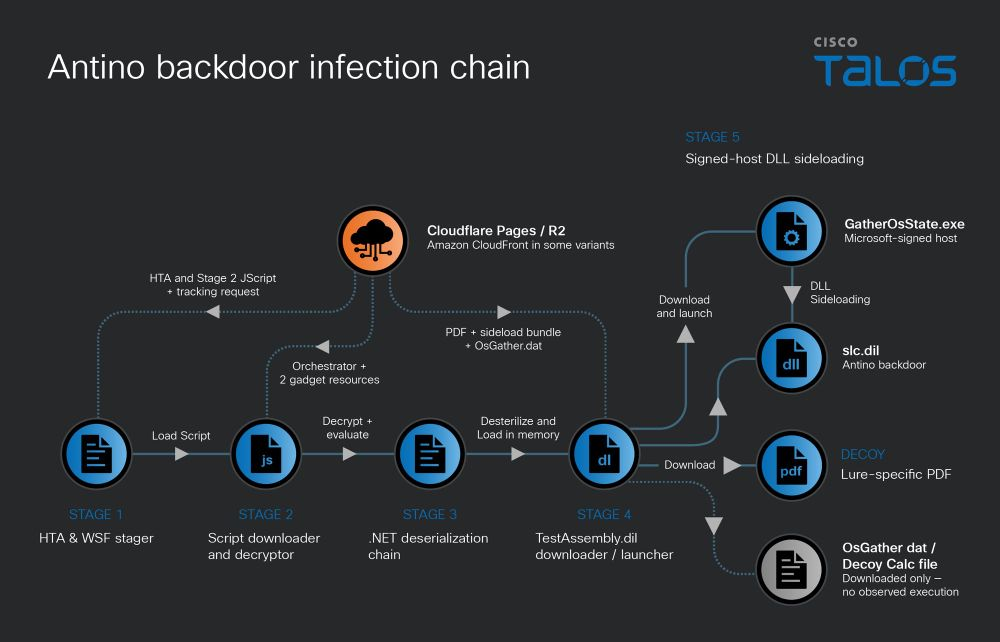
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight […]
 Pierluigi Paganini
September 08, 2026
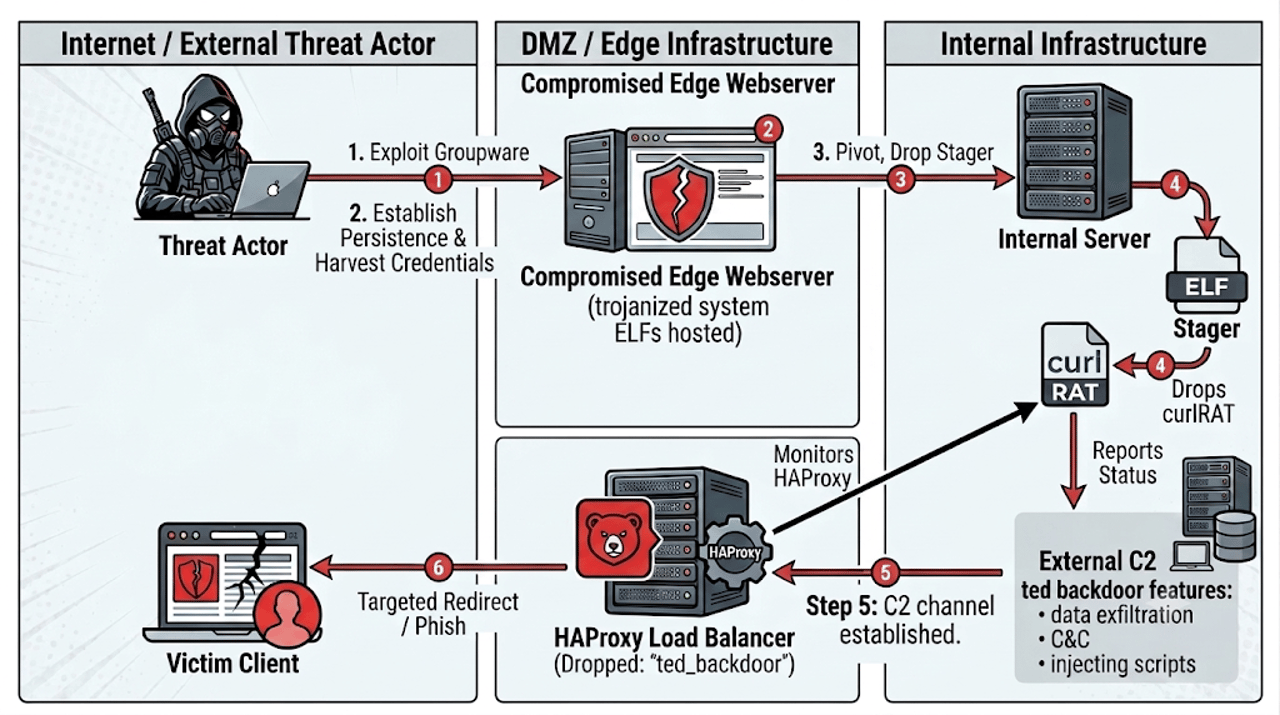
North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally. North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s […]
 Pierluigi Paganini
September 07, 2026
StyleSmuggler Magento zero-day is under active attack, letting unauthenticated attackers execute code and install backdoors on stores that may already be patched. A new zero-day flaw, dubbed StyleSmuggler, in Magento and Adobe Commerce is under active attack, giving unauthenticated attackers a path to run code on vulnerable online stores. Sansec researchers say it affects current […]
 Pierluigi Paganini
August 07, 2026
A hidden backdoor in 20 router models lets remote servers execute commands as root, putting affected devices at risk of takeover. Jacob Baines had a router on his desk that kept trying to call home, and it wasn’t supposed to. VulnCheck researchers found a backdoor baked into Zbtlink routers, and it’s not the kind of […]
 Pierluigi Paganini
July 10, 2026
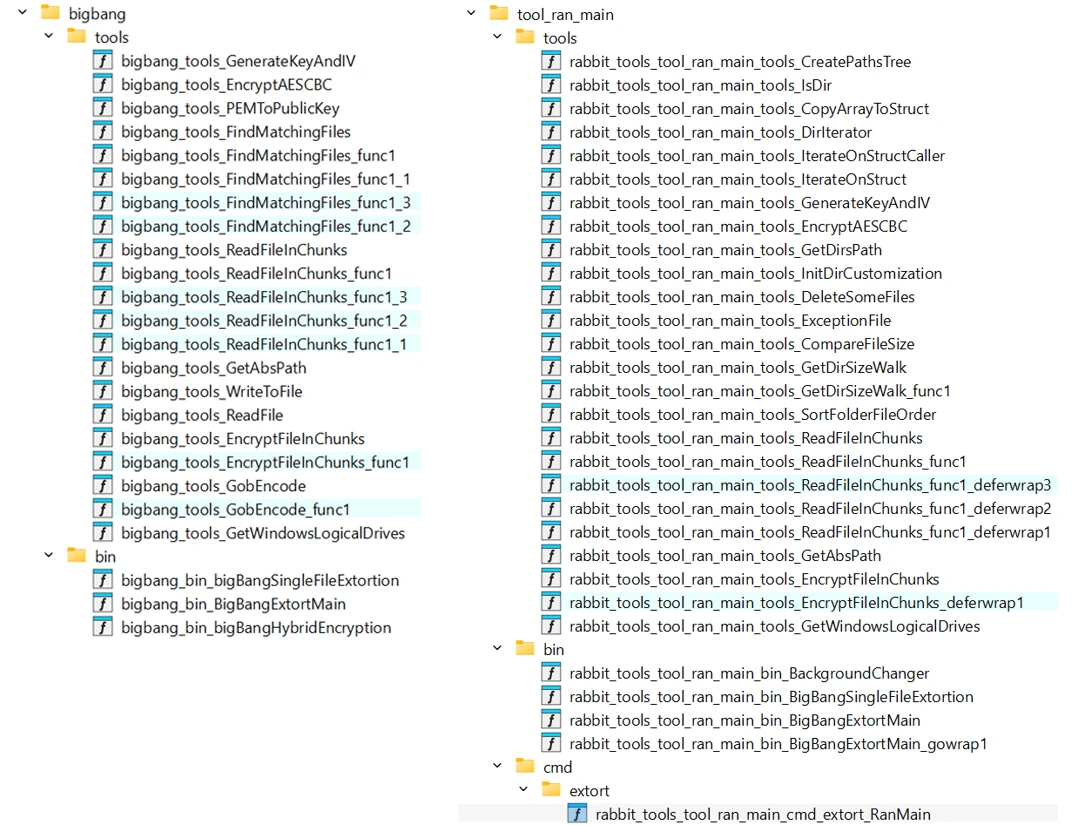
Microsoft uncovered GigaWiper, a modular Go backdoor combining three malware families with espionage, remote control, and destructive wiping features. In October 2025, Microsoft’s threat intelligence team identified destructive wiping activity inside compromised environments and traced it to a previously unknown piece of malware they’re now calling GigaWiper. The malicious code is written in Go, it […]
 Pierluigi Paganini
June 17, 2026
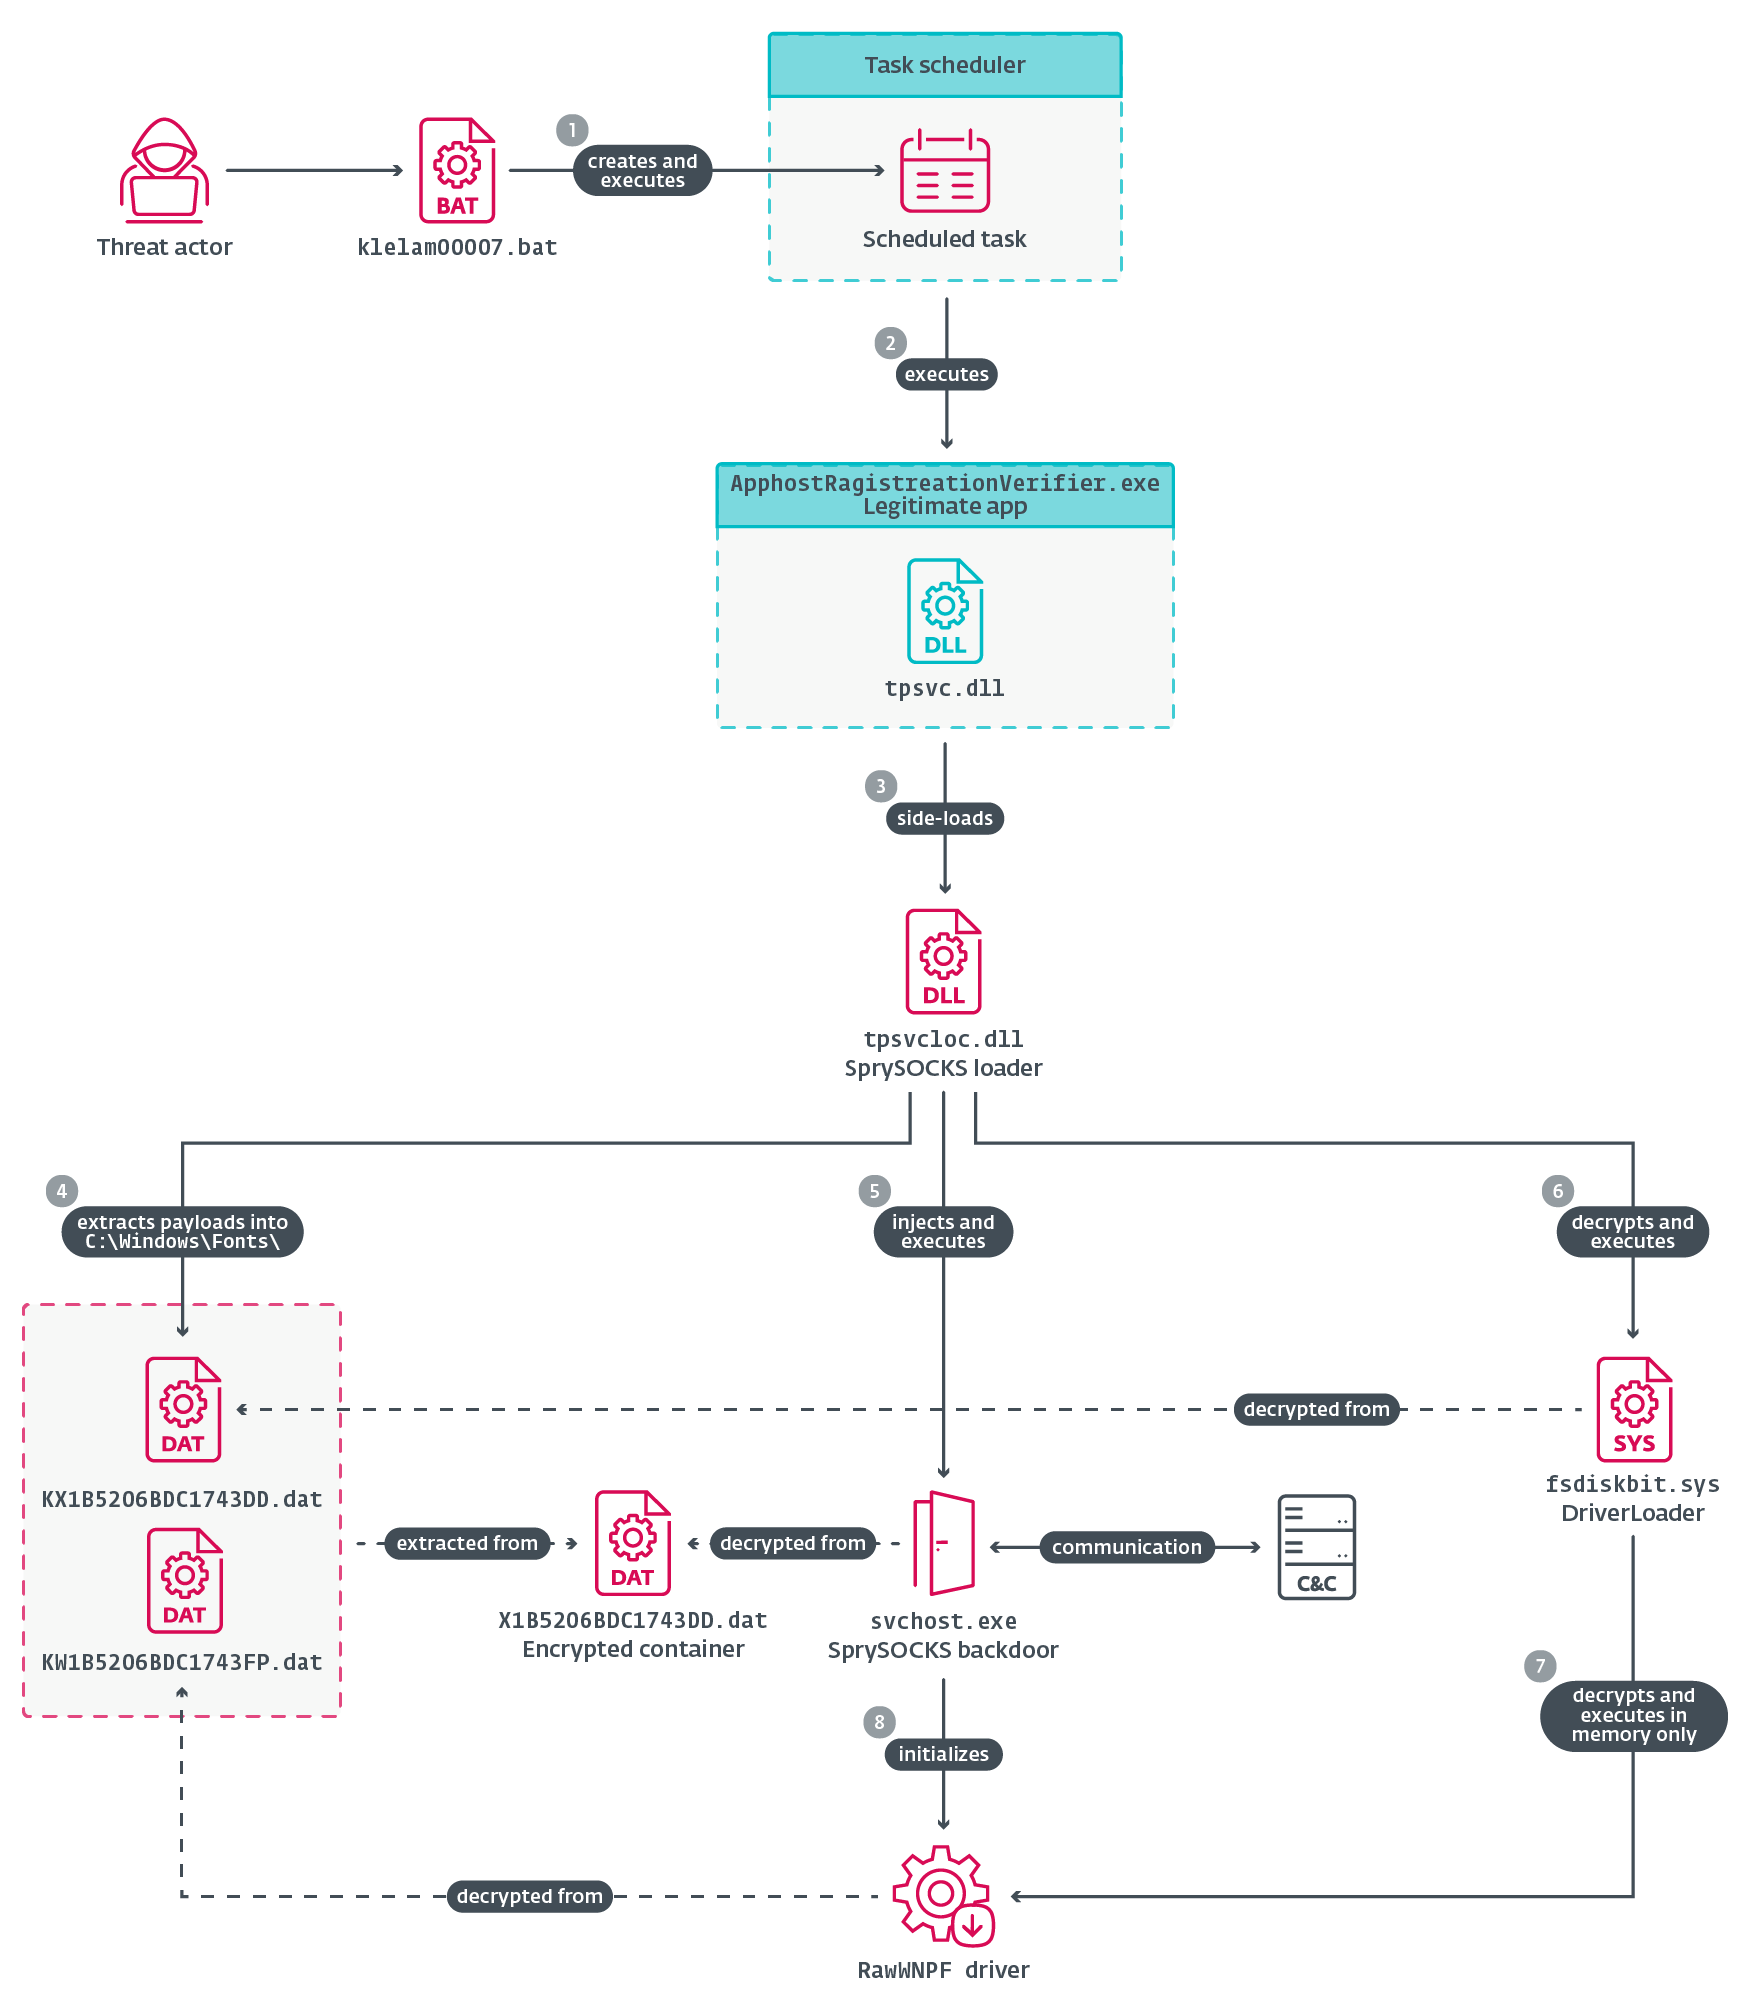
China-linked FishMonger used two SprySOCKS Windows variants that leveraged kernel drivers and the Print Spooler to target governments in four countries. ESET researchers have found two previously undocumented Windows versions of SprySOCKS, a backdoor that the security community had until now treated as Linux-only. Trend Micro first documented the Linux variant in September 2023 and […]
 Pierluigi Paganini
February 18, 2026
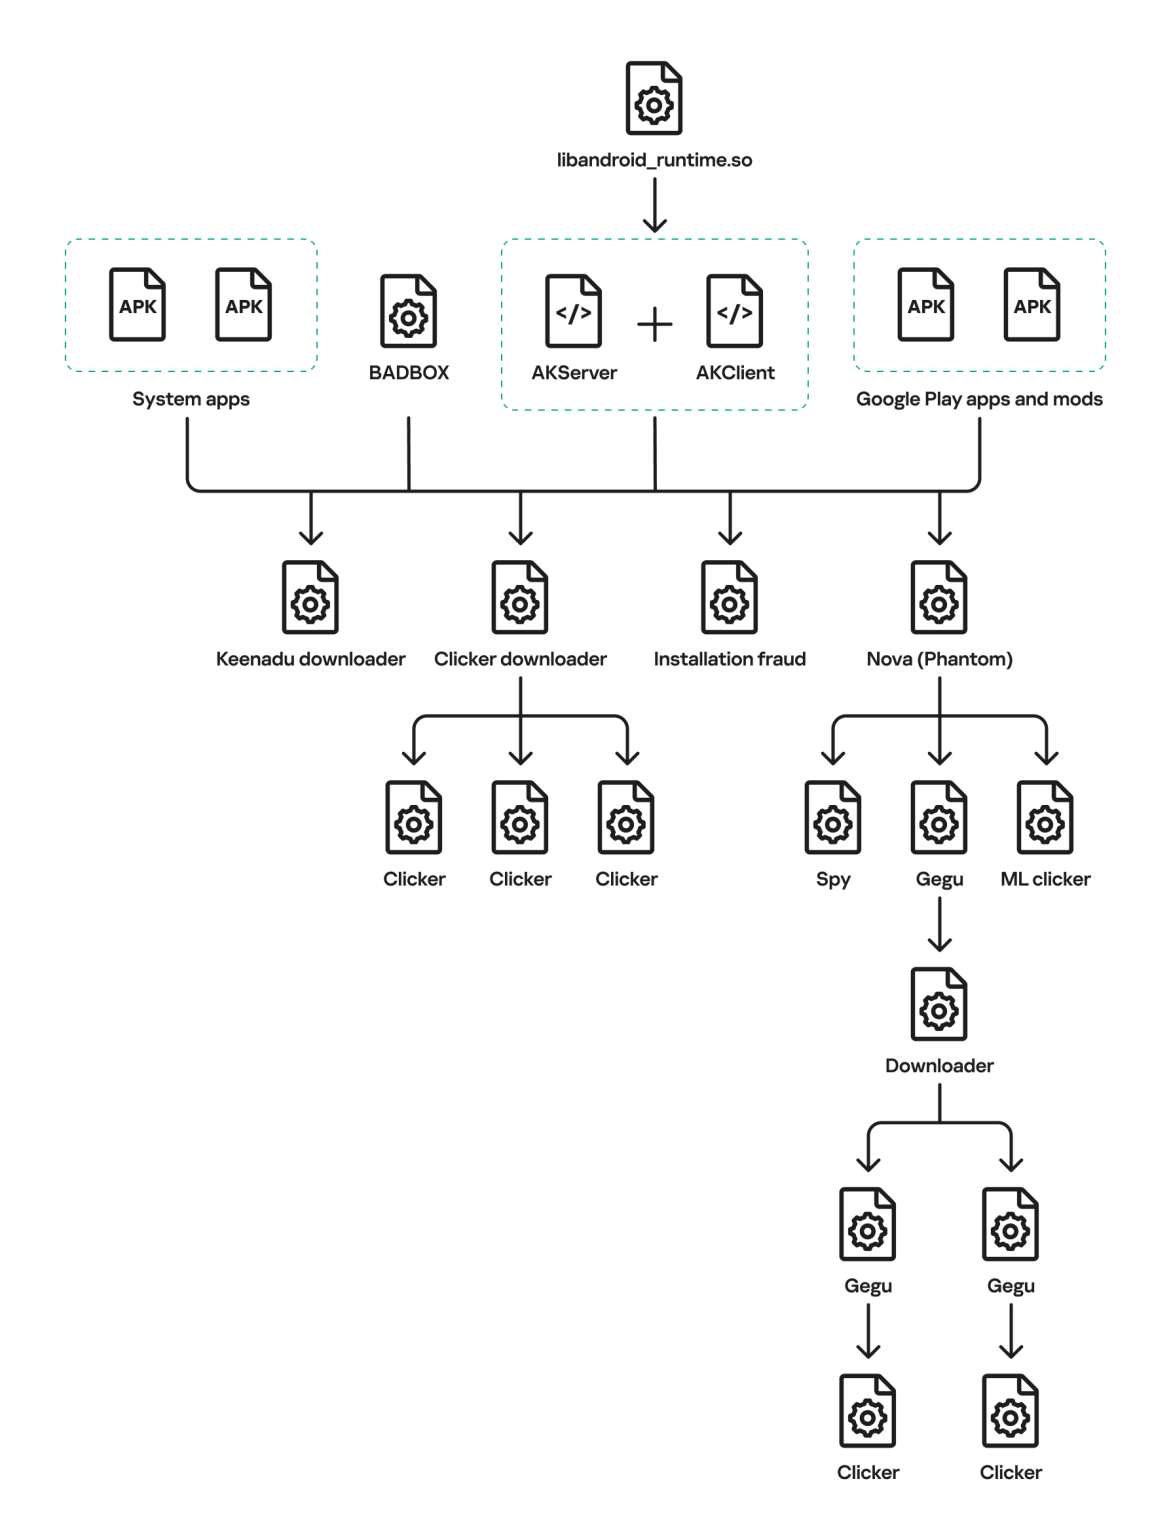
Kaspersky uncovered Keenadu, an Android backdoor used for ad fraud that can even take full control of devices. Kaspersky has identified a new Android malware called Keenadu. It can be preinstalled in device firmware, hidden inside system apps, or even distributed via official stores like Google Play. Currently used for ad fraud by turning infected […]
 Pierluigi Paganini
November 04, 2025
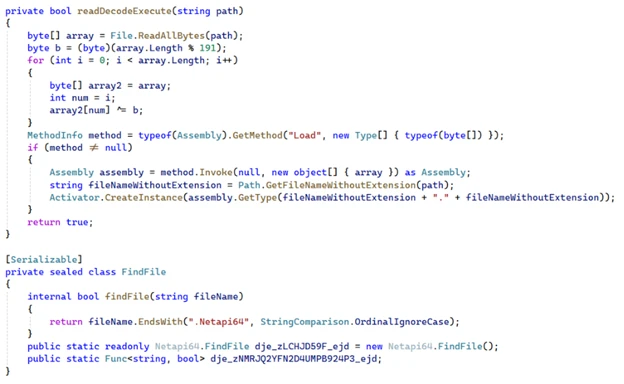
Microsoft found a new backdoor, SesameOp, using the OpenAI Assistants API for stealthy command-and-control in hacked systems. Microsoft uncovered a new backdoor, named SesameOp, that abuses the OpenAI Assistants API for command-and-control, allowing covert communication within compromised systems. Microsoft Incident Response – Detection and Response Team (DART) researchers discovered the backdoor in July 2025 while […]
 Pierluigi Paganini
August 02, 2025
China questioned Nvidia over suspected backdoors in its H20 chips, adding to rising tensions in the tech fight between the U.S. and Beijing. China’s internet watchdog has summoned Nvidia over concerns that its H20 AI chips may contain hidden backdoors. Nvidia H20 chips are AI GPUs tailored for the Chinese market, based on Hopper architecture. […]