 Pierluigi Paganini
 August 31, 2026
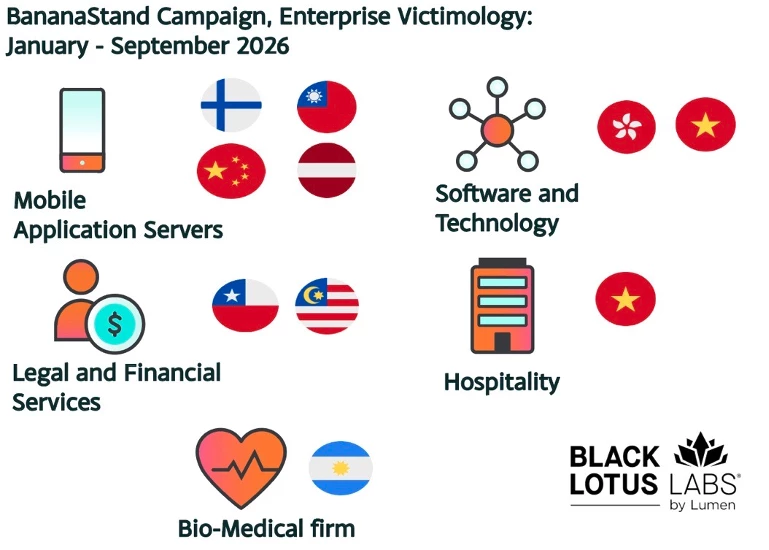
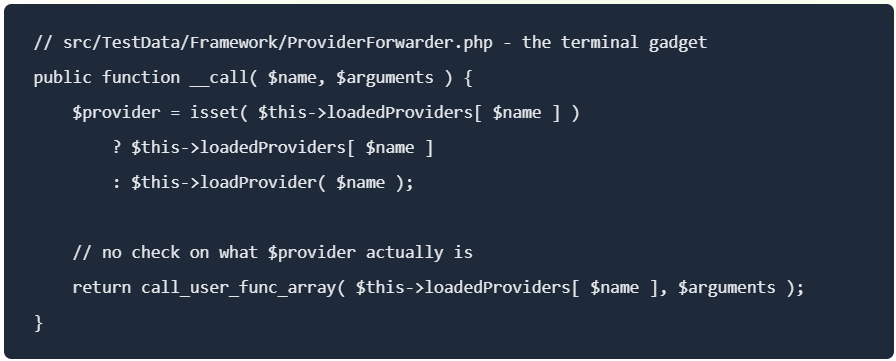
A critical GiveWP flaw lets unauthenticated attackers execute server commands. Version 4.16.7.2 fixes the PHP object injection chain. A critical vulnerability in GiveWP, one of the most widely used WordPress plugins for online donations and fundraising, can let an unauthenticated attacker execute commands on the server. Patchstack disclosed the flaw on August 28, after researcher […]
 Pierluigi Paganini
August 30, 2026
Extortion group FulcrumSec claims they stole 86GB of Manchester Airports Group data after finding API credentials exposed in client-side JavaScript. Manchester Airports Group (MAG) disclosed a data breach on August 27 affecting customers of Manchester, London Stansted, and East Midlands airports. Two days later, BleepingComputer reports the extortion group FulcrumSec claimed responsibility, saying it stole […]
 Pierluigi Paganini
August 30, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter Operation QUICSILVER: China-Nexus Actor Targets Myanmar Diplomats via VHD-Delivered Go Backdoor FTP Banners: The New Dead Drop Resolver Delivering Novel RATs The State of AI-Enabled Malware August 2026: From Brand Abuse to Agentic […]
 Pierluigi Paganini
August 30, 2026
PaperCut servers are under active attack, while 47% of tracked installations still run unpatched versions vulnerable to remote code execution. PaperCut, the print management software running in schools, hospitals, and offices worldwide, confirmed on August 27 that a pre-authentication remote code execution flaw is being actively exploited against real customers. Researchers at Huntress found evidence […]
 Pierluigi Paganini
August 30, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Hack One Robot, Reach the Next: Unitree G1 Security Flaws Rhysida Ransomware Group Targets Berlin Government Ahead […]
 Pierluigi Paganini
August 29, 2026
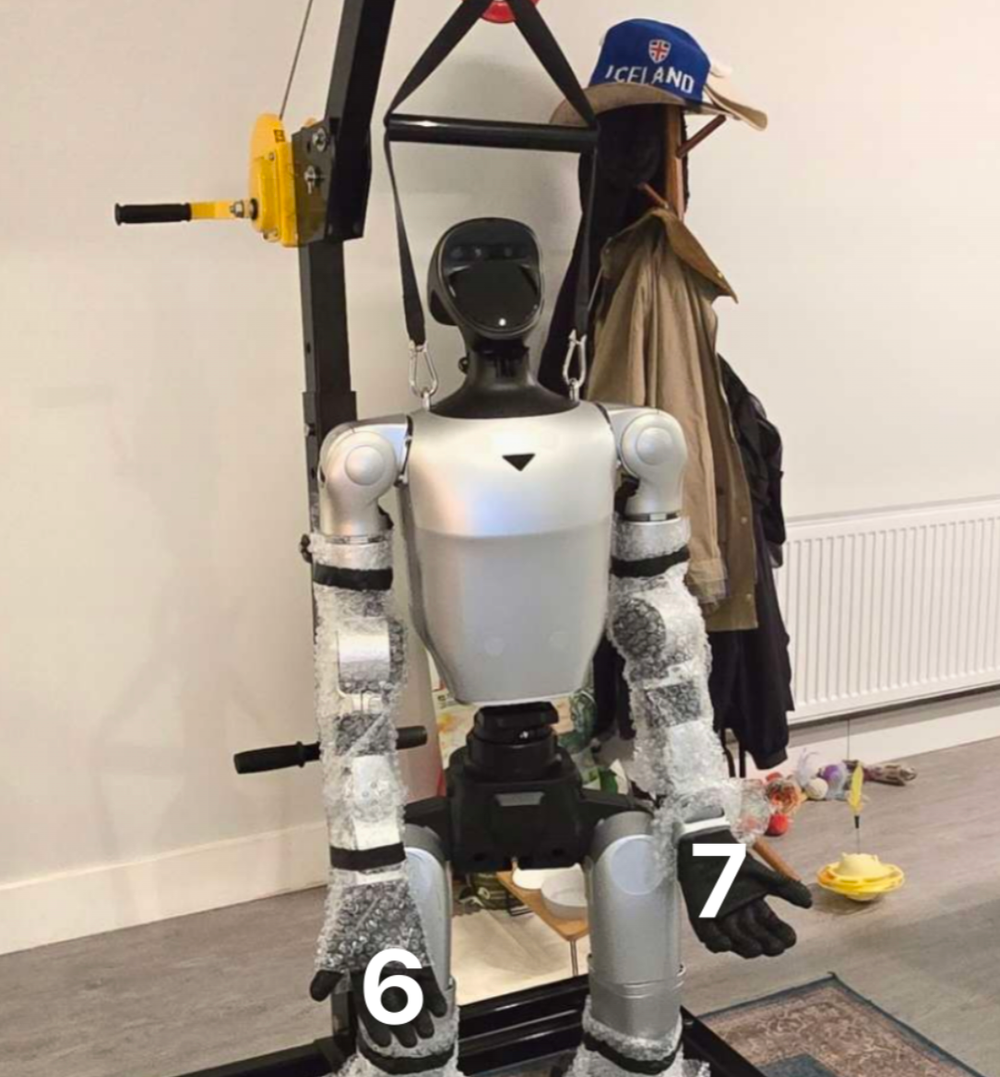
A researcher chained two Unitree G1 flaws to gain root access remotely and showed how a compromised robot could attack others nearby. Security researcher Olivier Laflamme spent about three months digging into the Unitree G1 humanoid robot and eventually found a way to fully compromise it without plugging in a single cable. In his technical […]
 Pierluigi Paganini
August 29, 2026
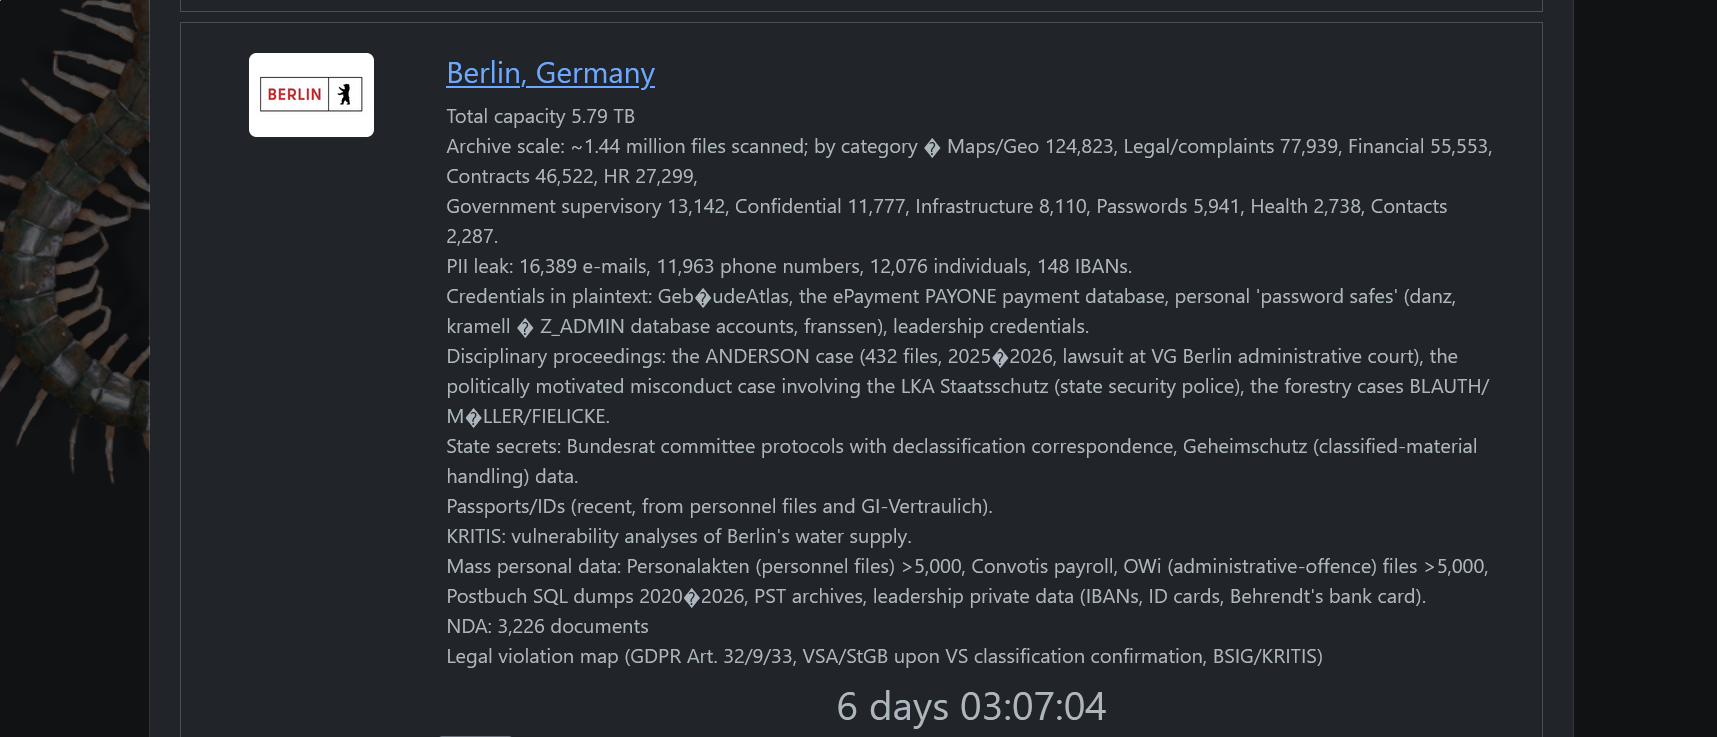
Berlin ‘s government faces a Rhysida ransomware attack weeks before elections, with officials refusing to pay despite a claimed 5.79 TB data theft. Berlin’s state government confirmed this week it’s dealing with an extortion attempt following an August cyberattack on the city-state’s administrative network, and officials have already refused the requested ransom. The ransomware group […]
 Pierluigi Paganini
August 29, 2026
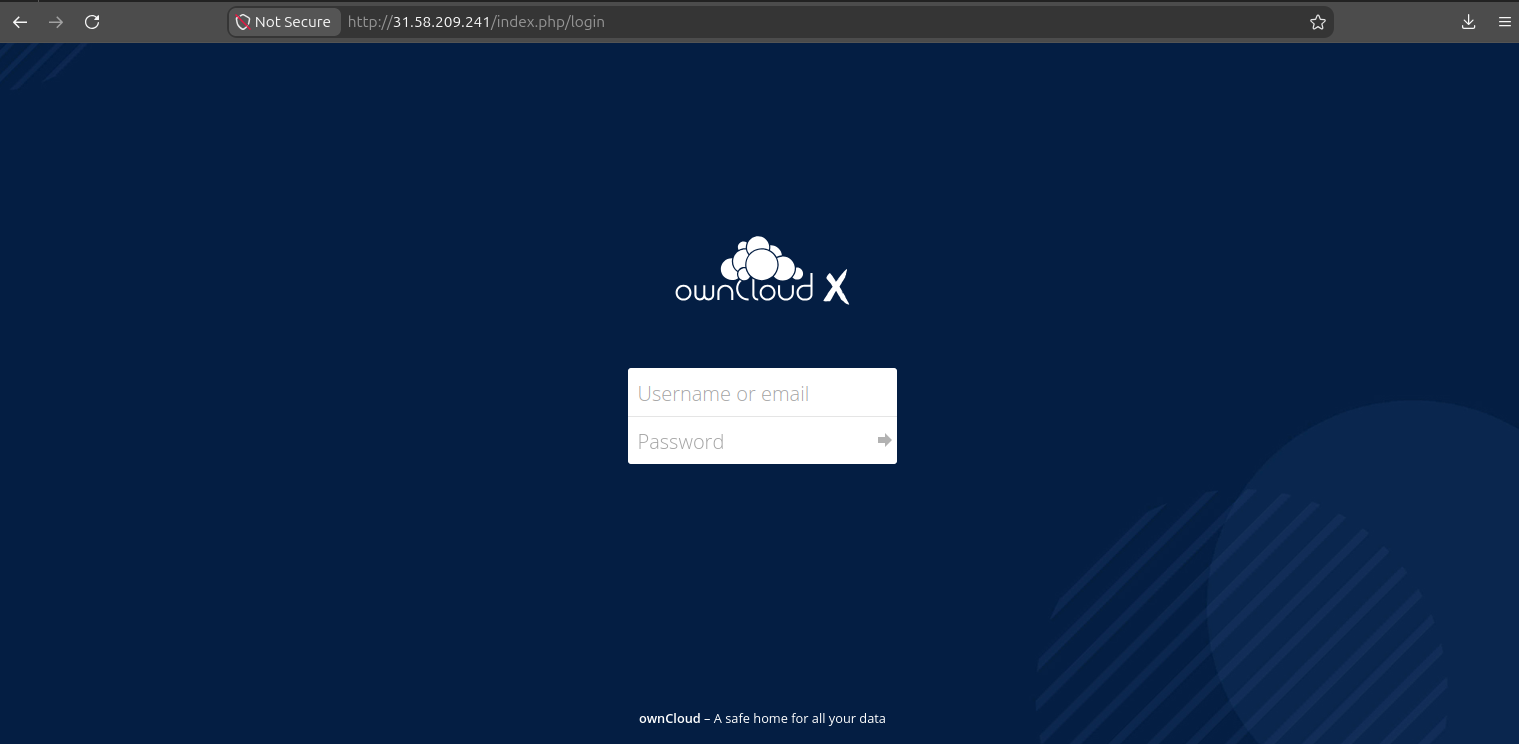
An alleged Chinese-speaking actor breached Philippine nuclear and naval targets by exploiting known flaws, stealing sensitive data. A suspected Chinese-speaking operator targeted a Philippine nuclear research body and a marine engineering company that supports the Philippine Navy, using well-known vulnerabilities in internet-facing ownCloud and WordPress systems. The activity was uncovered after Hunt.io found an exposed […]
 Pierluigi Paganini
August 28, 2026
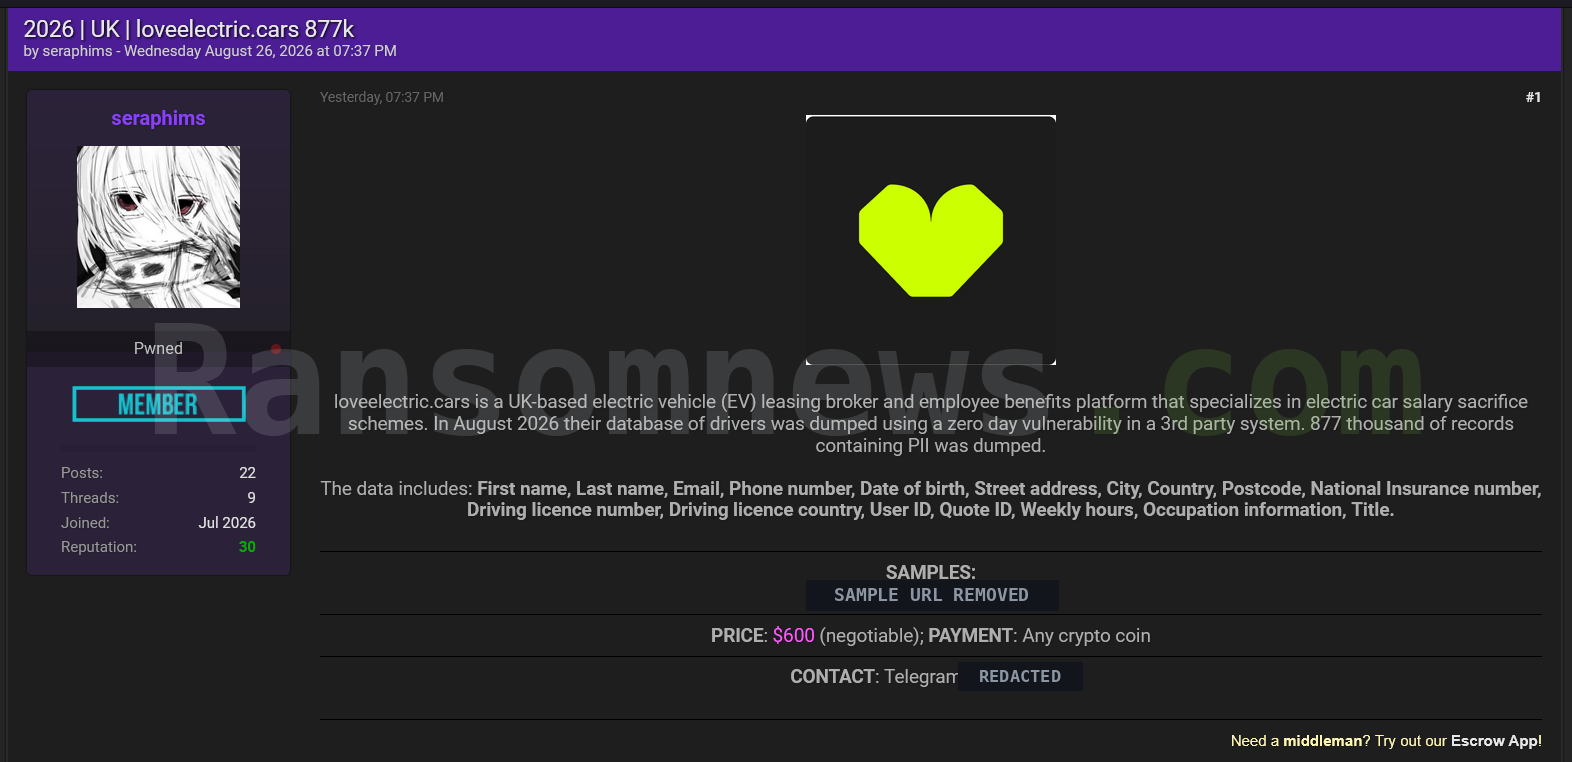
Love Electric’s alleged data breach exposes sensitive driver data and highlights the identity risks created by third-party salary sacrifice providers. A seller on an English-language data-breach forum claimed on August 26 that they had obtained the driver database of Love Electric, a UK broker that runs electric-vehicle salary sacrifice schemes. The seller, operating under the […]
 Pierluigi Paganini
August 28, 2026
Trump targets foreign-made power grid equipment, citing cyber, sabotage and supply-chain risks to U.S. national security. Executive Order 14420, signed on August 26, targets equipment and technologies that could expose the power grid to sabotage, unauthorized access, malicious remote activity or supply-chain disruption. The timing matters. The White House points to the rapid expansion of […]