 Pierluigi Paganini
 September 08, 2026
North Korea-linked hackers hid a backdoor inside HAProxy, masking C2 traffic and stealing data while keeping the load balancer working normally. North Korean-linked hackers found a genuinely clever hiding spot for their malware: inside the actual source code of HAProxy, the load balancing software running at the edge of two South Korean companies’ networks. Rapid7’s […]
 Pierluigi Paganini
September 01, 2026
Huntress found five DPRK-linked workers hired in 2026 using fake identities, remote-access setups and proxy tools to infiltrate legitimate companies. Companies keep accidentally hiring North Korea-linked individuals as remote workers, and Huntress just published the receipts. The security firm’s investigation documents five confirmed cases in 2026 alone where DPRK-aligned workers, tracked under the name FAMOUS […]
 Pierluigi Paganini
August 13, 2026
Lazarus targets defense professionals with fake Lockheed Martin jobs, exploiting a Windows zero-day to deploy backdoors and evade security controls. Check Point Research has uncovered a new wave of Operation Dream Job, the long-running North Korean campaign that lures defense and aerospace professionals with convincing fake job offers. This iteration is more dangerous than previous […]
 Pierluigi Paganini
June 26, 2026
macOS.Gaslight: DPRK Rust implant for Mac with a prompt injection payload designed to fool AI-based malware analysts. SentinelLabs researchers spotted a Rust-based macOS implant, dubbed macOS.Gaslight, that surfaced in early June after an Apple XProtect update pointed to a VirusTotal sample uploaded on May 22. The binary was undetected by static engines at the time […]
 Pierluigi Paganini
May 26, 2026
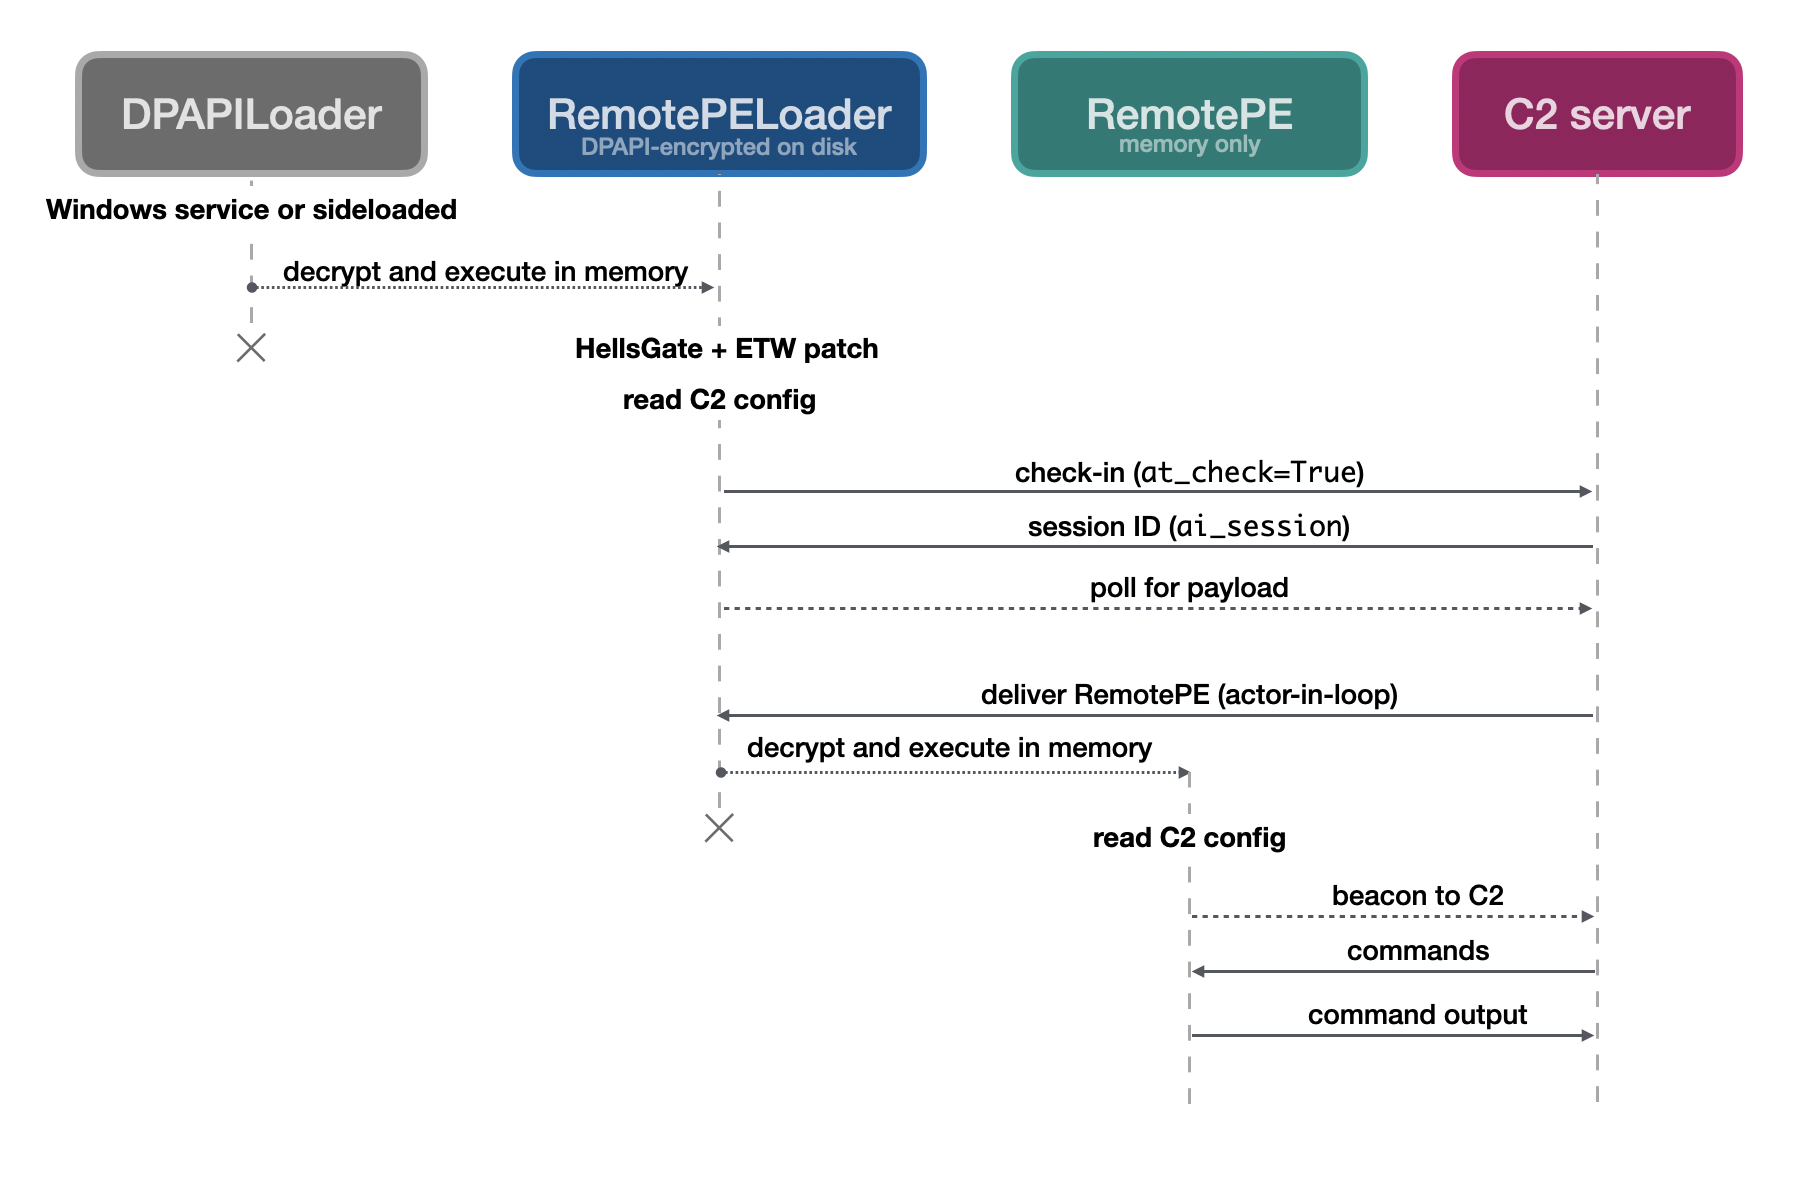
North Korea-linked Lazarus APT Group is using a stealthy memory-only RAT that leaves almost no forensic traces behind. North Korea-linked APT group Lazarus has never been shy about its ambitions, the threat actor has been tied to some of the most audacious financial heists in recent memory, draining hundreds of millions from cryptocurrency exchanges and […]
 Pierluigi Paganini
April 21, 2026
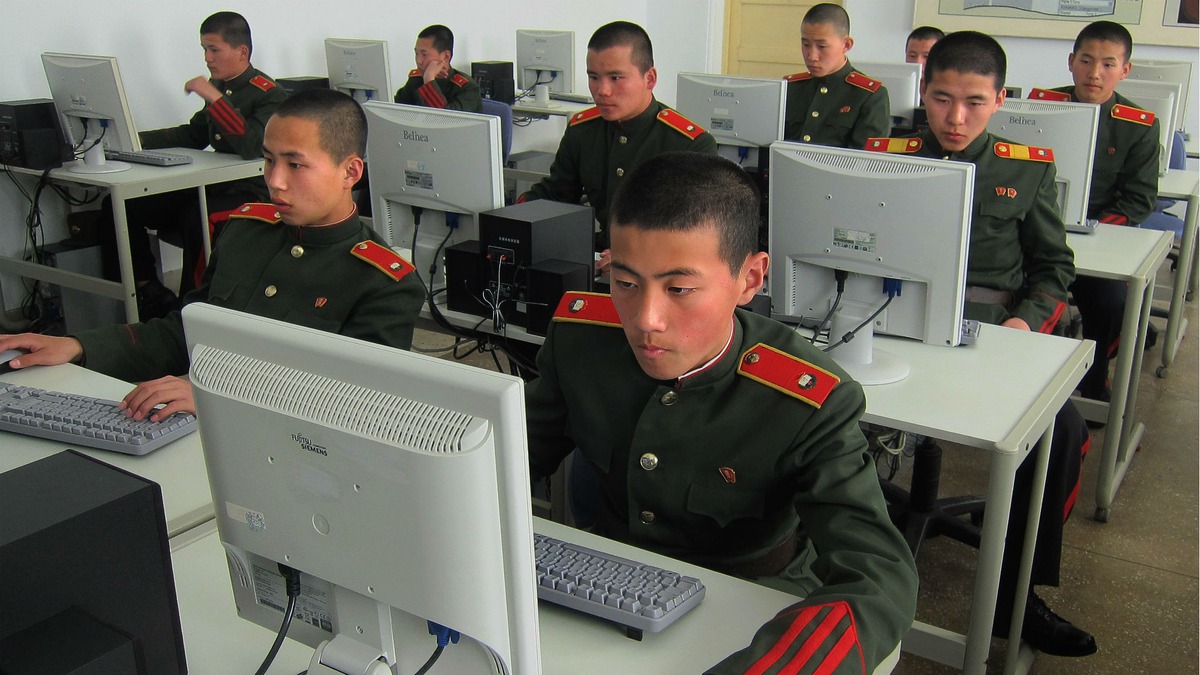
North Korea-linked Lazarus Group stole $290M from Kelp DAO by abusing LayerZero. A second $95M attempt was stopped. Hackers tied to the North-Korea linked group Lazarus APT carried out a $290M crypto theft targeting Kelp DAO. Kelp DAO is a decentralized finance (DeFi) protocol built on the Ethereum ecosystem that focuses on a concept called […]
 Pierluigi Paganini
April 06, 2026
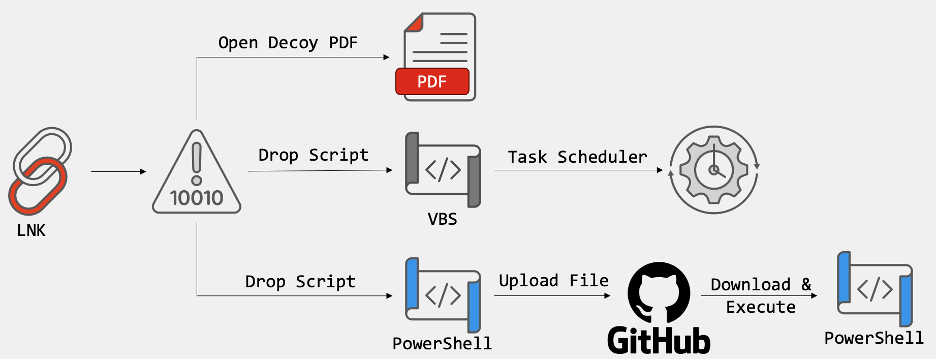
DPRK-linked hackers use GitHub C2s, starting attacks via phishing LNK files that drop a PDF and PowerShell script in South Korea. North Korea-linked threat actors target South Korean organizations using GitHub as C2 servers. The attack chain starts with phishing emails carrying obfuscated LNK files that drop a decoy PDF and a PowerShell script to […]
Pierluigi Paganini
April 03, 2026
Drift lost $285M in a sophisticated attack, likely by North Korea, who used nonce-based tricks to gain control and quickly drain funds Drift suffered a $285 million cryptocurrency heist in a highly sophisticated attack likely linked to North Korea. Threat actors used durable nonce accounts to pre-sign and delay transactions, while also compromising multisig approvals […]
Pierluigi Paganini
April 01, 2026
Google links the Axios npm supply chain attack to North Korean threat group UNC1069, targeting financial gain. Google has attributed the recent Axios npm supply chain compromise to a North Korean threat group tracked as UNC1069. The attack, aimed at financial gain, exploited the package to target developers and organizations relying on Axios. John Hultquist […]
 Pierluigi Paganini
March 24, 2026
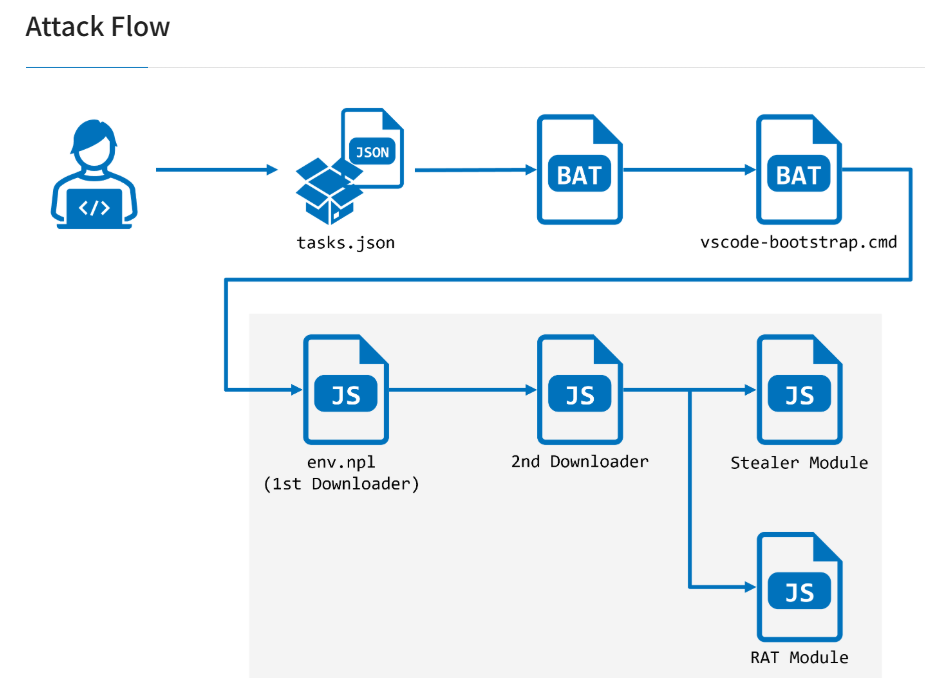
North Korea-linked threat actors use VS Code auto-run tasks to spread StoatWaffle malware via malicious projects that execute on folder open. North Korea-linked threat actor Team 8 behind the Contagious Interview campaign is spreading StoatWaffle malware through malicious Microsoft Visual Studio Code projects. Since late 2025, they have abused the “tasks.json” auto-run feature in Microsoft […]