 Pierluigi Paganini
 March 23, 2017
Chinese scammers are deploying rogue cellphone towers to spread the Android Swearing Trojan via malicious URL in SMS messages. Chinese scammers are deploying fake mobile base stations to spread the Android Swearing Trojan in text messages. The attackers have improved the well-known Smishing attack using rogue cell phone towers as the attack vector and distribute the Android […]
 Pierluigi Paganini
March 20, 2017
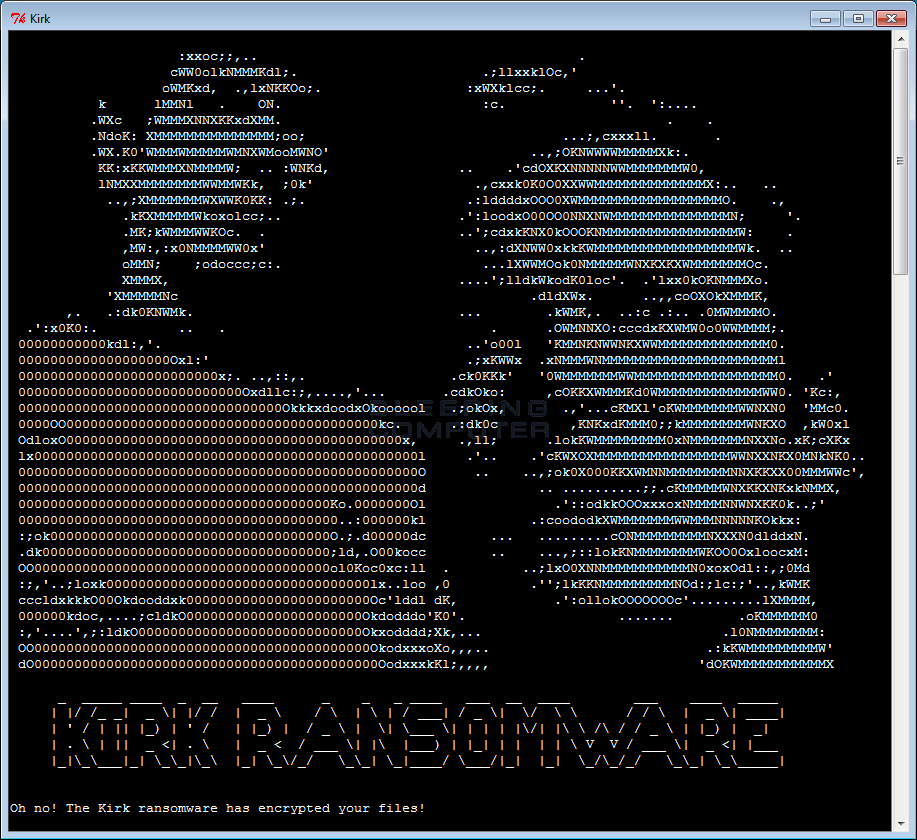
The researchers have discovered a new piece of ransomware featuring a Star Trek theme, dubbed Kirk ransomware, the first one accepting Monero payments. Ransomware continues to be one of the most profitable cyber threats, for this reason, every week we see new strains of malware in the wild. The researchers have discovered a new piece […]
 Pierluigi Paganini
March 19, 2017
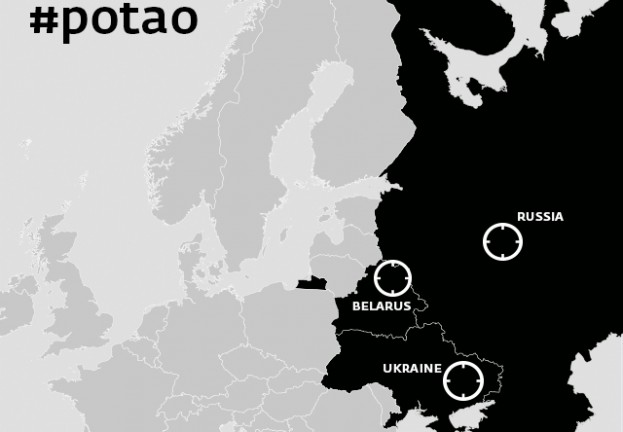
Security experts at Arbor Networks linked a new Acronym malware to the malicious code used by threat actors behind the Operation Potao Express. Security experts at Arbor Networks have spotted a new strain of malware that could be linked to the malicious code used by threat actors behind the Operation Potao Express. The researchers started […]
 Pierluigi Paganini
March 17, 2017
New APT Campaign based on Poison Ivy RAT with C&C in China has been reversed by MalwareMustDie who shared a lot of interesting details about the attack vectors and reverse techniques. Our travel along the great analysis of a fresh, new insidious APT China campaign. An ordinary case of phishing? At the beginning, it seemed […]
 Pierluigi Paganini
March 16, 2017
Trend Micro has discovered a new PoS malware, tracked as MajikPOS, that is targeting business in North America and Canada. Security experts at Trend Micro have discovered a new PoS malware, tracked as MajikPOS, that is targeting business in North America. The experts explained that the MajikPOS has the same capabilities of any other PoS malware, […]
 Pierluigi Paganini
March 15, 2017
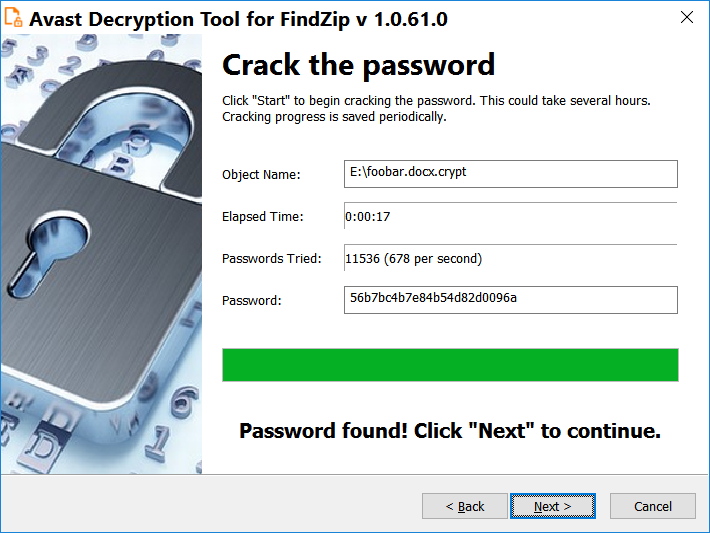
Great news for macOS users who were infected by the FindZip macOS ransomware, Avast released a decryption tool for free. Good news for macOS users who were infected by the FindZip ransomware, now a decryption tool was released online for free. The FindZip macOS ransomware was spotted last month by researchers at ESET, it is […]
 Pierluigi Paganini
March 15, 2017
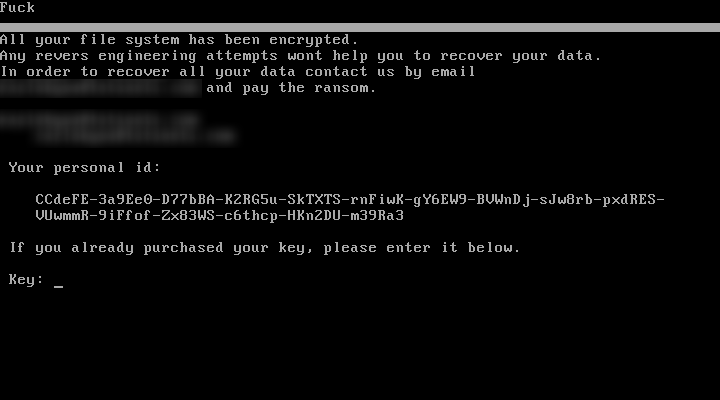
Threat actors in the wild have found the way to hijack the Petya ransomware on the fly and use it in targeted attacks, say welcome to PetrWrap ransomware. The Petya ransomware was first spotted by experts at TrendMicro one year ago, it overwrites MBR to lock users out of the infected machines. The Petya ransomware causes a blue […]
 Pierluigi Paganini
March 13, 2017
Experts from security firm Sixgill have discovered a new strain of the macOS Proton RAT that is offered for sale on Russian cybercrime underground. The Dark Web is the right place where to find any kind of illegal products and services, malware such as banking trojan and spyware are very popular in cyber criminal underground. Recently a […]
 Pierluigi Paganini
March 12, 2017
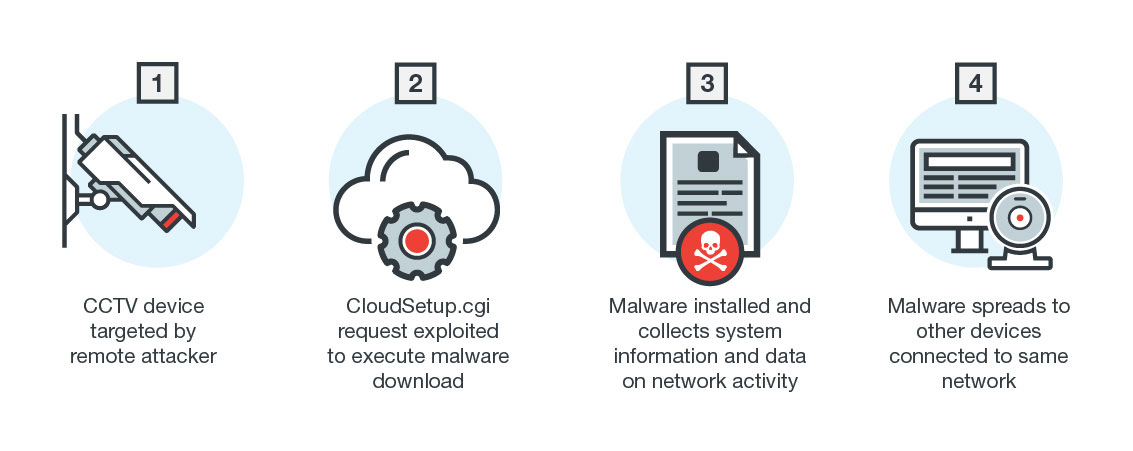
Security experts from Trend Micro discovered a new family of Linux malware, tracked as ELF_IMEIJ, targeting AVTech surveillance devices. Security experts from Trend Micro discovered a new family of Linux malware that is targeting products from surveillance technology company AVTech exploiting a CGI vulnerability that was disclosed in 2016. According to Trend Micro, the flaw was […]
 Pierluigi Paganini
March 11, 2017
Danish-speaking users were infected by malware spread through Dropbox, but the company quickly adopted the countermeasures to stop the attack. According to the experts from security firm AppRiver, Danish-speaking users were hit by an unusual malware-based attack. The attack hit Denmark, Germany, and several surrounding Scandinavian countries on Wednesday morning. Danish-speaking users were infected by malware spread through […]