 Pierluigi Paganini
 March 11, 2017
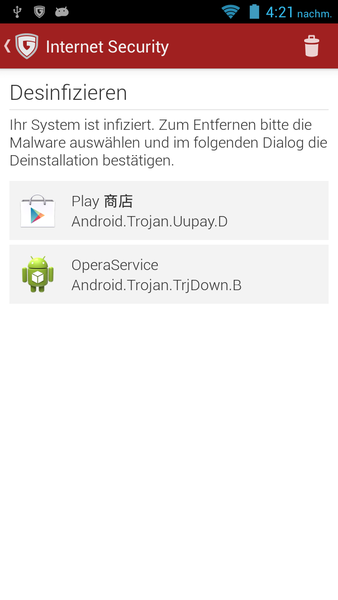
Experts discovered pre-installed malware on 38 high-end smartphone models belonging to popular manufacturing companies such as Samsung, LG, Xiaomi and Asus. In the past, security experts have already reported cases of pre-installed malware on mobile devices. In September 2015, security experts at G-Data security firm discovered new cases of Chinese Android mobile devices infected by […]
 Pierluigi Paganini
March 10, 2017
Palo Alto Networks discovered a new strain of ransomware, dubbed RanRan ransomware, that has been used in targeted attacks in Middle East. Malware researchers at Palo Alto Networks have spotted a new strain of ransomware, dubbed RanRan, that has been used in targeted attacks against government organizations in the Middle East. “Recently, Unit 42 has observed […]
 Pierluigi Paganini
March 08, 2017
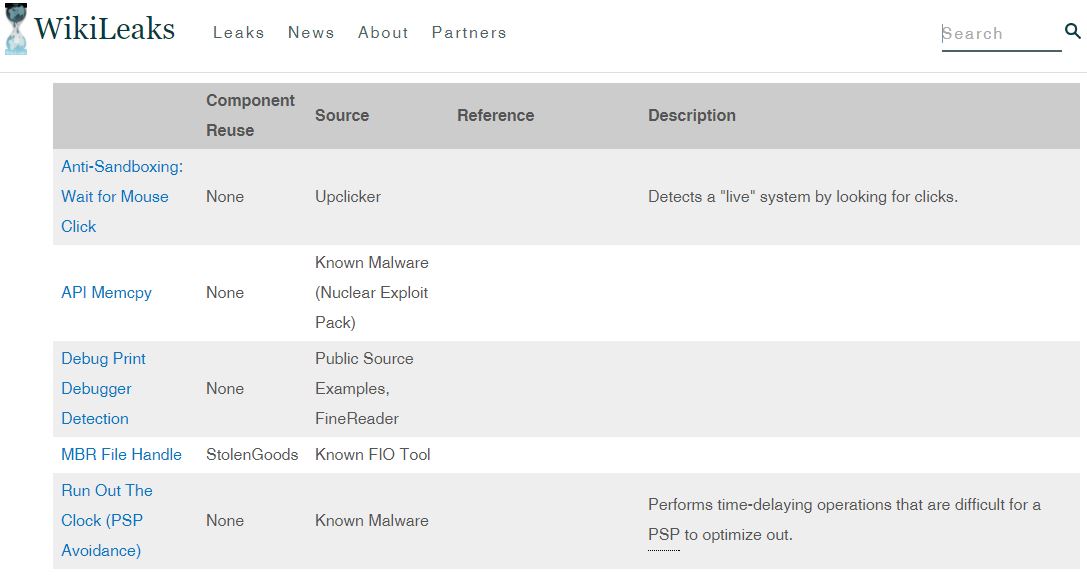
Wikileaks Vault7 data leak – the Umbrage team was tasked by the Central Intelligence Agency for false flag hacking operations. WikiLeaks has obtained thousands of files allegedly originating from a CIA high-security network that details CIA hacking tools and capabilities.Digging in the huge trove of files, it is possible to find information about the ability of the […]
 Pierluigi Paganini
March 08, 2017
The manufacture Dahua Technology has started releasing firmware updates fix a serious flaw in some models of its video recorders and IP cameras. Security experts believe the flaw is a true backdoor that could be used to remotely access the user database containing usernames and hashed passwords. The backdoor was discovered by a researcher that is known online as “bashis.” Once the attacker […]
 Pierluigi Paganini
March 07, 2017
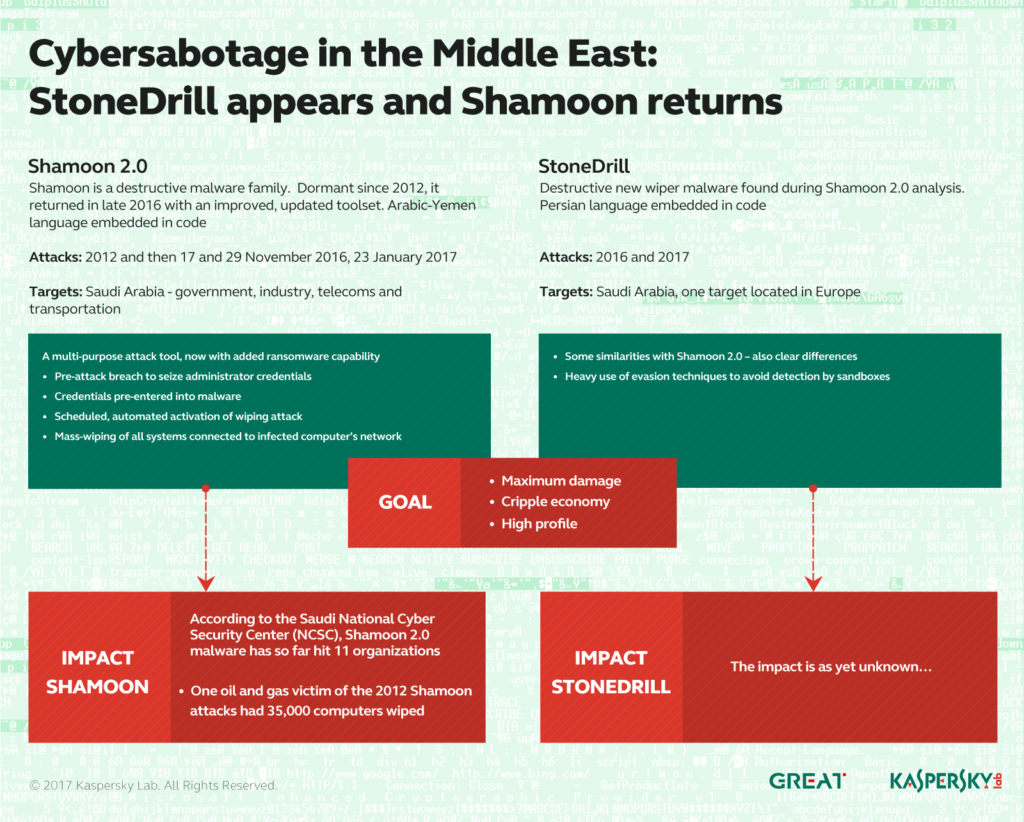
The experts spotted a new sophisticated strain of malware dubbed StoneDrill that is linked to Shamoon 2 and Charming Kitten. Researchers at Kaspersky Lab have discovered further information about the dreaded Shamoon 2 malware. The experts spotted a new sophisticated strain of malware dubbed StoneDrill that is linked to Shamoon 2 and Charming Kitten (aka Newscaster and […]
 Pierluigi Paganini
March 05, 2017
In January, a cyber attack breached some systems at Barts NHS Trust and forced them offline. Hackers exploited a zero-day vulnerability. In January, a cyber attack breached some systems at Barts NHS Trust and forced them offline. Barts Health Trust runs the Royal London, St Bartholomew’s, Whipps Cross, Mile End and Newham hospitals. The hackers used […]
 Pierluigi Paganini
March 03, 2017
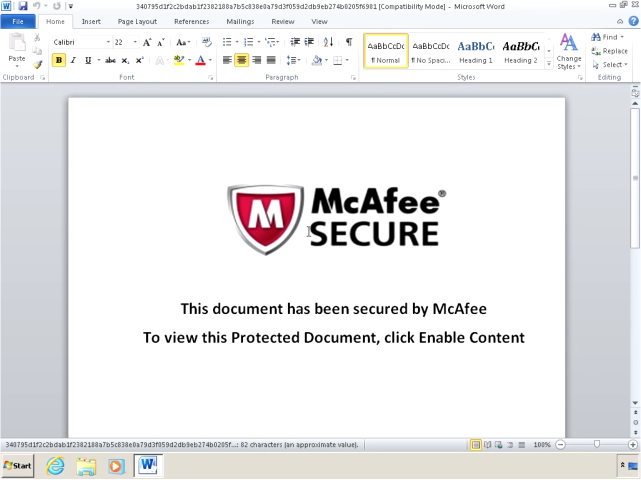
Researchers from Cisco Talos team spotted a new strain of malware that leverages PowerShell scripts to fetch commands from DNS TXT records. Malware researchers at Cisco Talos have published a detailed analysis on a targeted attack leveraging a weaponized Microsoft Word document that is spread in spam emails as an attachment. The malicious code used in the […]
 Pierluigi Paganini
March 02, 2017
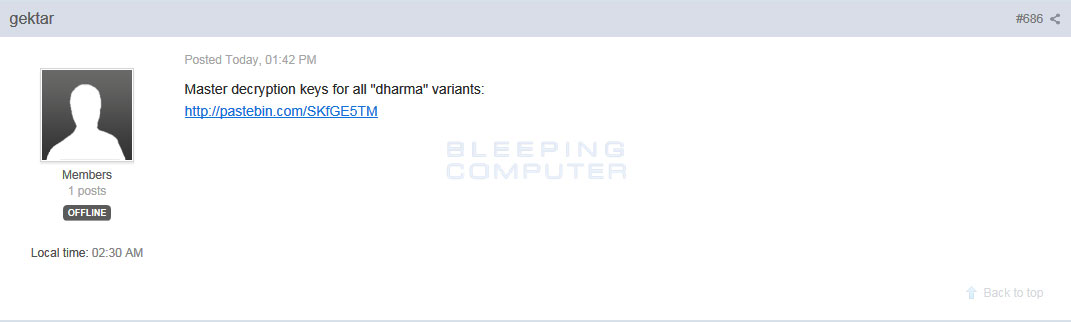
Good news for the victims of the Dharma Ransomware, someone has released the alleged Master Keys on the BleepingComputer.com forums. The alleged Master Keys for the Dharma Ransomware has been released by someone on BleepingComputer.com forums. A member using the online moniker ‘gektar‘ published a post containing a Pastebin link to a header file in C programming […]
 Pierluigi Paganini
March 01, 2017
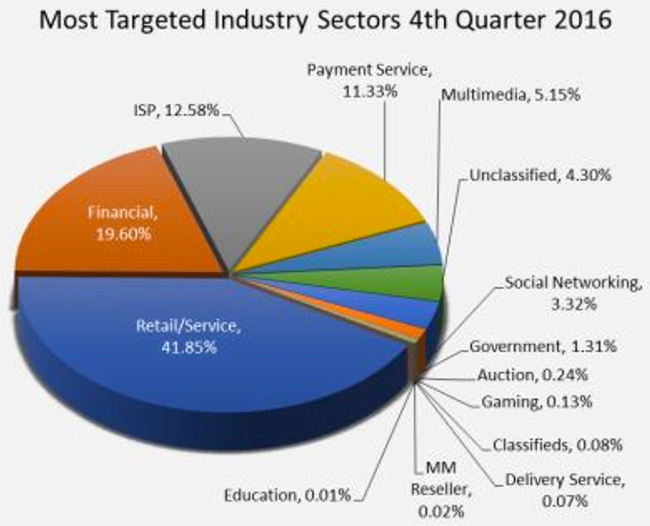
The Anti-Phishing Working Group (APWG) published the Phishing Trends Report for Q4 2016. APWG reported 1.2 million phishing attacks in 2016. The Anti-Phishing Working Group (APWG) published the Phishing Trends Report for Q4 2016. The data are worrisome, 2016 ended as the worst year for phishing in history. The experts reported the total number of phishing attacks in 2016 […]
 Pierluigi Paganini
March 01, 2017
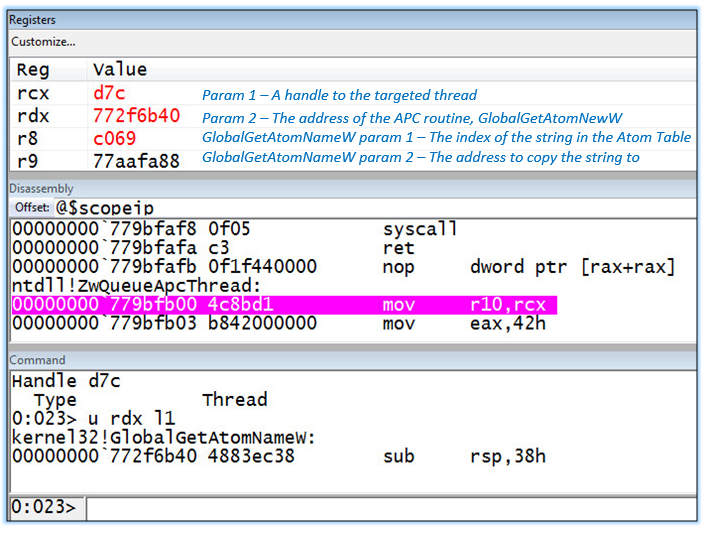
Malware author are using Dridex v4 in the wild, an improved version of the Trojan that includes a new injection method known as AtomBombing. According to researchers with IBM X-Force, vxers have improved the Dridex banking Trojan adding a new injection method for evading detection, the technique is known as AtomBombing. The researchers have spotted […]