 Pierluigi Paganini
 November 05, 2026
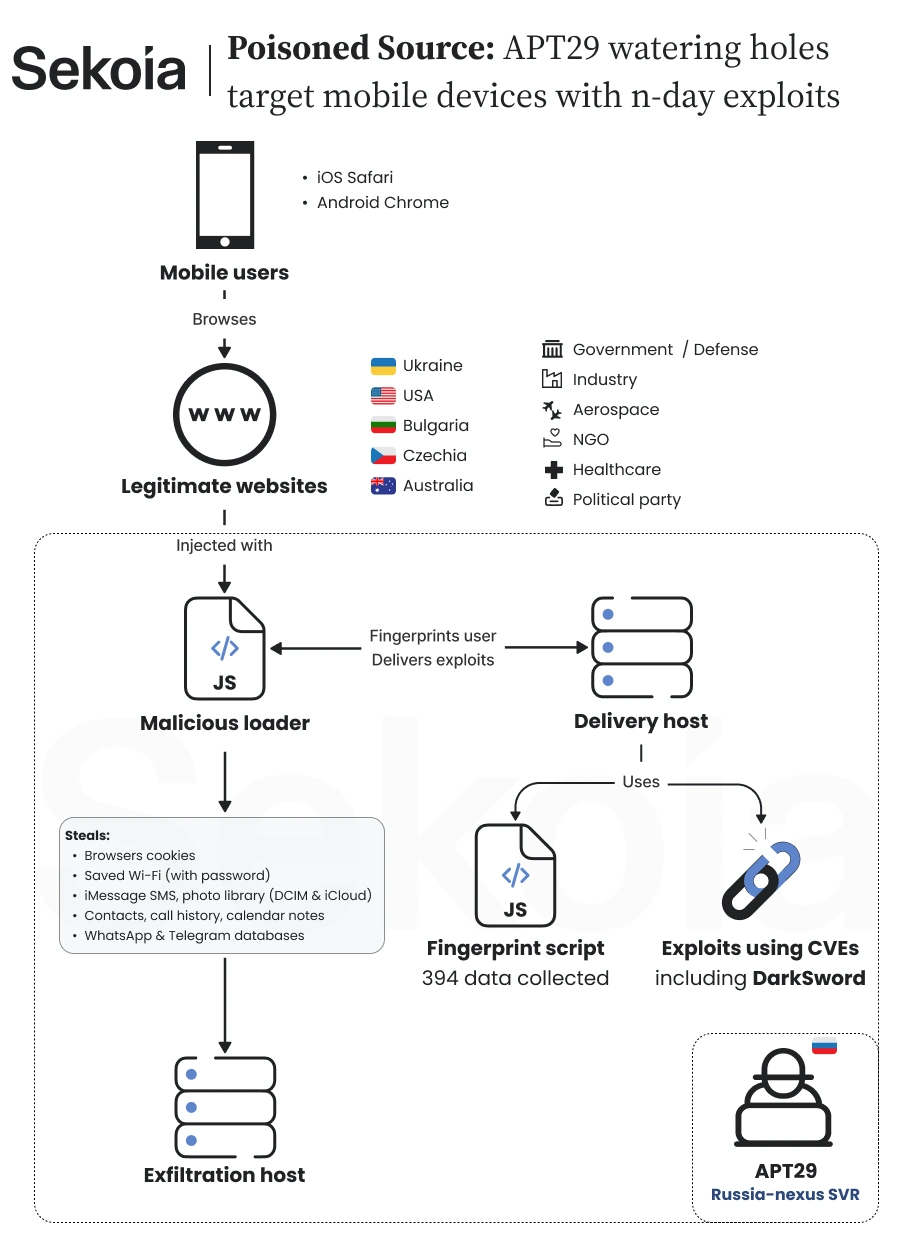
Russia-linked group APT29 targeted iOS and Android users through hijacked websites and a compromised analytics service. Sekoia says a large-scale watering hole campaign is going after iOS and Android users, and it links the campaign to APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes), the Russian group tied to the SVR foreign intelligence service. A watering hole […]
 Pierluigi Paganini
November 05, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Apple flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Apple flaw, tracked as CVE-2024-27834 (CVSS score of 5.5), to its Known Exploited Vulnerabilities (KEV) catalog. “This type of vulnerability is a frequent attack vector for malicious cyber actors and poses significant […]
 Pierluigi Paganini
August 21, 2026
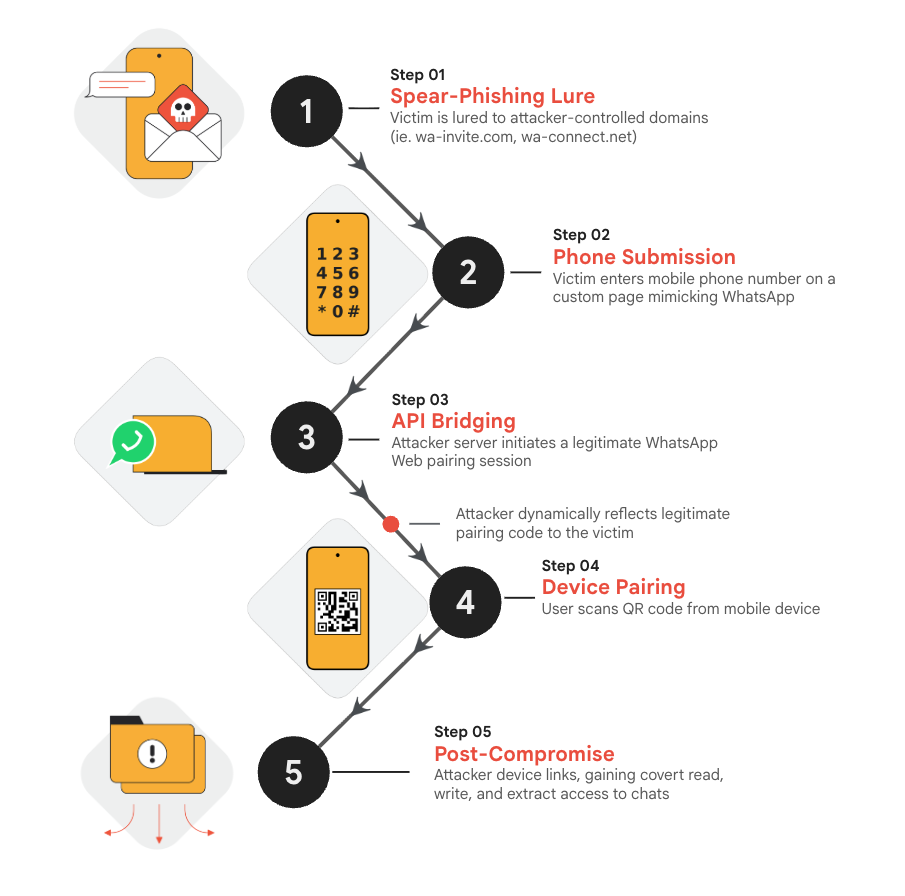
Google tracks three Russia-linked espionage clusters using phishing and legitimate authentication tools to target researchers, diplomats and defense staff. Google’s Threat Intelligence Group tracked three separate suspected Russia-linked cyber espionage clusters. All three focus on the same thing: abusing authentication features that are supposed to protect accounts to access them instead. Threat actors target researchers, […]
 Pierluigi Paganini
August 01, 2026
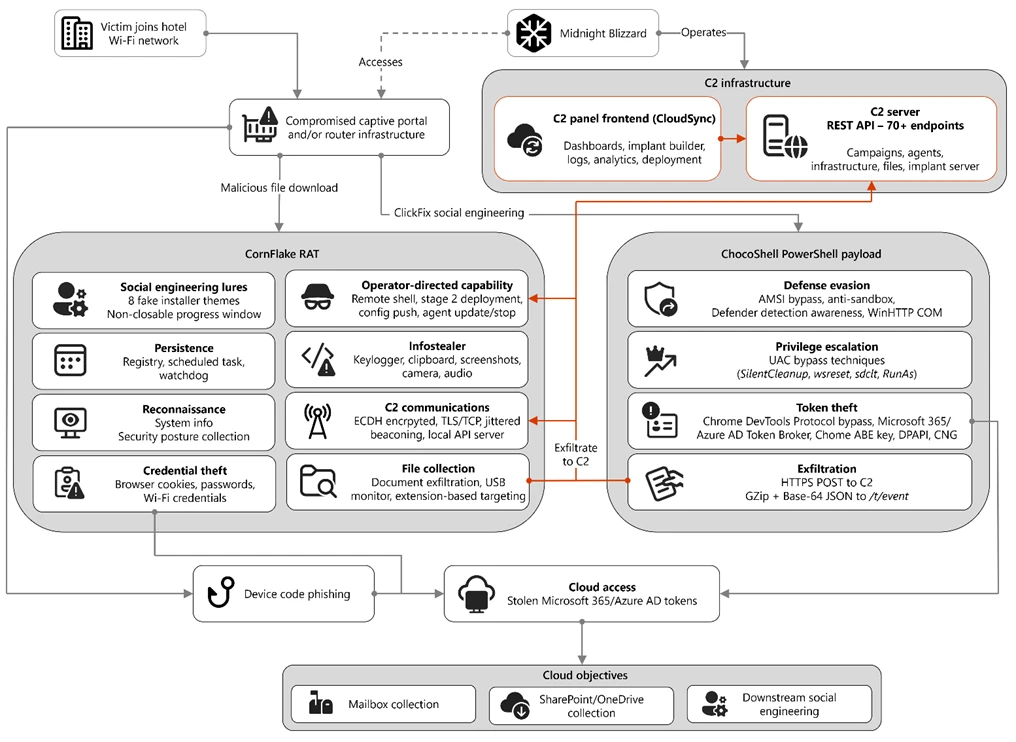
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]
 Pierluigi Paganini
August 31, 2025
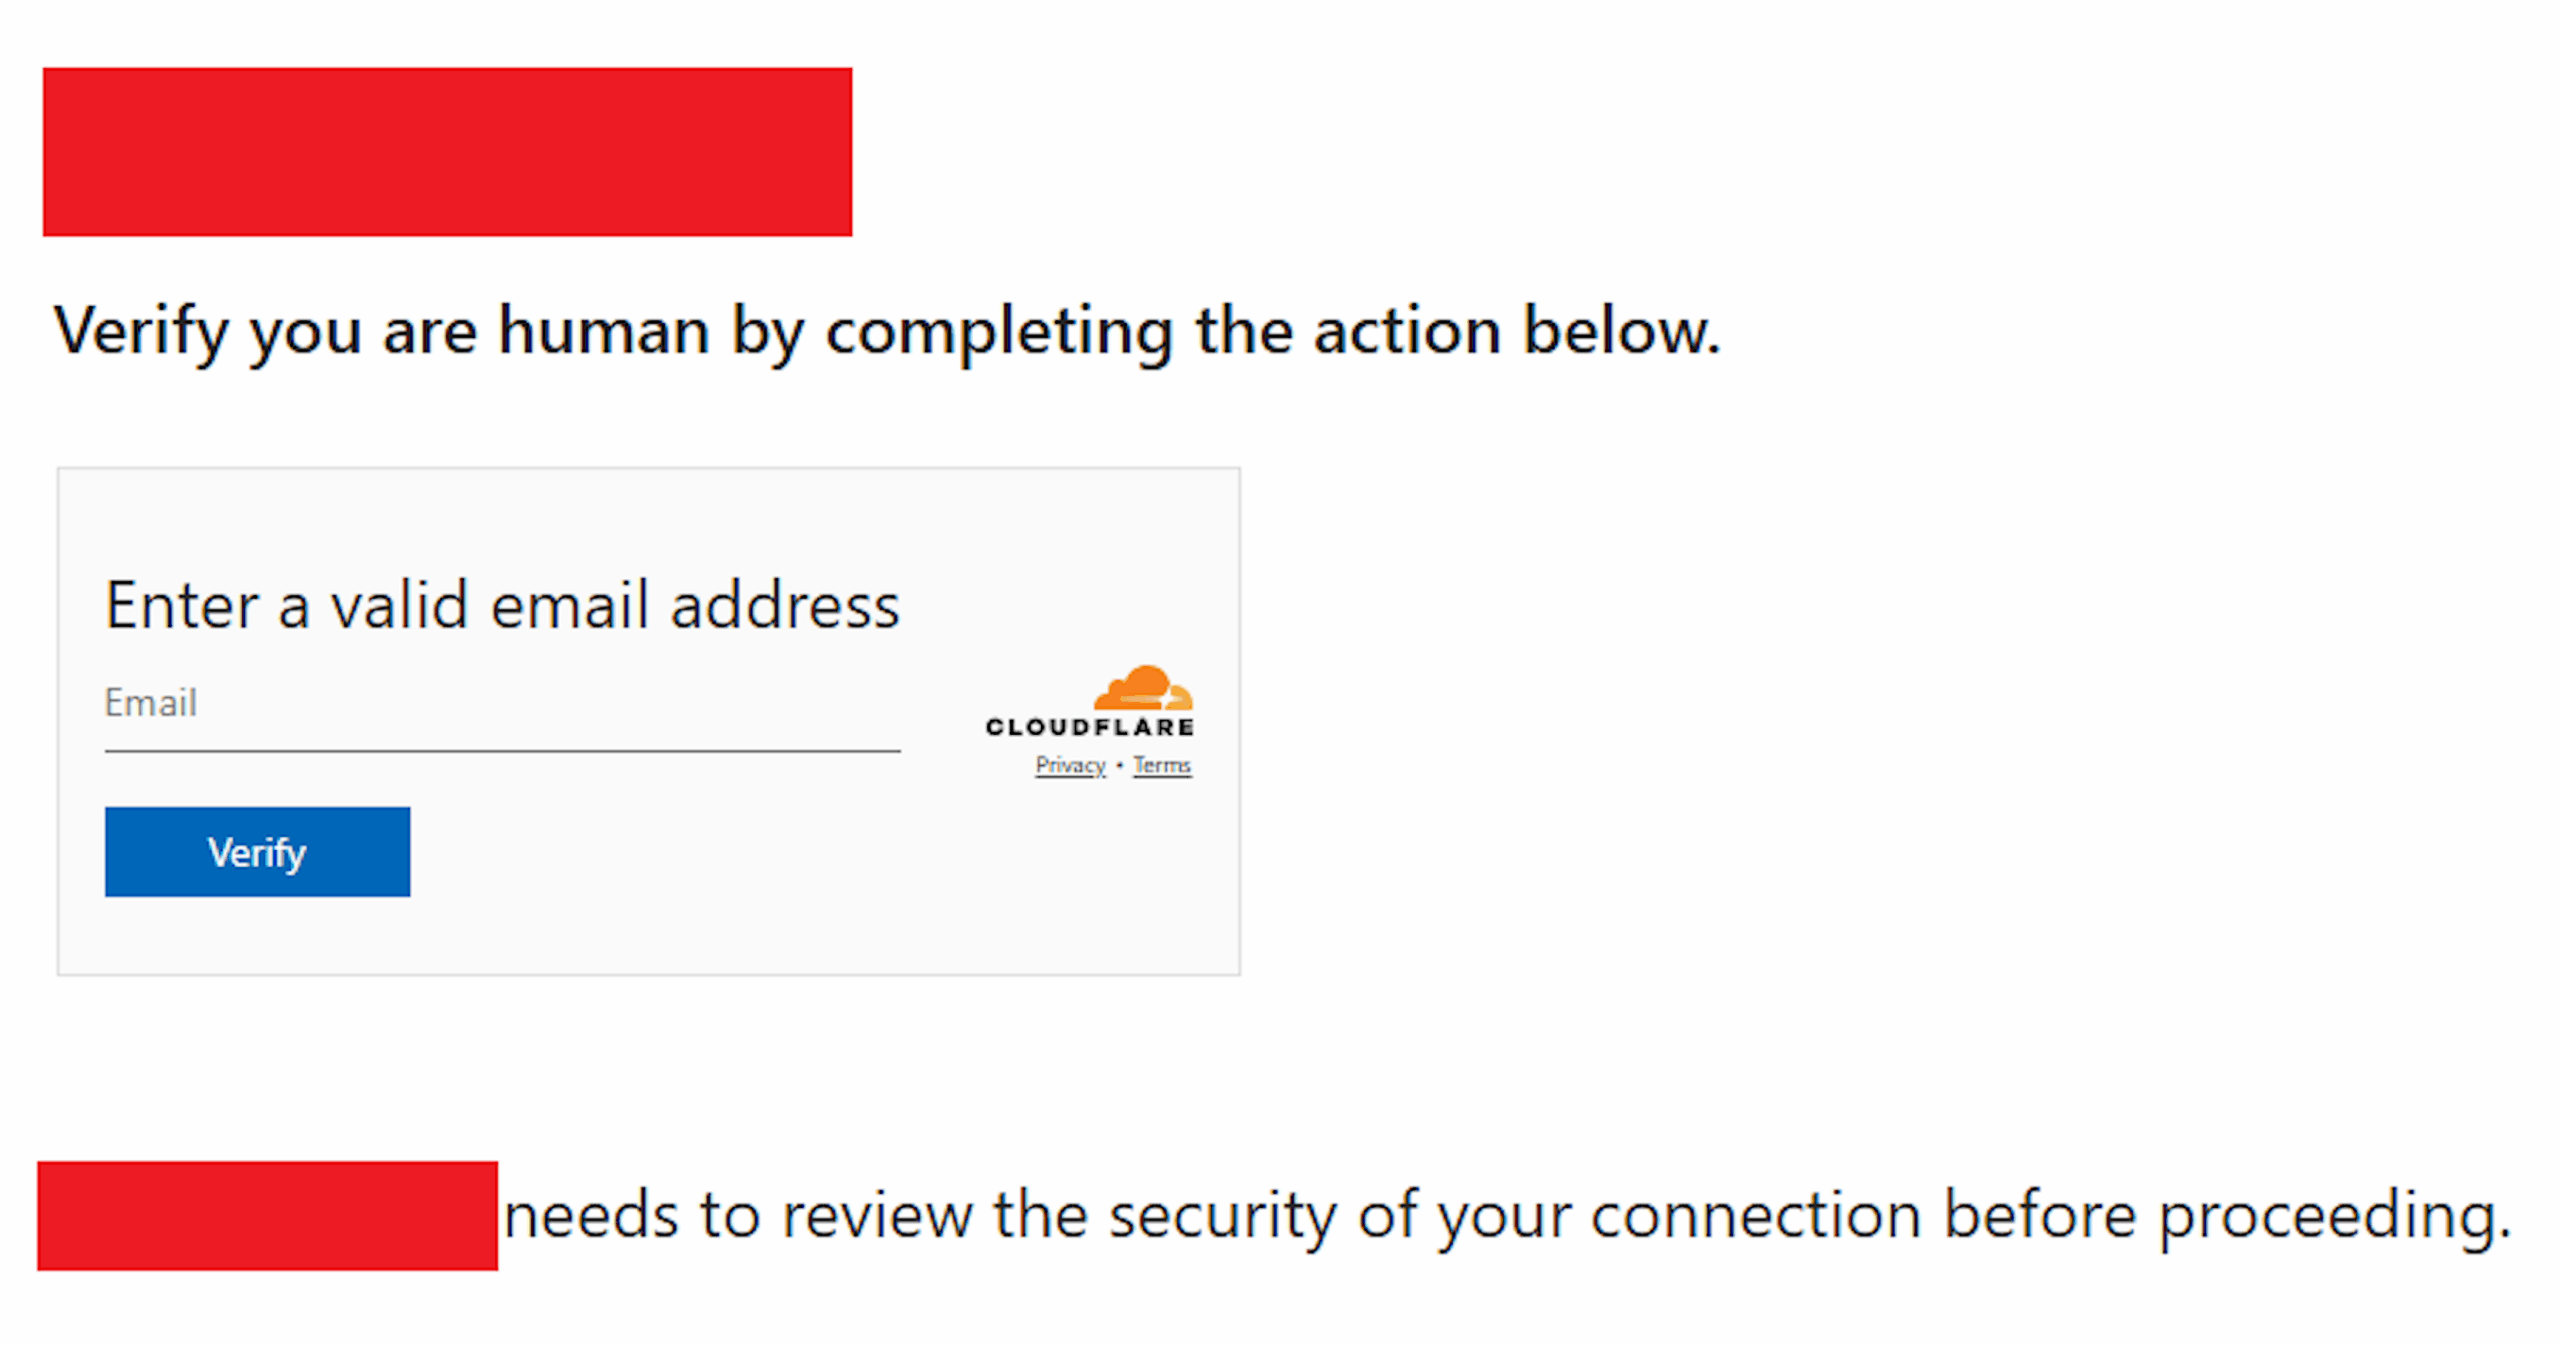
Amazon stopped a Russia-linked APT29 watering hole attack that hijacked Microsoft device code authentication via compromised sites. Amazon announced that it had disrupted an opportunistic watering hole campaign orchestrated by the Russia-linked cyber espionage group APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes). Amazon experts labeled the attacks as an opportunistic watering hole campaign using compromised […]
 Pierluigi Paganini
April 21, 2025
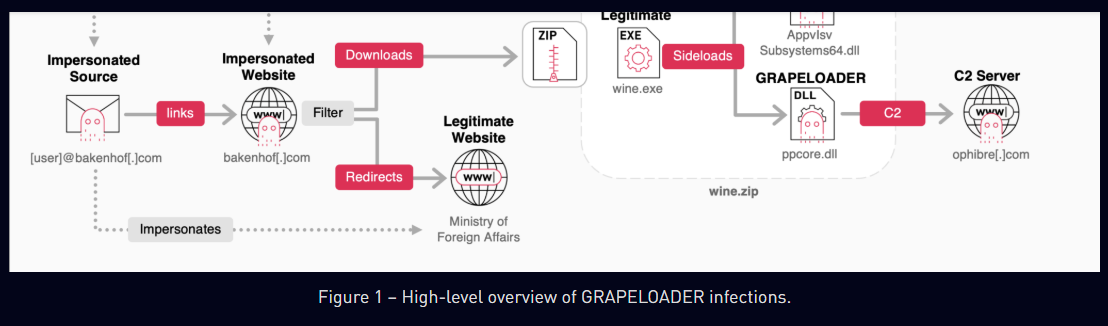
Russia-linked group APT29 targeted diplomatic entities across Europe with a new malware loader codenamed GRAPELOADER. Check Point Research team reported that Russia-linked cyberespionage group APT29 (aka SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes) is behind a sophisticated phishing campaign targeting European diplomatic entities, using a new WINELOADER variant and a previously unknown malware called GRAPELOADER. “While the […]
 Pierluigi Paganini
December 18, 2024
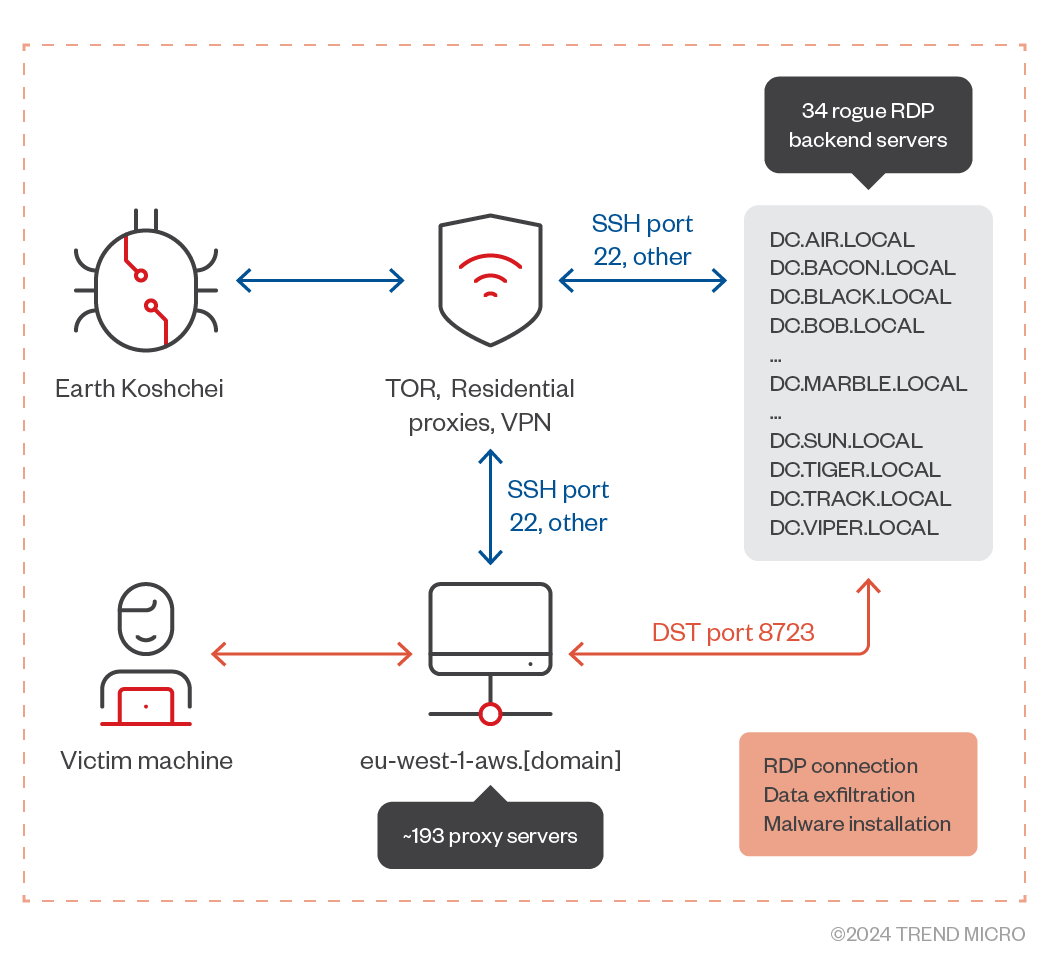
Russia-linked APT29 group uses malicious RDP configuration files, adapting red teaming methods for cyberattacks to compromise systems. In October 2024, the Russia-linked cyber espionage group APT29 (aka Earth Koshchei, SVR group, Cozy Bear, Nobelium, BlueBravo, Midnight Blizzard, and The Dukes) used rogue RDP attacks via phishing emails targeting governments, think tanks, and Ukrainian entities to steal data and install malware. The […]
 Pierluigi Paganini
October 13, 2024
U.S. and U.K. cyber agencies warn that Russia-linked group APT29 is targeting vulnerable Zimbra and JetBrains TeamCity servers on a large scale. Russia-linked cyber espionage group APT29 (aka SVR group, BlueBravo, Cozy Bear, Nobelium, Midnight Blizzard, and The Dukes) target vulnerable Zimbra and JetBrains TeamCity servers as part of a mass scale campaign, U.S. and U.K. cyber agencies warned. The Federal Bureau […]
 Pierluigi Paganini
August 30, 2024
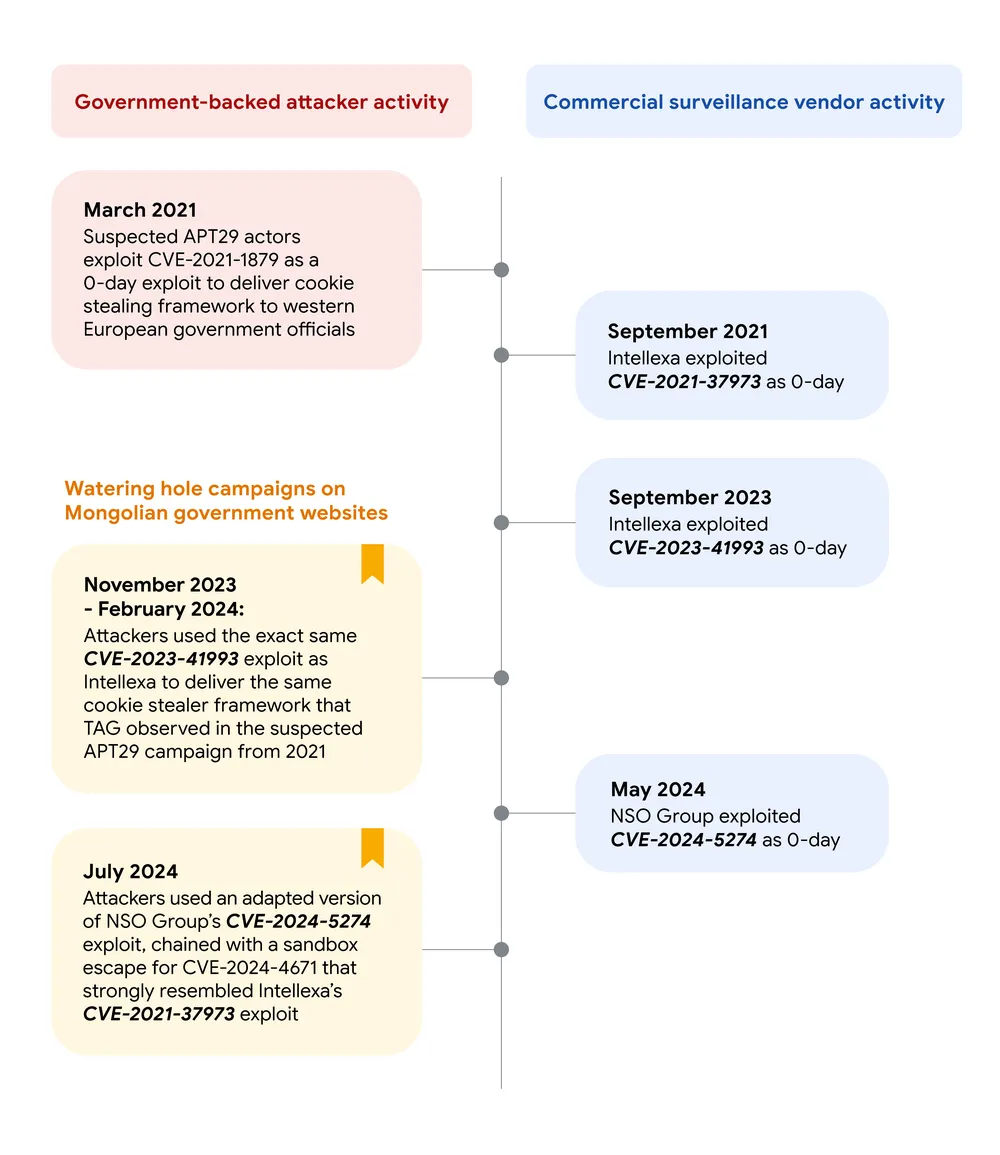
Russia-linked APT29 group was spotted reusing iOS and Chrome exploits previously developed by surveillance firms NSO Group and Intellexa. Google TAG (Threat Analysis Group) researchers observed the Russia-linked group APT29 (aka SVR group, BlueBravo, Cozy Bear, Nobelium, Midnight Blizzard, and The Dukes). using exploits previously used by surveillance software vendors NSO Group and Intellexa. The circumstance suggests that the nation-state actors […]
 Pierluigi Paganini
June 30, 2024
Russia-linked APT group, reportedly APT29, is suspected to be behind a hack of TeamViewer ‘s corporate network. TeamViewer discovered that a threat actor has breached its corporate network and some reports attribute the intrusion to the Russia-linked APT group APT29 (aka SVR group, BlueBravo, Cozy Bear, Nobelium, Midnight Blizzard, and The Dukes). The unauthorized access to the IT infrastructure of the […]