 Pierluigi Paganini
 September 05, 2026
Attackers are exploiting two new PaperCut flaws to steal credentials and gain privileged access in education-sector attacks across the U.S. and Europe. Attackers are exploiting two recelty disclosed PaperCut flaws, CVE-2026-81578 and CVE-2026-82078, in attacks targeting schools and other education organizations in the U.S. and Europe, as reported by TheHackerNews. Arctic Wolf researchers observed threat […]
 Pierluigi Paganini
September 01, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds PaperCut NG/MF flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the following vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog: PaperCut, the print management software running in schools, hospitals, and offices worldwide, recently confirmed that a pre-authentication remote code execution flaw, tracked as CVE-2026-81578, […]
Pierluigi Paganini
August 30, 2026
PaperCut servers are under active attack, while 47% of tracked installations still run unpatched versions vulnerable to remote code execution. PaperCut, the print management software running in schools, hospitals, and offices worldwide, confirmed on August 27 that a pre-authentication remote code execution flaw is being actively exploited against real customers. Researchers at Huntress found evidence […]
Pierluigi Paganini
August 05, 2023
Researchers discovered a vulnerability in PaperCut NG/MF print management software that can lead to remote code execution. Cybersecurity researchers at Horizon3 discovered a high-severity vulnerability, tracked as CVE-2023-39143 (CVSS score: 8.4), in PaperCut print management software for Windows. An attacker can exploit the vulnerability to gain remote code execution under specific conditions. The vulnerability CVE-2023-39143 is a path traversal […]
 Pierluigi Paganini
May 09, 2023
Microsoft warns of Iran-linked APT groups that are targeting vulnerable PaperCut MF/NG print management servers. Microsoft warns that Iran-linked APT groups have been observed exploiting the CVE-2023-27350 flaw in attacks against PaperCut MF/NG print management servers. The CVE-2023-27350 flaw is a PaperCut MF/NG Improper Access Control Vulnerability. PaperCut MF/NG contains an improper access control vulnerability within the […]
 Pierluigi Paganini
May 04, 2023
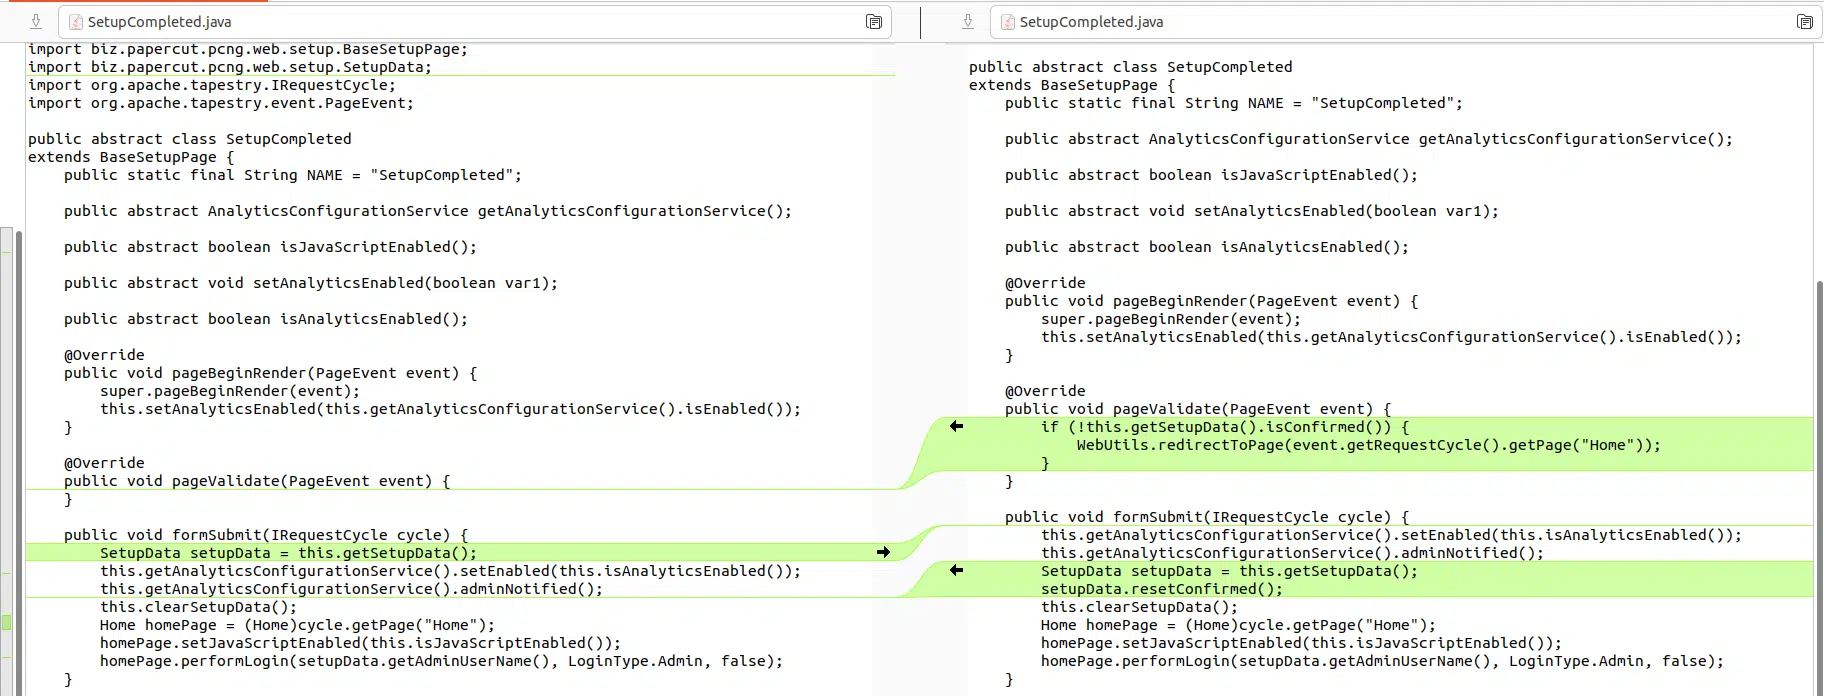
VulnCheck researchers devised a new exploit for a recently disclosed critical flaw in PaperCut servers that bypasses all current detections. Cybersecurity researchers from VulnCheck have developed a new exploit for the recently disclosed critical flaw in PaperCut servers, tracked as CVE-2023-27350 (CVSS score: 9.8), that bypasses all current detections. The CVE-2023-27350 flaw is a PaperCut MF/NG Improper Access […]
 Pierluigi Paganini
April 27, 2023
Microsoft revealed that recent attacks against PaperCut servers aimed at distributing Cl0p and LockBit ransomware. Microsoft linked the recent attacks against PaperCut servers to a financially motivated threat actor tracked as Lace Tempest (formerly DEV-0950). The group is known to be an affiliate of the Clop ransomware RaaS affiliate, it has been linked to GoAnywhere attacks and […]
Pierluigi Paganini
April 24, 2023
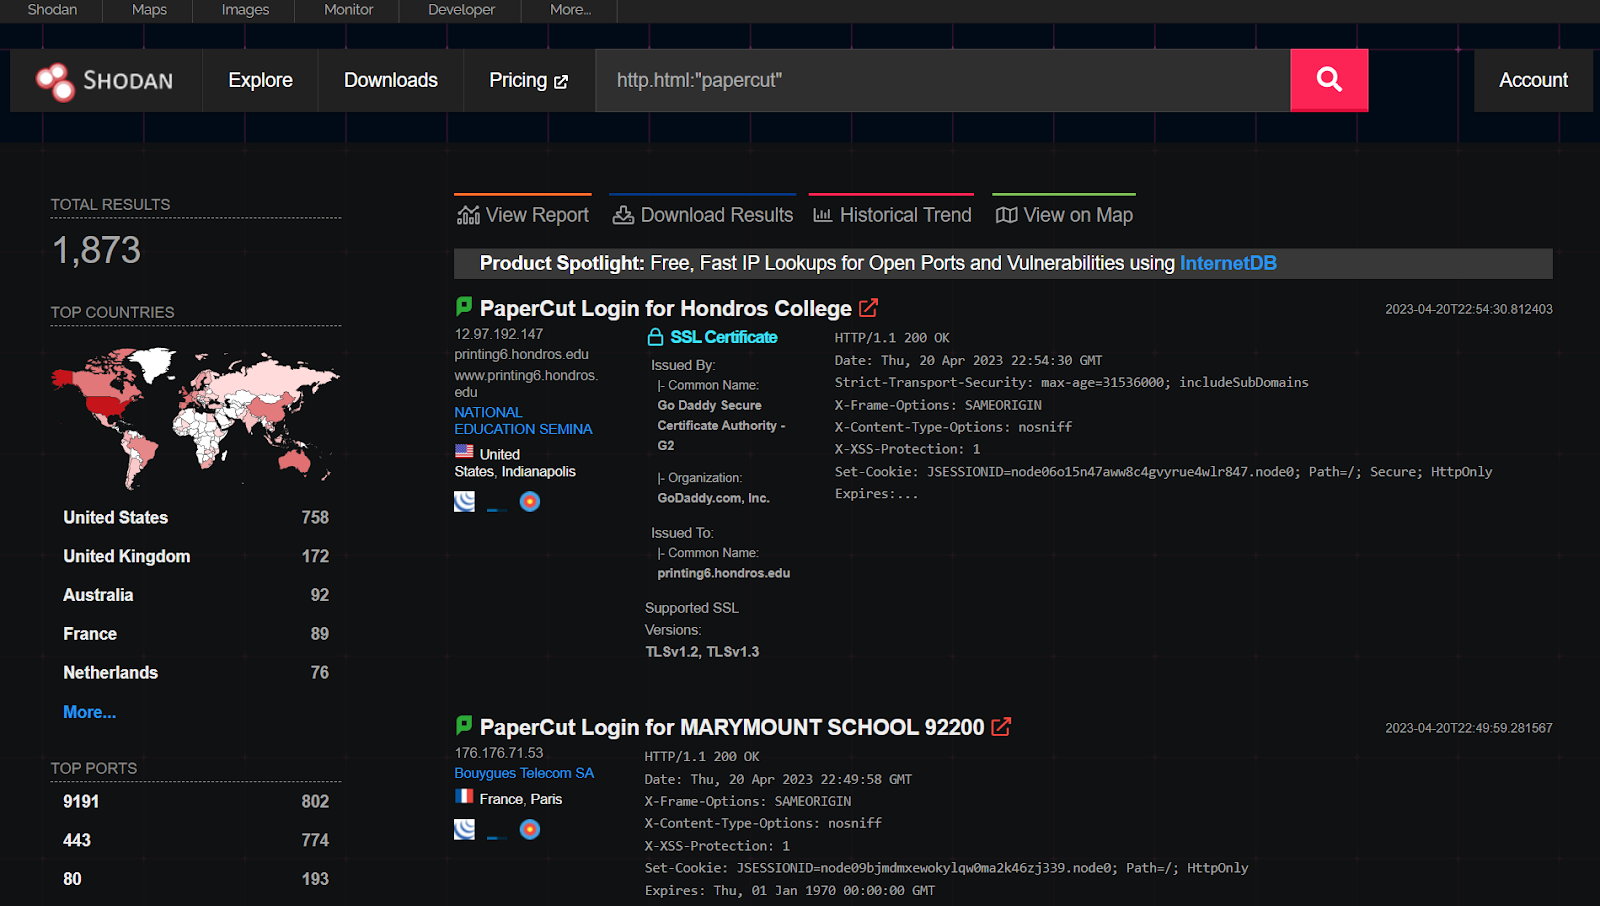
Threat actors are exploiting PaperCut MF/NG print management software flaws in attacks in the wild, while researchers released PoC exploit code. Hackers are actively exploiting PaperCut MF/NG print management software flaws (tracked as CVE-2023-27350 and CVE-2023-27351) in attacks in the wild. The threat actors were observed installing the Atera remote management software to take over vulnerable servers. On […]
Pierluigi Paganini
April 24, 2023
Print management software provider PaperCut confirmed ongoing active exploitation of CVE-2023-27350 vulnerability. On April 19th, Print management software provider PaperCut confirmed that it is aware of the active exploitation of the CVE-2023-27350 vulnerability. The company received two vulnerability reports from the cybersecurity firm Trend Micro for high/critical severity security issues in PaperCut MF/NG. Trend Micro announced they will […]
Security / September 20, 2026