



 Pierluigi Paganini
 August 26, 2026
FBI seizes QScan and QTRouter, China-linked platforms used to hide intrusions and target U.S. critical infrastructure. The U.S. Department of Justice and the FBI have seized two platforms, QScan and QTRouter, used by a China-linked group to hide cyberattacks and target critical infrastructure. The operation matters because it shows how state-backed actors no longer need […]
 Pierluigi Paganini
August 26, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Gitea flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Oracle HTTP Server and Oracle Weblogic Server Proxy Plug-in flaw, tracked as CVE-2026-60004 (CVSS score of 9,8), to its Known Exploited Vulnerabilities (KEV) catalog. Gitea is an open-source platform for […]
 Pierluigi Paganini
August 26, 2026
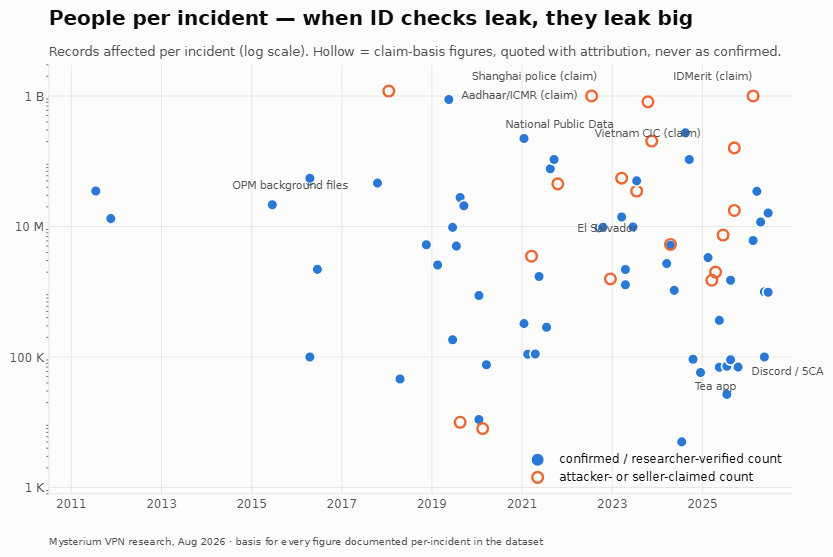
88 ID-verification breaches exposed billions of records, highlighting the growing risks of collecting sensitive identity and biometric data. A new report from Mysterium VPN compiles 88 documented incidents since 2011 where data collected specifically to verify someone’s identity or age got breached, exposed, or sold. The confirmed and researcher-verified total sits at 2.15 billion records, […]
 Pierluigi Paganini
August 26, 2026
WhatsApp says 1 billion users now use passkeys, while stronger two-step verification and caller context add new layers of account protection. WhatsApp has reached a significant security milestone: more than one billion people now use passkeys to protect access to their accounts. At the same time, Meta is adding stronger two-step verification and more information […]
 Pierluigi Paganini
August 26, 2026
INTERPOL’s Operation Jackal IV made 58 arrests and exposed global networks laundering money from scams, fraud and sextortion. INTERPOL announced that Operation Jackal IV, running from November 2025 to June 2026, led to 58 arrests and identified 263 suspects tied to West African organized crime networks, groups like Black Axe that are responsible for a […]
 Pierluigi Paganini
August 25, 2026
Norway ’s shared government infrastructure suffered a third DDoS attack, disrupting digital services but showing no signs of data compromise. Norway ‘s shared digital government infrastructure has been hit by another distributed denial-of-service (DDoS) attack that disrupted services used by citizens, businesses and public agencies. The incident began at 03:38 CEST on Monday, August 24, […]
 Pierluigi Paganini
August 25, 2026
Uber faces an €825M GDPR fine for automatically suspending drivers without human review, highlighting the risks of AI decisions affecting workers. The Dutch Data Protection Authority handed Uber its largest privacy fine yet, and this one isn’t about data transfers or cookie consent. The regulator imposed an 825 million euro penalty, roughly $964 million, over […]
 Pierluigi Paganini
August 25, 2026
Two CVSS 9.8 miniOrange SAML WordPress plugin auth bypasses were exploited while paid editions never appeared in any vulnerability database. Manual patch required. Two critical authentication bypass vulnerabilities in the miniOrange SAML 2.0 Single Sign On WordPress plugin, both rated CVSS 9.8, are under active exploitation. Both CVE-2026-61979 and CVE-2026-15981 allow an unauthenticated attacker to […]
Pierluigi Paganini
August 25, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Oracle flaw to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added an Oracle HTTP Server and Oracle Weblogic Server Proxy Plug-in flaw, tracked as CVE-2026-21962 (CVSS score of 10,0), to its Known Exploited Vulnerabilities (KEV) catalog. CVE-2026-21962 is a critical, unauthenticated vulnerability […]
 Pierluigi Paganini
August 25, 2026
WeedHack Minecraft Malware Survives C2 Takedown: Fake Client Sites Still Active, SEO Poisoning Puts Malicious Downloads at the Top of Google McAfee Labs published a follow-up report on the WeedHack Malware-as-a-Service campaign this week, documenting ten active malicious sites and multiple file-hosting accounts that are still spreading the infostealer despite a disruption to its command-and-control […]

Security / September 15, 2026

