 Pierluigi Paganini
 September 18, 2026
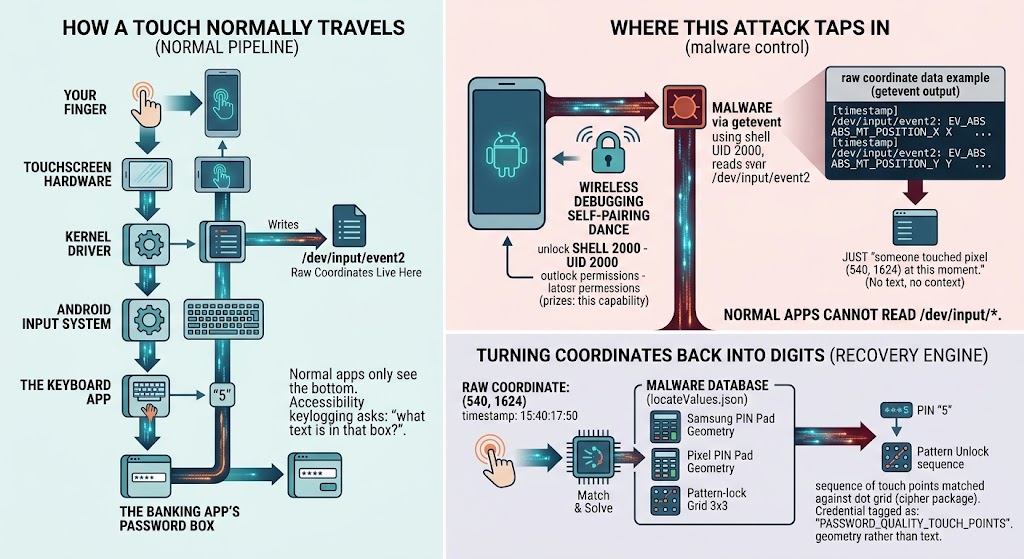
RatHat combines AI-driven screen control, Android debugging abuse and advanced credential theft to give attackers deep control of infected phones. RatHat is the new Android trojan you should know about. Zimperium researchers just published a breakdown of a strain they’ve traced to China-based operators, and what makes it different isn’t the credential theft, which is […]
 Pierluigi Paganini
September 16, 2026
Google has patched a high-severity zero-day in the Pixel cellular modem after finding evidence that the vulnerability was exploited in limited, targeted attacks. Google has released its September 2026 Pixel security update, addressing a large set of vulnerabilities, including a high-severity flaw, tracked as CVE-2026-58704 (CVSS score of 8.0), in the cellular modem that has […]
 Pierluigi Paganini
September 08, 2026
Researchers built a WeChat worm that spreads through incoming calls without user action. Tencent has blocked the exploit. Researchers at Calif created a WeChat worm that can take over an account through an incoming call, even if the victim never answers or touches the phone. The attack works only when the caller already appears in […]
 Pierluigi Paganini
August 20, 2026
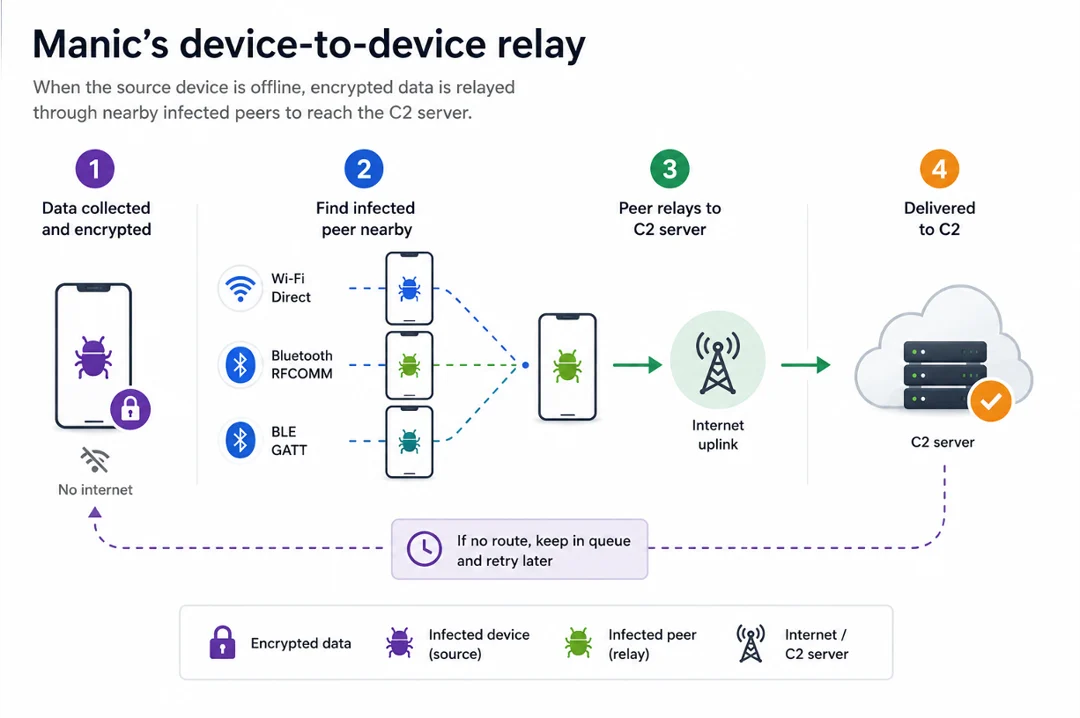
Manic Android malware combines banking fraud and spyware, using a Bluetooth relay to steal data even when devices are offline. ThreatFabric’s Mobile Threat Intelligence team has identified a new Android malware, dubbed Manic, which has been active in the wild since at least February 2026. The researchers state that the malware is still under development […]
 Pierluigi Paganini
July 08, 2026
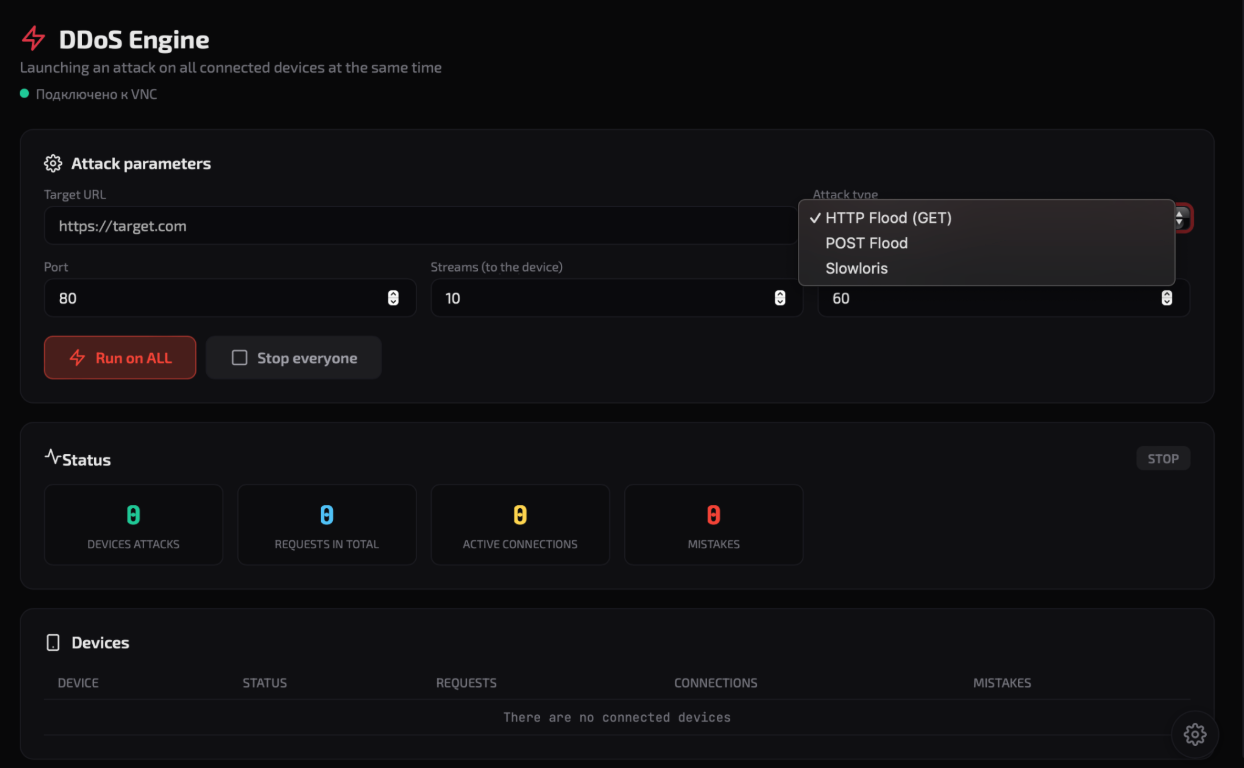
RedWing: The Android Banking Trojan You Can Rent on Telegram for Less Than a Coffee Subscription Zimperium’s zLabs team has uncovered RedWing, an Android spyware operation sold as a subscription service through Telegram, with links to Russian threat actors and apparent roots in the Oblivion malware family. It comes with documentation, tutorial videos, a referral […]
 Pierluigi Paganini
July 06, 2026
Bad Epoll (CVE-2026-46242) lets local attackers gain root on Linux and Android. The flaw was missed by AI but found by a security researcher. A newly disclosed Linux kernel vulnerability, named Bad Epoll (CVE-2026-46242), allows a local attacker with no special privileges to gain full root access on affected Linux systems and Android devices. Security updates are […]
 Pierluigi Paganini
July 02, 2026
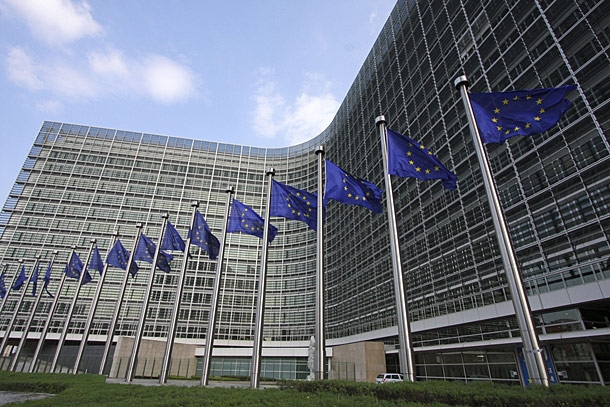
EU’s top court upheld a €4.1B fine against Google, ruling it abused Android’s market dominance through restrictive licensing practices. The Court of Justice of the European Union issued its ruling on July 2, 2026, and Google lost. The court dismissed the appeal brought by Google and its parent company Alphabet against an earlier judgment from […]
 Pierluigi Paganini
June 17, 2026
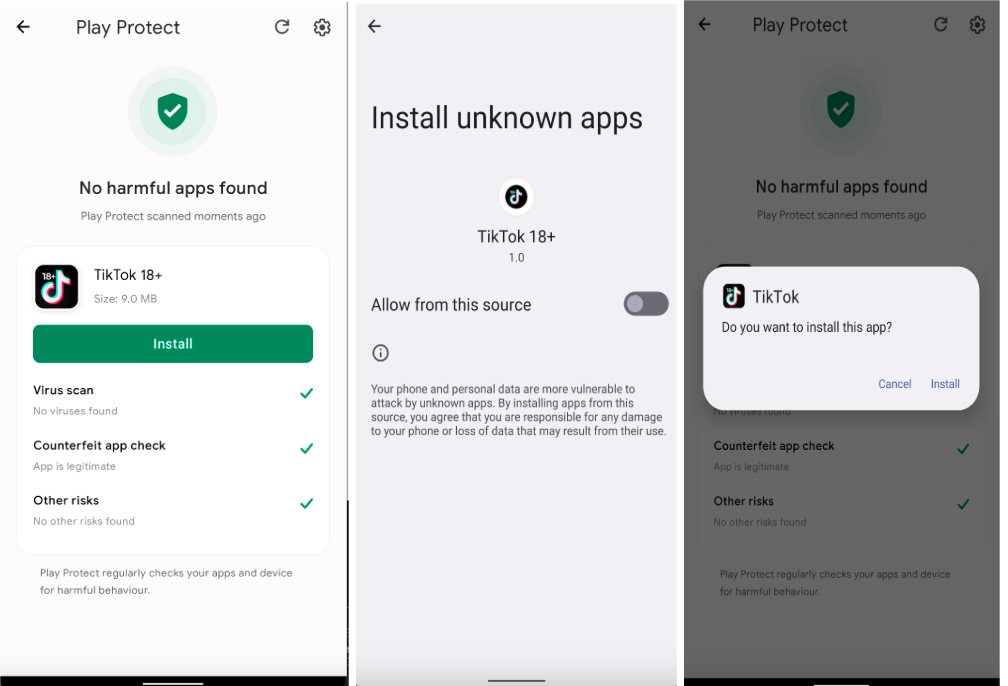
Rokarolla Android malware targets 217 banking and crypto apps, steals credentials, blocks bank calls, intercepts SMS, and disables Play Protect. Zimperium’s zLabs researchers have published a detailed analysis of Rokarolla, a new Android banking trojan named after its command-and-control infrastructure. It spreads through malicious websites masquerading as TikTok and Chrome, one confirmed distribution point being […]
 Pierluigi Paganini
June 03, 2026
U.S. Cybersecurity and Infrastructure Security Agency (CISA) adds Android and Linux Kernel flaws to its Known Exploited Vulnerabilities catalog. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added Windows Shell and ConnectWise ScreenConnect flaws to its Known Exploited Vulnerabilities (KEV) catalog. Below are the flaws added to the catalog: The first flaw added to the catalog, tracked […]
 Pierluigi Paganini
June 03, 2026
Google fixed 124 Android flaws, including CVE-2025-48595, an actively exploited privilege escalation bug linked to targeted attacks. Google has released its June 2026 Android security updates, fixing 124 vulnerabilities across the mobile operating system. One flaw, tracked as CVE-2025-48595 (CVSS score of 8.4) stands out from the rest because it is already being exploited in […]
Uncategorized / September 21, 2026
Security / September 20, 2026