 Pierluigi Paganini
 November 09, 2026
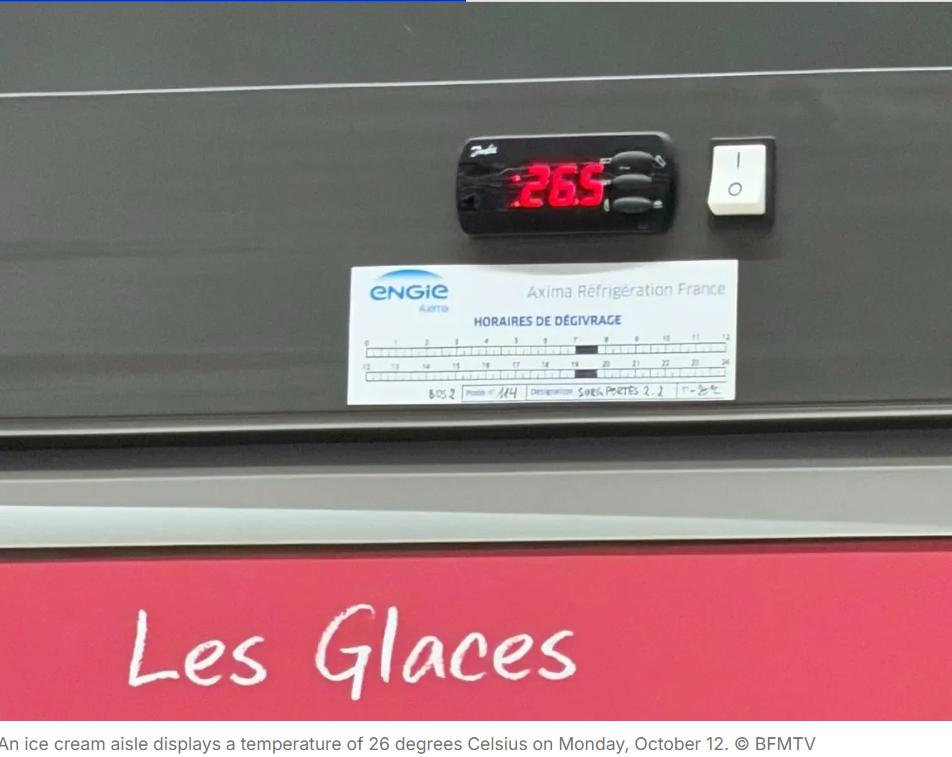
France blames Iran for supermarket fridge attacks. What’s known, what remains unclear, and how to secure exposed controllers. French Foreign Minister Jean-Noël Barrot said Iran’s Revolutionary Guard Corps was behind the attacks on supermarket fridges in France on 11 and 12 October. He said they hit 700 sites and raised refrigerator temperatures. Some stores threw […]
 Pierluigi Paganini
November 09, 2026
Taiwanese vendor QNAP urges users to update Plex Media Server after reports of NAS compromises through the Plex2Shell vulnerability chain. QNAP urges users to update Plex Media Server through the QNAP App Center after reports that threat actors exploited the Plex2Shell vulnerability chain to compromise NAS devices. “QNAP has received reports from some users that […]
 Pierluigi Paganini
November 09, 2026
US agencies warn attackers are going after industrial refrigeration controllers. The fixes are basic, and most start with getting them off the internet. CISA, the FBI, HHS, USDA and the Department of Transportation published a joint advisory on attacks against industrial refrigeration controllers and cold chain monitoring systems. The activity is global. Healthcare, chemical, food […]
 Pierluigi Paganini
November 02, 2026
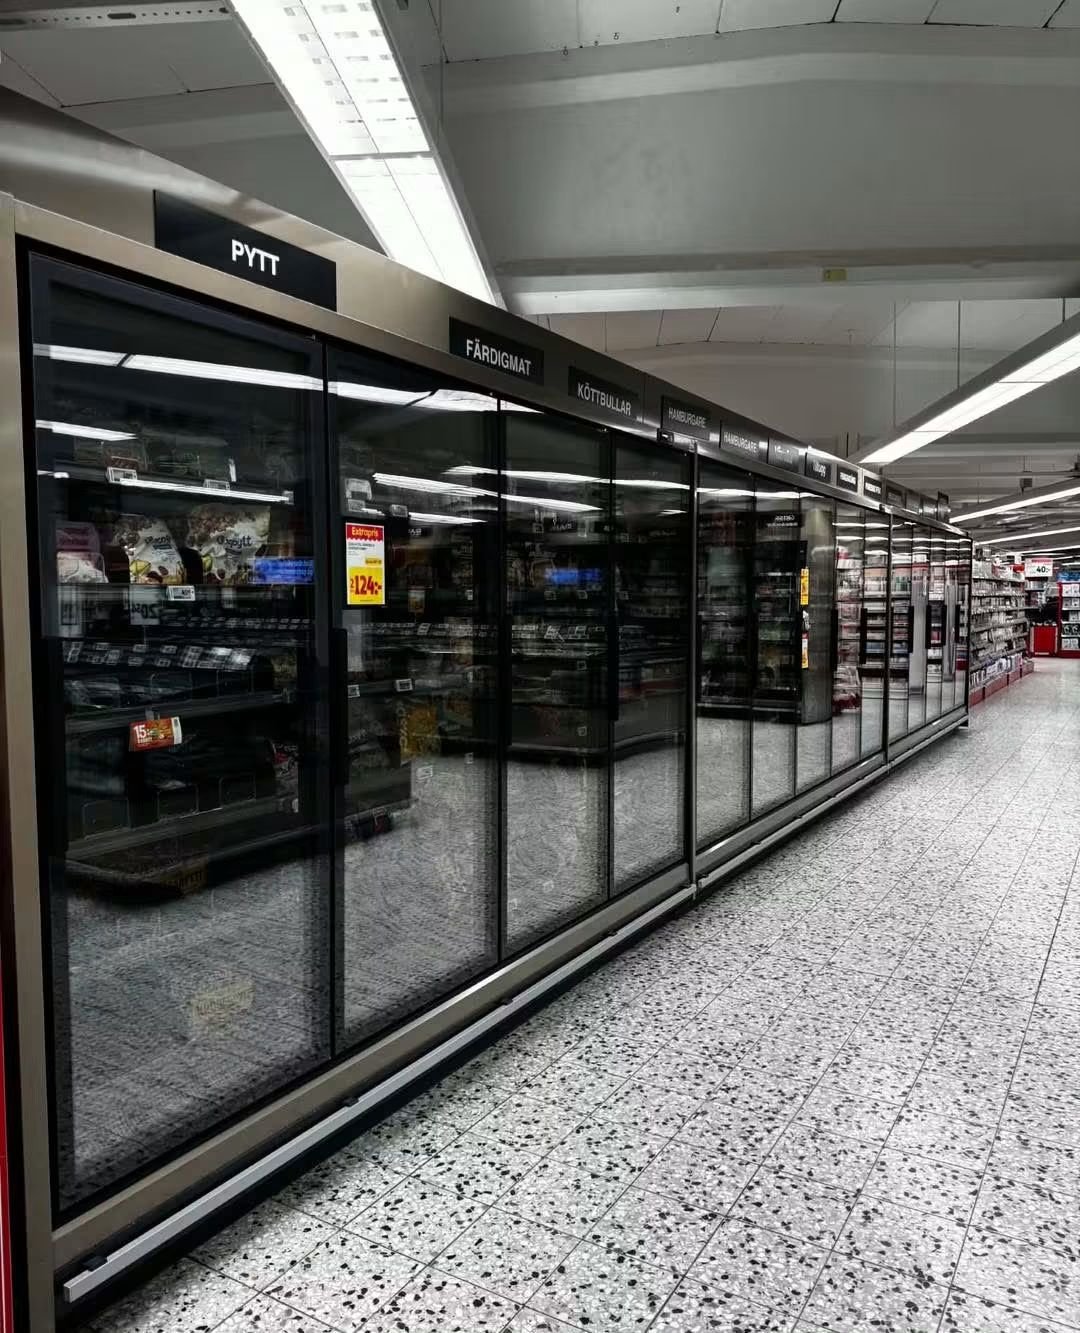
A new wave of fridge cyberattacks hit supermarket refrigeration systems across five European countries, raising temperatures and causing food losses. A new wave of fridge cyberattacks has affected supermarket refrigeration systems in several European countries. Fridges and freezers suddenly rose in temperature overnight, with some incidents suspected to be caused by hackers. On Monday, November […]
 Pierluigi Paganini
October 27, 2026
Ukraine warns that attackers can remotely access Dahua cameras and recorders via Easy4IP, viewing video and changing settings. Ukraine’s cyber incident response team CERT-UA has warned about attackers taking over video surveillance systems made by Dahua. In its alert dated October 23, 2026, it reports unauthorized remote access to IP cameras and video recorders. The […]
 Pierluigi Paganini
October 06, 2026
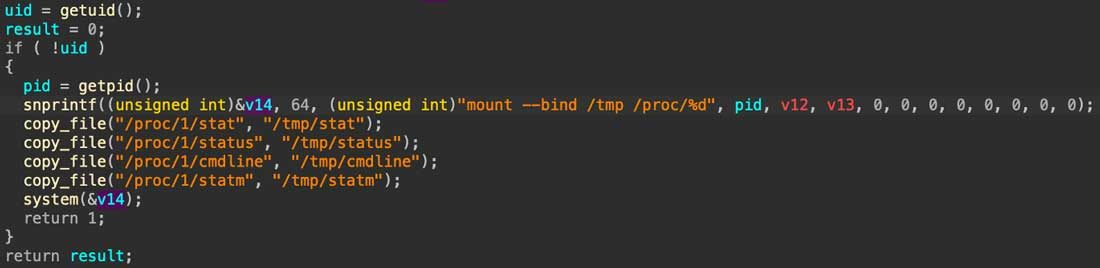
Fortinet details ClingSTUN, a Linux backdoor exploiting unpatched IoT devices and abusing public STUN servers to route traffic past NAT. FortiGuard Labs researchers spotted a Linux malware family they call ClingSTUN, and the name gives away its trick immediately. Instead of relying on a dedicated command server, the malicious code leans on STUN, the protocol […]
 Pierluigi Paganini
July 16, 2026
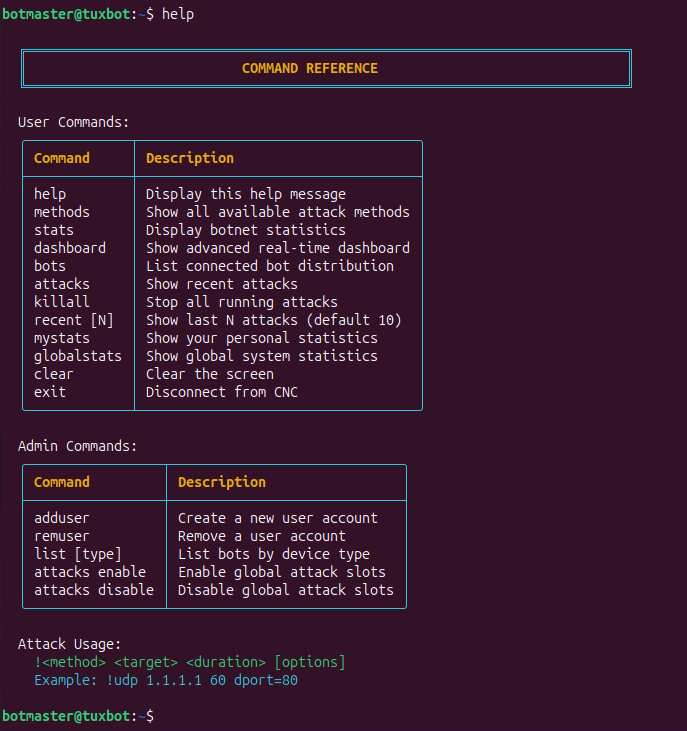
TuxBot v3, an AI-built IoT botnet for 17 architectures, shipped with LLM bugs and safety disclaimers the developer never removed. Palo Alto Networks’ Unit 42 identified a previously undocumented modular IoT botnet framework called TuxBot v3 Evolution, and it comes with an unusual detail: the developer used a large language model to write significant portions […]
 Pierluigi Paganini
July 06, 2026
runZero found 7 flaws in FatFs, a filesystem used in IoT and embedded devices. Bugs can cause memory corruption, crashes, or data leaks via crafted storage. Cybersecurity firm runZero has disclosed seven vulnerabilities in FatFs, a compact open-source library that lets embedded devices read and write FAT and exFAT formatted storage, the same formats used […]
 Pierluigi Paganini
June 11, 2026
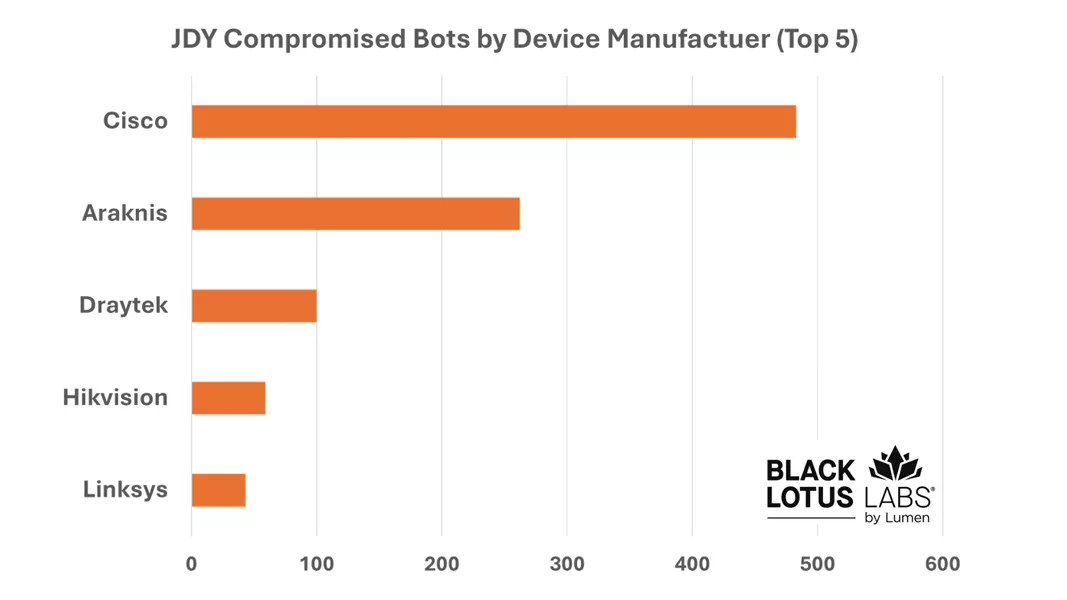
JDY botnet scans SOHO/IoT devices globally to map services and targets, especially US military networks. Lumen’s Black Lotus Labs reported the resurgence of the JDY botnet, a covert reconnaissance network tied to Chinese state-sponsored hacking groups including Volt Typhoon. The network was first spotted in late 2023 as a cluster inside KV-botnet. The U.S. government […]
 Pierluigi Paganini
February 19, 2026
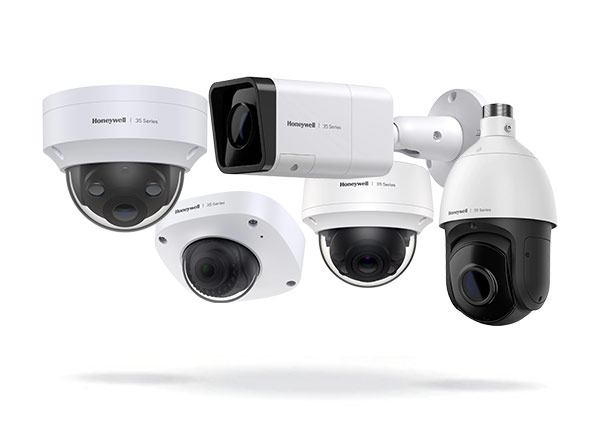
CISA warns Honeywell CCTVs are affected by a critical auth bypass flaw (CVE-2026-1670) allowing unauthorized access or account hijacking. The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warns that Honeywell CCTVs are affected by a critical authentication bypass flaw, tracked as CVE-2026-1670 (CVSS score of 9.8), that lets attackers change the recovery email without logging […]