


 Pierluigi Paganini
 August 02, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including international press. Russian Hackers Hijack Hotel Wi-Fi to Steal Microsoft 365 Tokens Adobe fixed a maximum-severity vulnerability flaw in […]
 Pierluigi Paganini
July 31, 2026
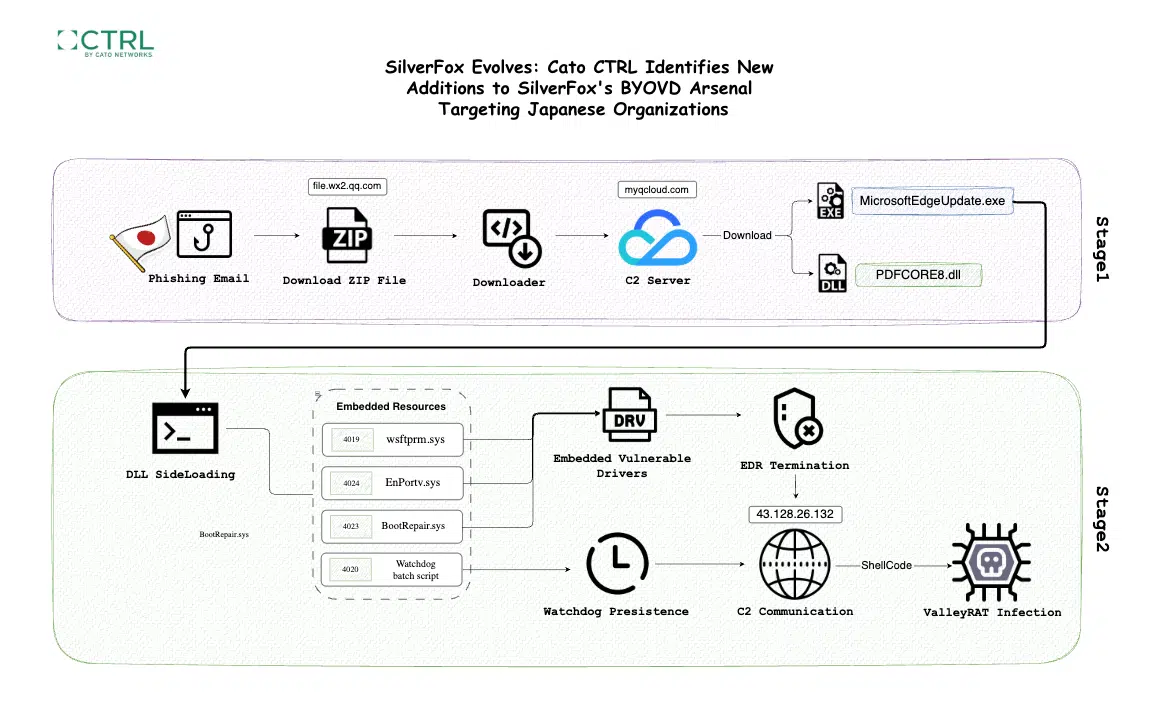
SilverFox targeted a Japanese manufacturer with new DLL sideloading techniques, kernel drivers, and resilient ValleyRAT persistence mechanisms. Cato CTRL documented a new SilverFox campaign targeting a Japanese industrial manufacturer. The attack chain adds two previously undocumented DLL-sideloading hosts, two kernel drivers not previously associated with SilverFox, and a dual-layer recovery architecture that keeps ValleyRAT running […]
 Pierluigi Paganini
July 30, 2026
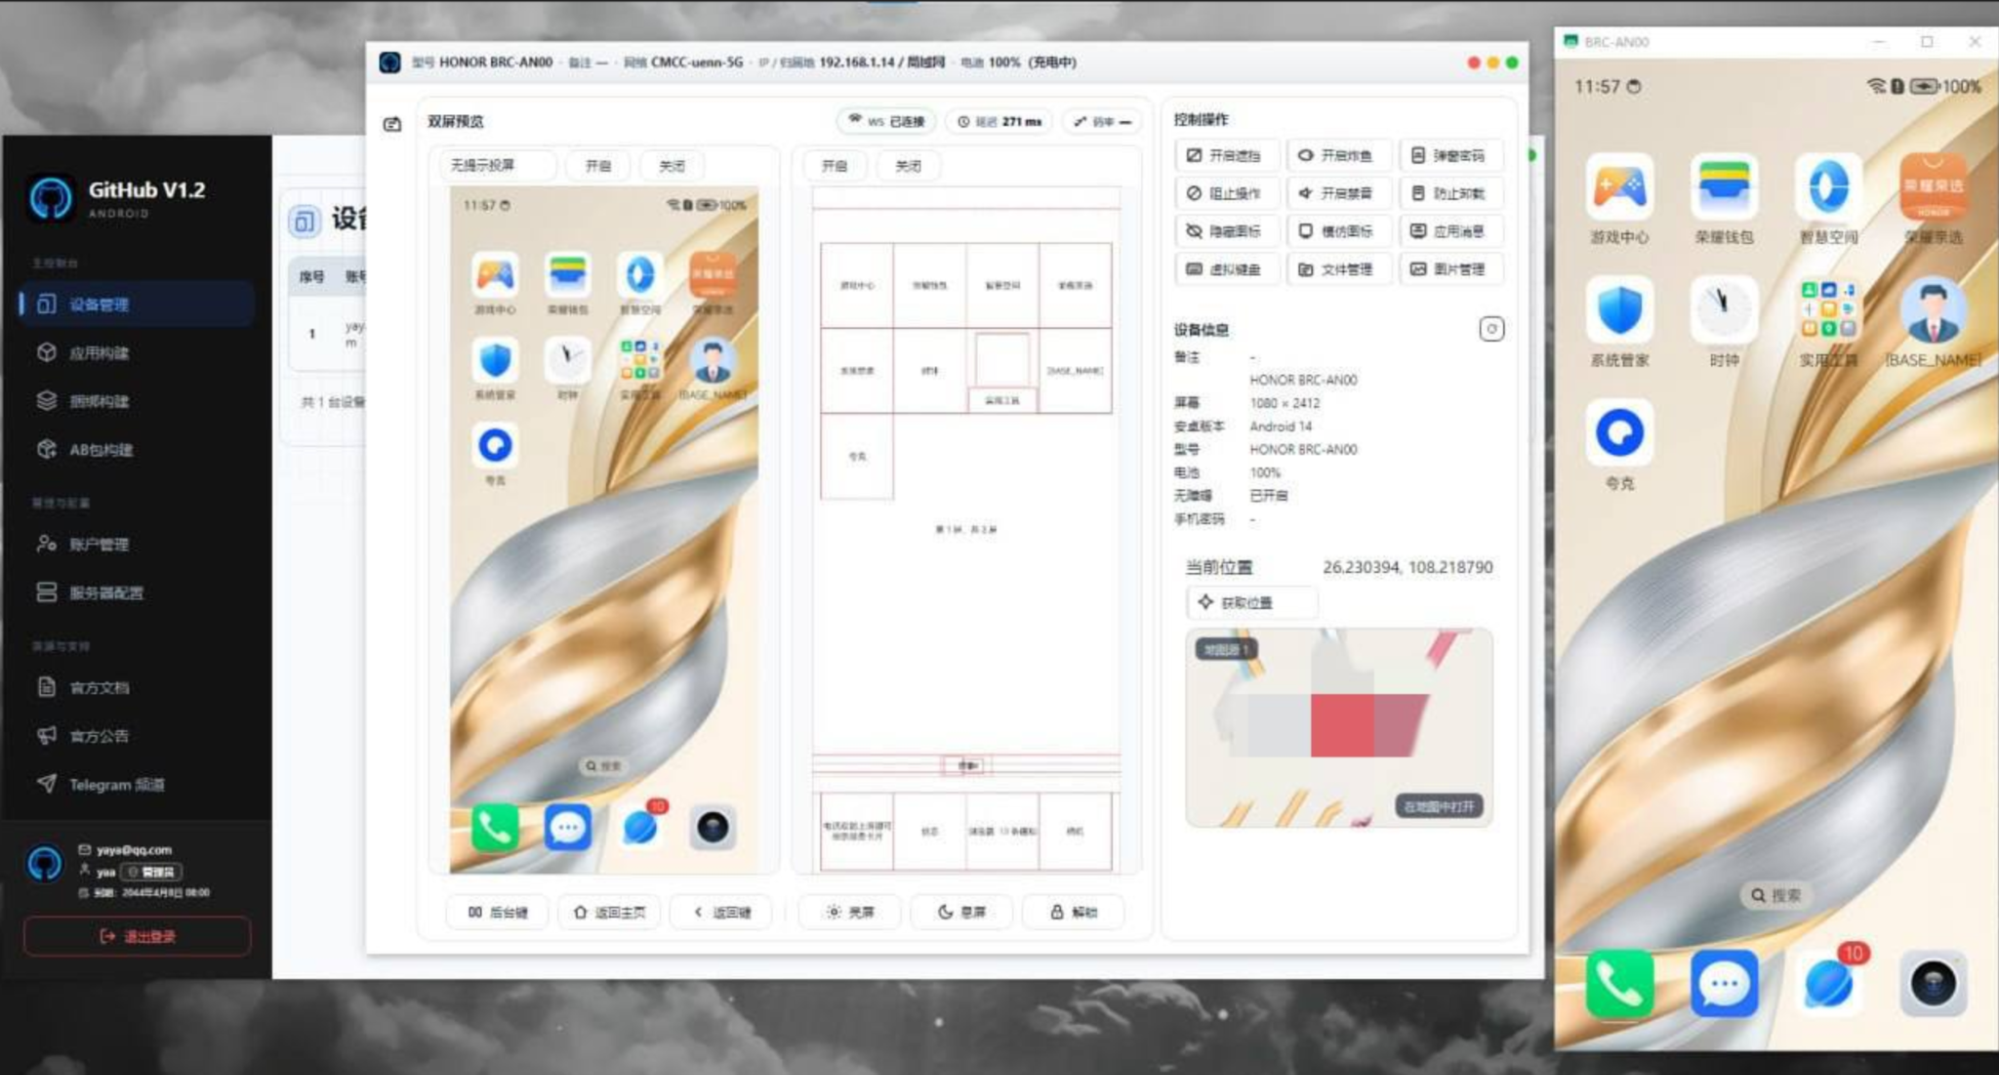
Researchers linked the Flying Eagle Android RAT to fake police apps, uncovering 170 servers in a growing cybercrime ecosystem. Hunt.io researchers and independent journalist NetAskari started with a fraudulent Android app impersonating a Chinese Provincial Public Security Bureau service and ended up mapping a sprawling criminal ecosystem built around a leaked Android RAT framework called […]
 Pierluigi Paganini
July 28, 2026
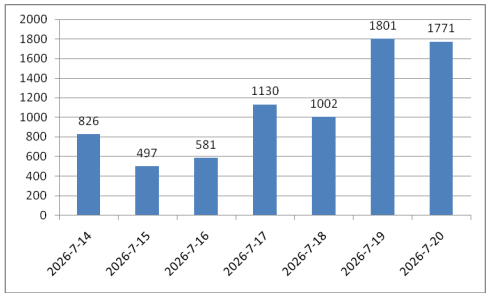
Researchers uncovered the 200,000-device Dysphoria botnet, which uses Ethereum and Solana domains to hide its command servers. QiAnXin XLab, jointly with China’s CNCERT, disclosed Dysphoria, a botnet that has compromised roughly 200,000 devices worldwide and uses Ethereum and Solana blockchain domain names to hide its command infrastructure. The botnet evolved from jackskid and fbot malware […]
 Pierluigi Paganini
July 28, 2026
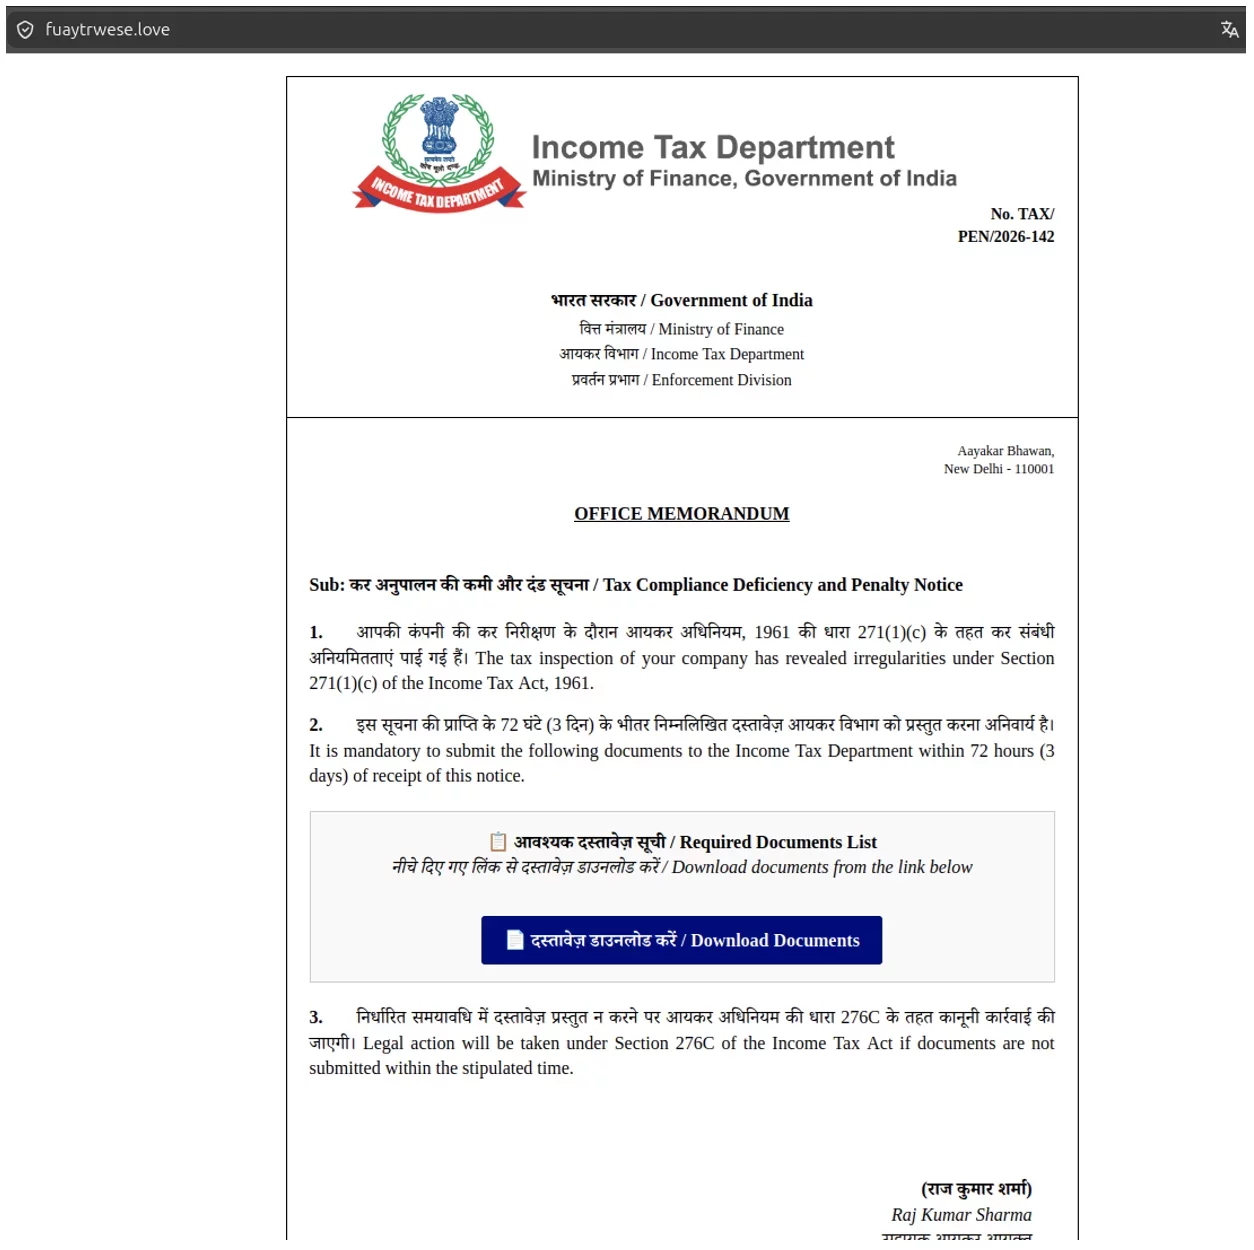
Proofpoint uncovered Cruciferra, a crypter-as-a-service that helps hackers evade antivirus and deliver malware in multiple campaigns. Proofpoint’s research team traced a wave of income-tax-themed lures targeting Indian taxpayers, tax professionals, and corporate finance teams back to a crypter service called Cruciferra, and the tool turns out to be shared infrastructure used across multiple unrelated criminal […]
 Pierluigi Paganini
July 27, 2026
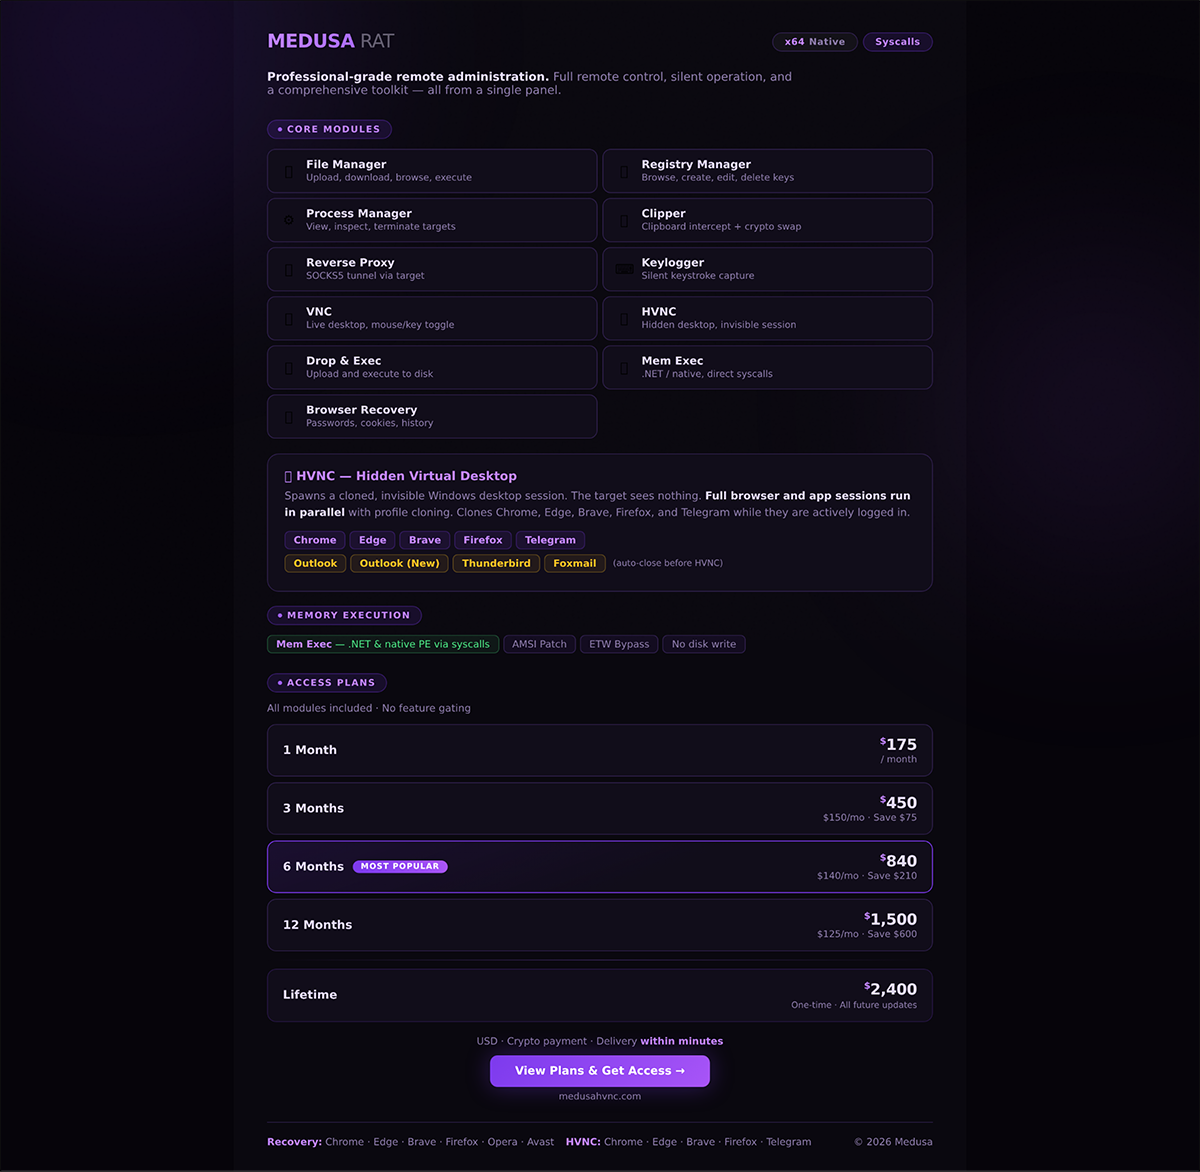
MedusaHVNC RAT uses hidden Windows desktops to remotely control browsers, steal data, and evade detection through legitimate system features. Windows has always supported hidden desktops as a legitimate feature, useful for specialized software that needs a workspace the user never touches. It’s a niche capability most people never think about, buried deep in how the […]
 Pierluigi Paganini
July 27, 2026
DentaQuest disclosed a data breach that may have exposed the personal and dental health information of more than 23 million people. DentaQuest is notifying more than 23 million people of a data breach after hackers accessed its network in May 2026. The incident may have exposed customers’ personal information and dental health data. DentaQuest, part […]
 Pierluigi Paganini
July 27, 2026
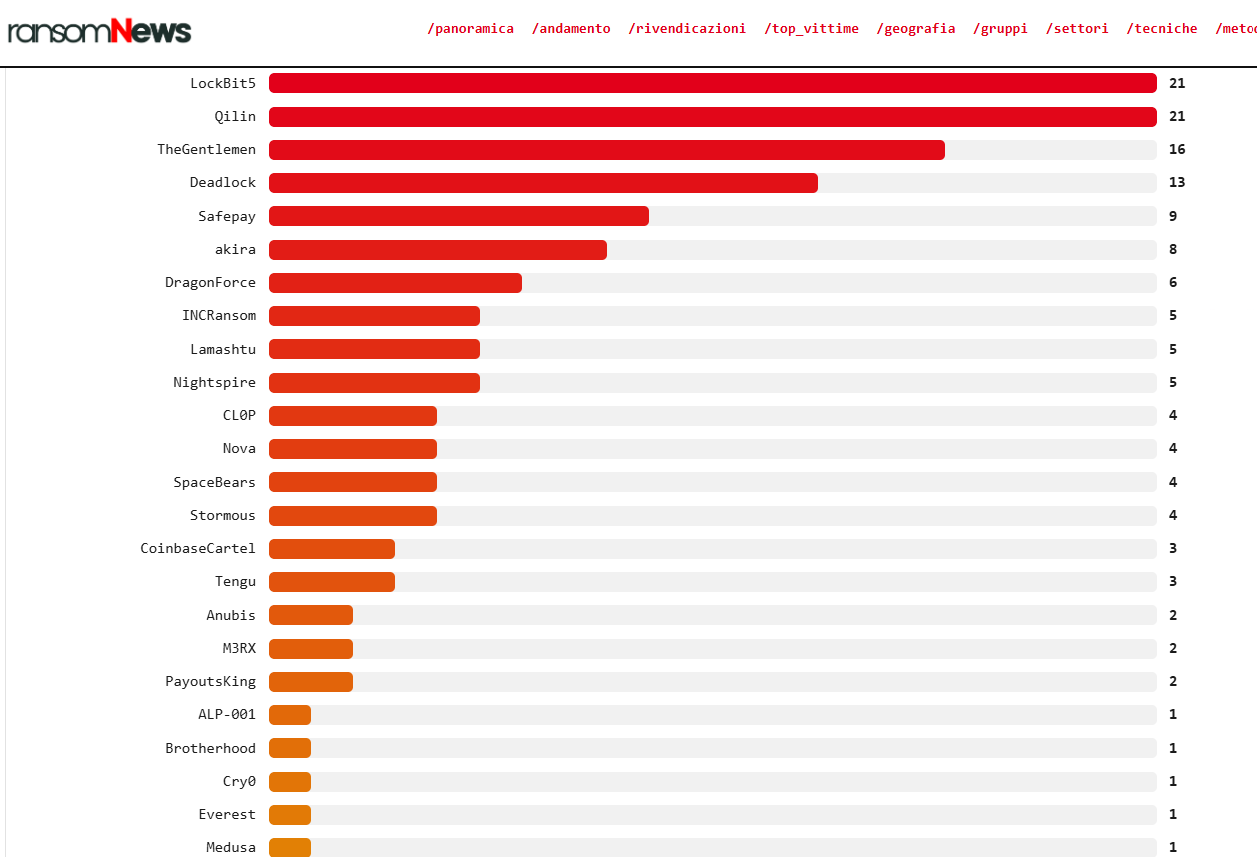
A new report links 148 ransomware attacks to Italian organizations in H1 2026, with manufacturing the most targeted sector. Six months, 148 confirmed ransomware claims against Italian targets, and one sector taking the brunt of it. That’s the headline number from a new semi-annual tracker compiled by ransomNews under its RedACT project, which pulls together […]
 Pierluigi Paganini
July 26, 2026
Security Affairs Malware newsletter includes a collection of the best articles and research on malware in the international landscape Malware Newsletter UAC-0145 Primary Compromise Vectors as of July 2026 SleeperGem: Compromised git_credential_manager, Dendreo, and fastlane RubyGems Drop a Persistent Backdoor AgentBaiting: How 800+ Fake AI Skills and MCP Servers Delivered Malware Chaos ransomware’s msaRAT: Living […]
Pierluigi Paganini
July 26, 2026
A new round of the weekly Security Affairs newsletter has arrived! Every week, the best security articles from Security Affairs are free in your email box. Enjoy a new round of the weekly SecurityAffairs newsletter, including the international press. Iran-Linked Actors Breach Are Targeting US Water and Energy Control Systems Australian energy provider Origin Energy […]







