 Pierluigi Paganini
 May 10, 2017
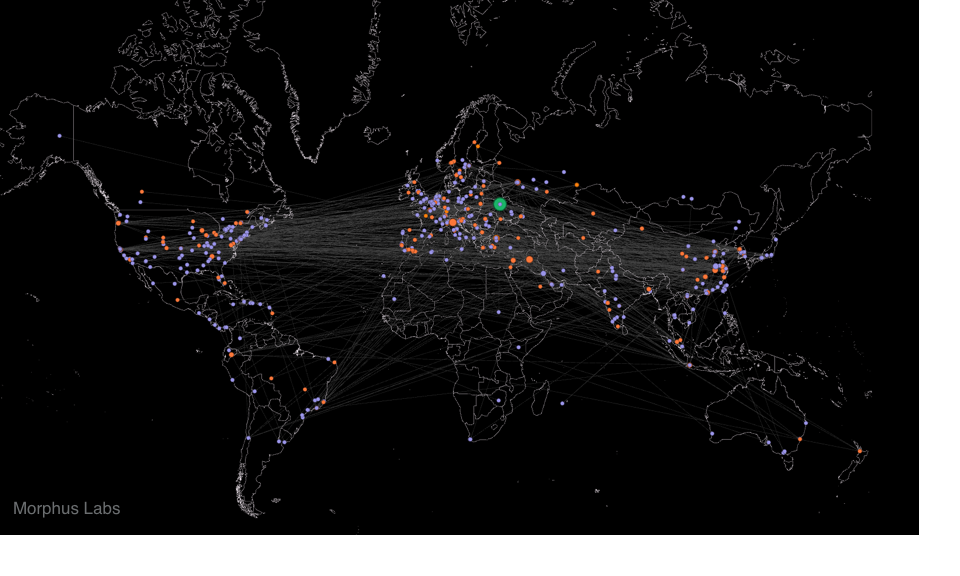
The Rakos botnet – Exploring a P2P Transient Botnet From Discovery to Enumeration. 1. Introduction We recently deployed a high interaction honeypots expecting it to be compromised by a specific malware. But in the first few days, instead of getting infected by the expected malware, it received a variety of attacks ranging from SSH port forwarding […]
 Pierluigi Paganini
May 09, 2017
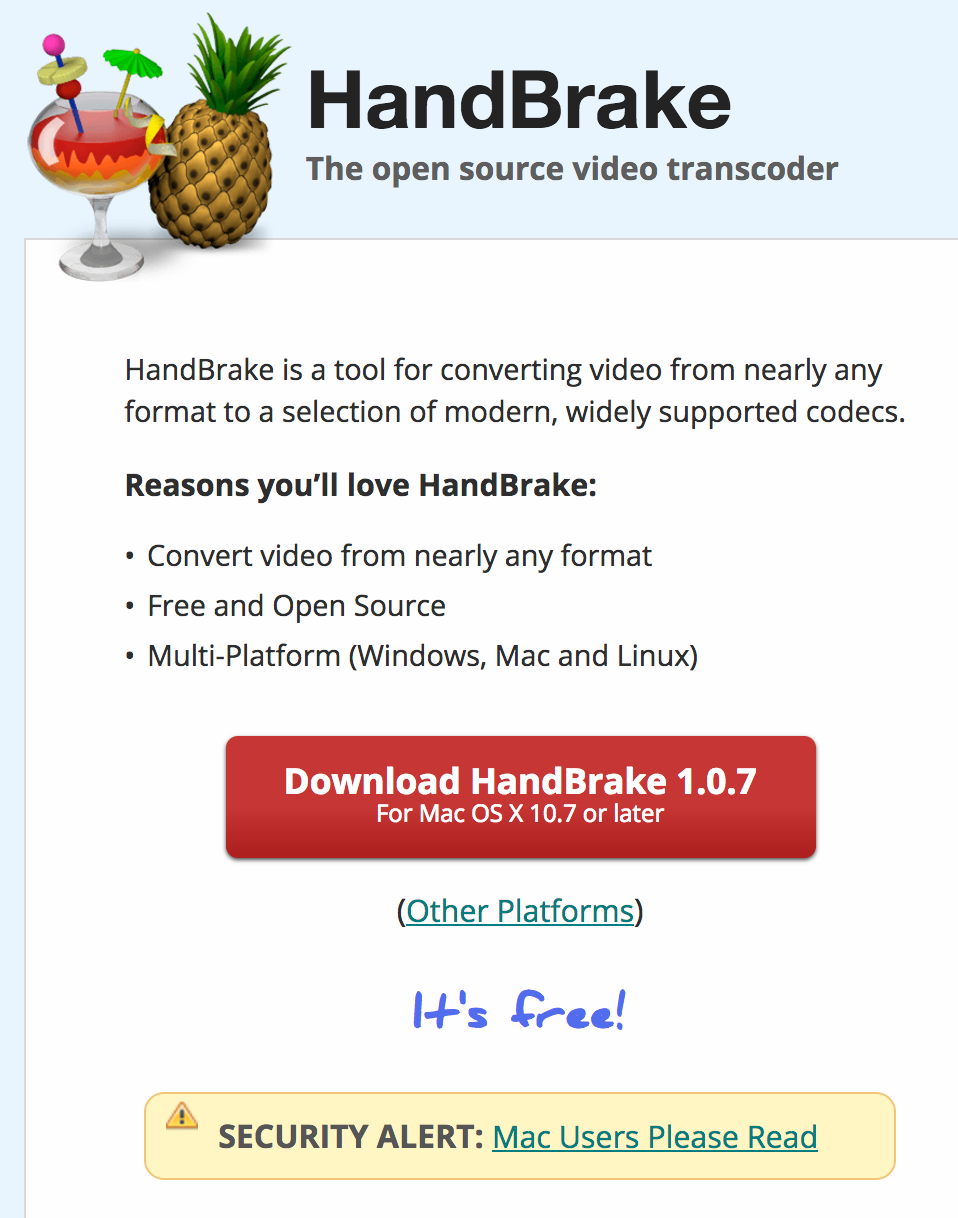
Maintainers of the HandBrake video transcoder are warning Mac users who recently downloaded the software that they may have been infected with malware. Maintainers of the open-source HandBrake video transcoder are warning Mac users who recently downloaded the application that they may have been infected with malware.Mac users who downloaded and installed the program from May […]
 Pierluigi Paganini
May 08, 2017
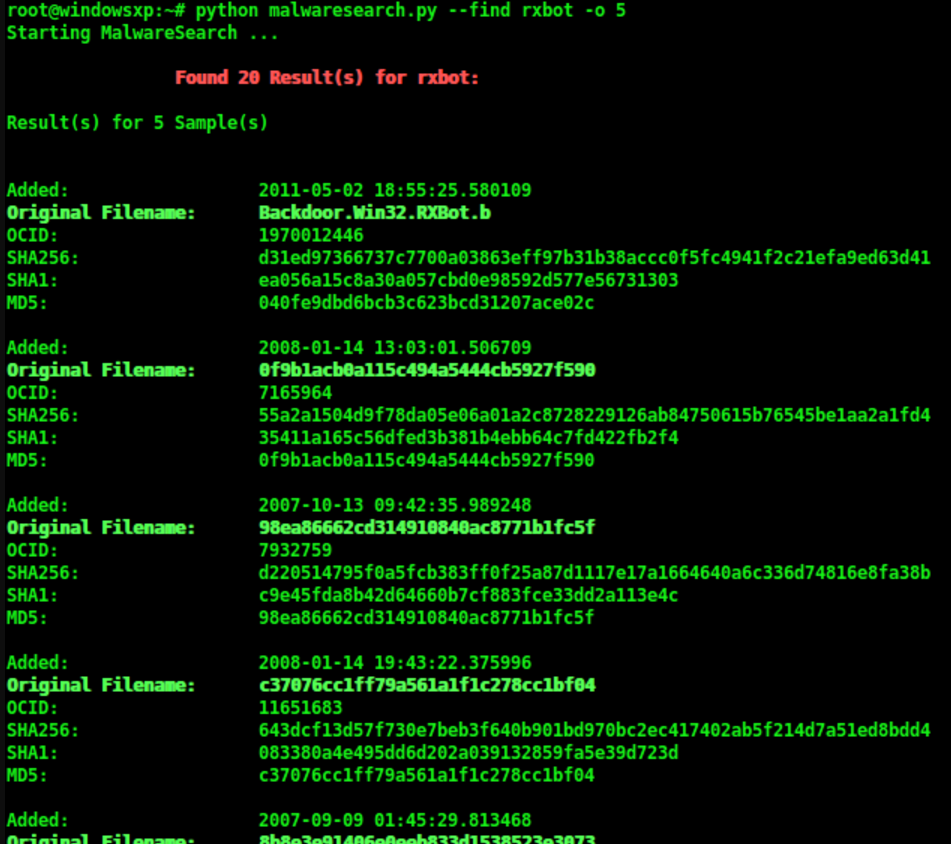
Malwaresearch is a command line tool to find malware on Openmalware.org, it was developed to facilitate and speed up the process of finding and downloading malware samples. The tool was developed to facilitate and speed up the process of finding and downloading malware samples via the command line interface. We’ve made use of the API provided by […]
 Pierluigi Paganini
May 08, 2017
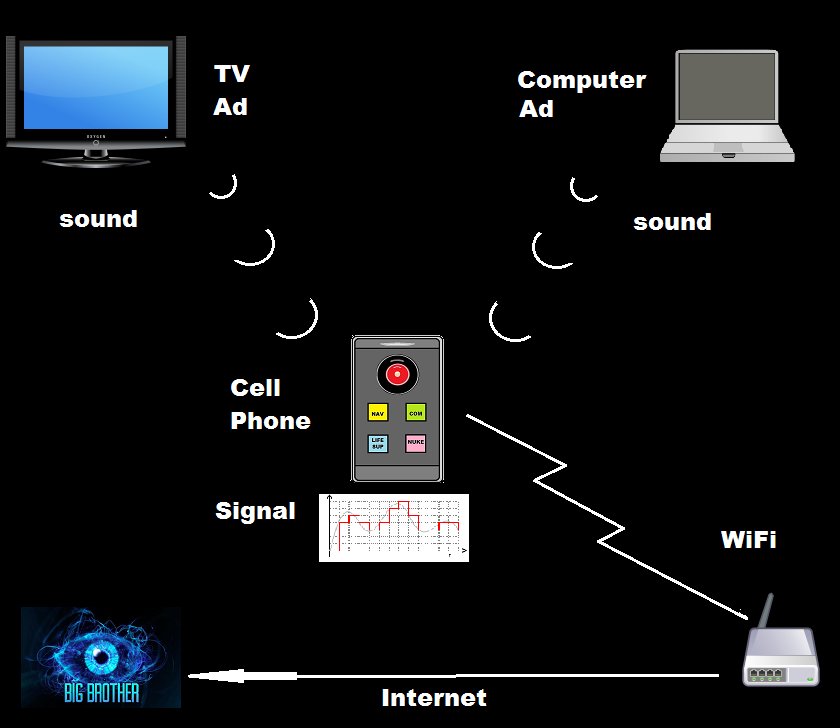
Researchers at Technische Universitat Braunschweig published a study on 200+ Android mobile apps that are listening to your life through ultrasonic beacons. Researchers at Technische Universitat Braunschweig in Germany recently published a finding that over 200 Android mobile applications are listening to your life through ultrasonic beacons. Like digital electronic vampire bats, these apps are checking […]
 Pierluigi Paganini
May 08, 2017
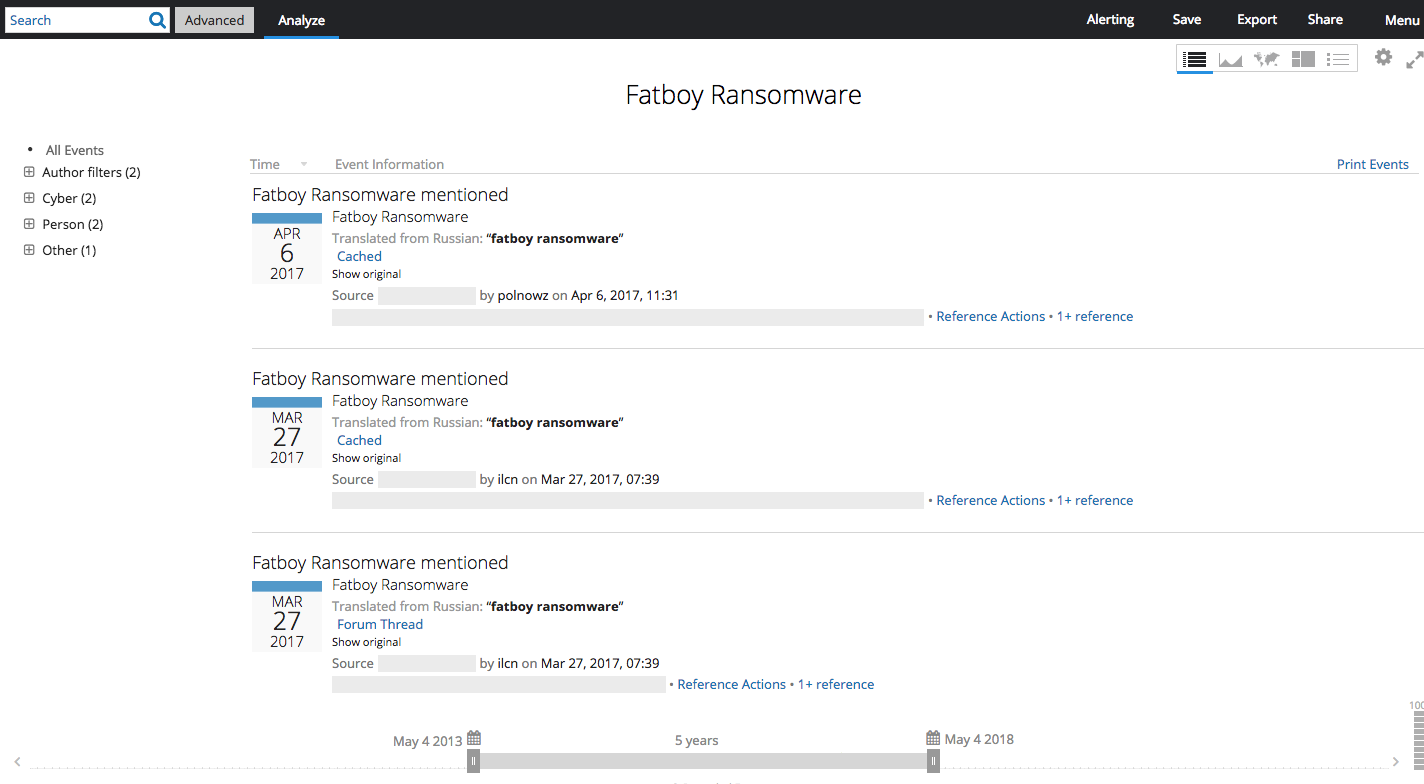
Recently discovered Fatboy ransomware implements a dynamic method of setting the ransom amount based on the geographic location of the victims. Ransomware continues to monopolize the threat landscape, recently security experts have observed numerous evolution of this specific family of malware. A newly discovered ransomware-as-a-service (RaaS), dubbed Fatboy, implements a dynamic method of setting the […]
 Pierluigi Paganini
May 06, 2017
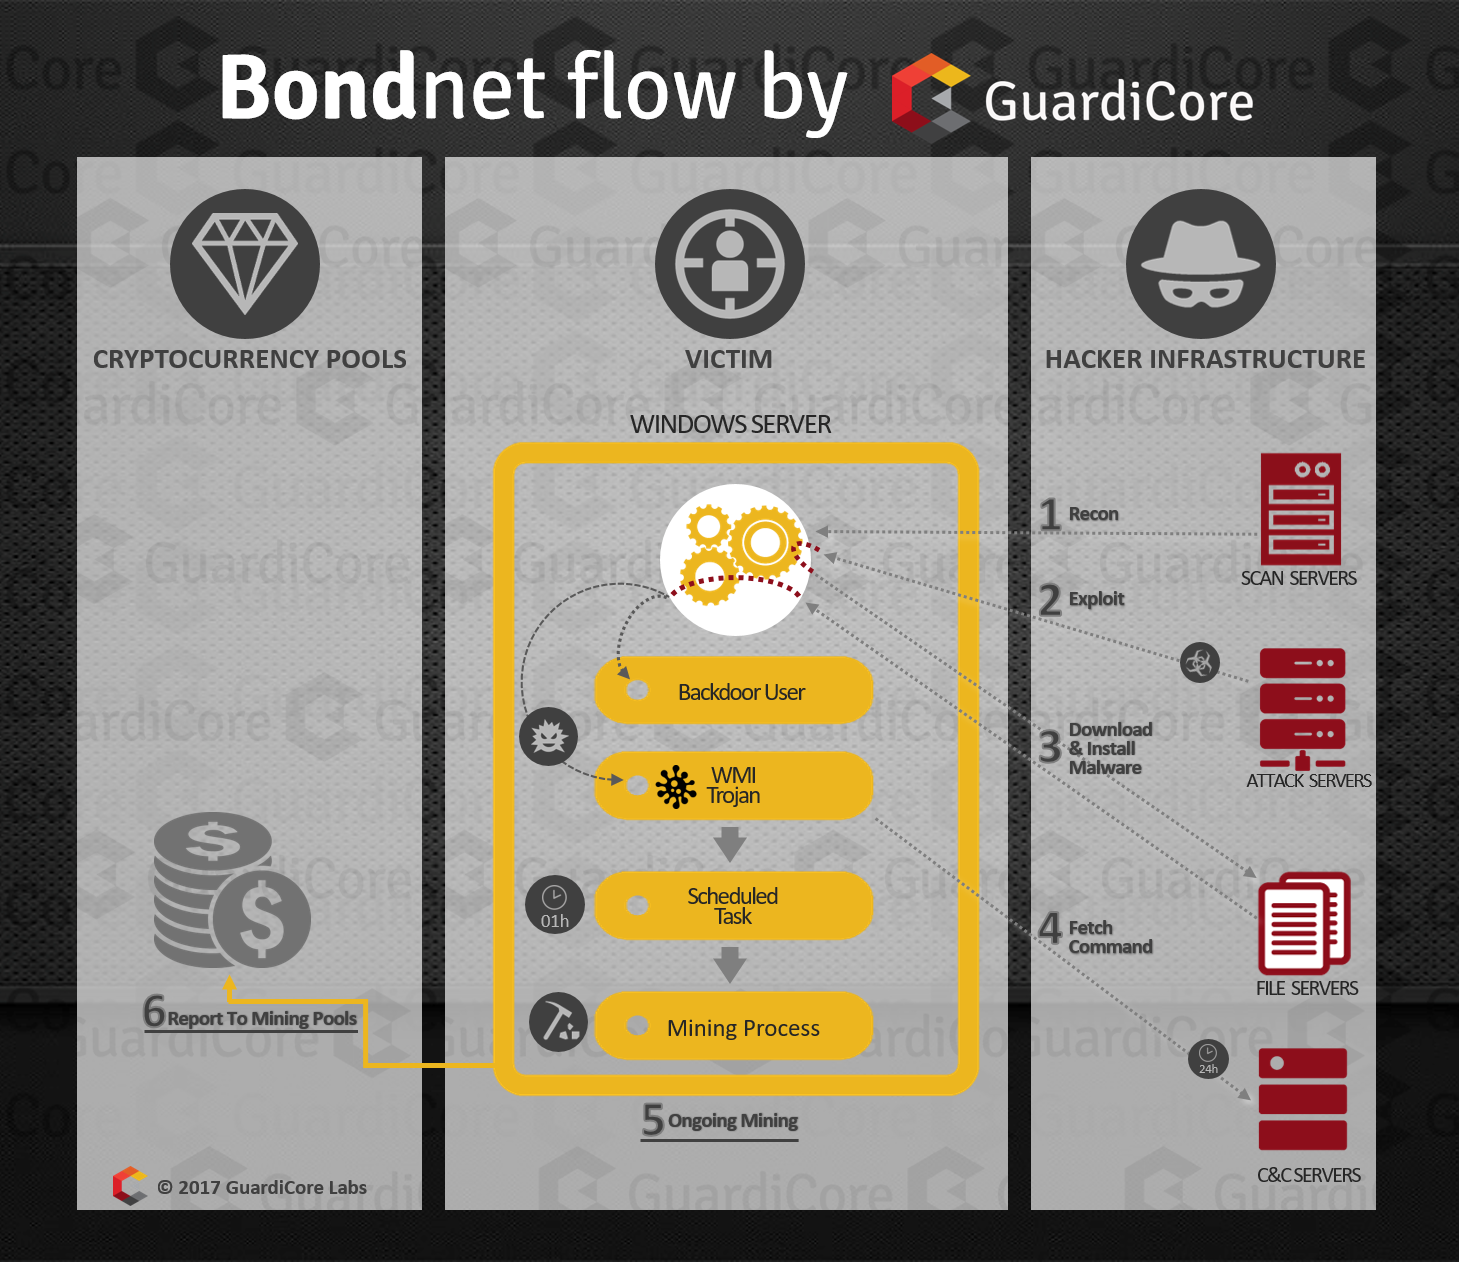
The new Bondnet botnet “Bond007.01” recently discovered coming out of China and it has infected an estimated 15,000 Windows server computers world-wide. There’s a new botnet in town and it’s named after the spy with a license to kill – James Bond. The new Bondnet botnet “Bond007.01” was discovered coming out of China by researchers […]
 Pierluigi Paganini
May 06, 2017
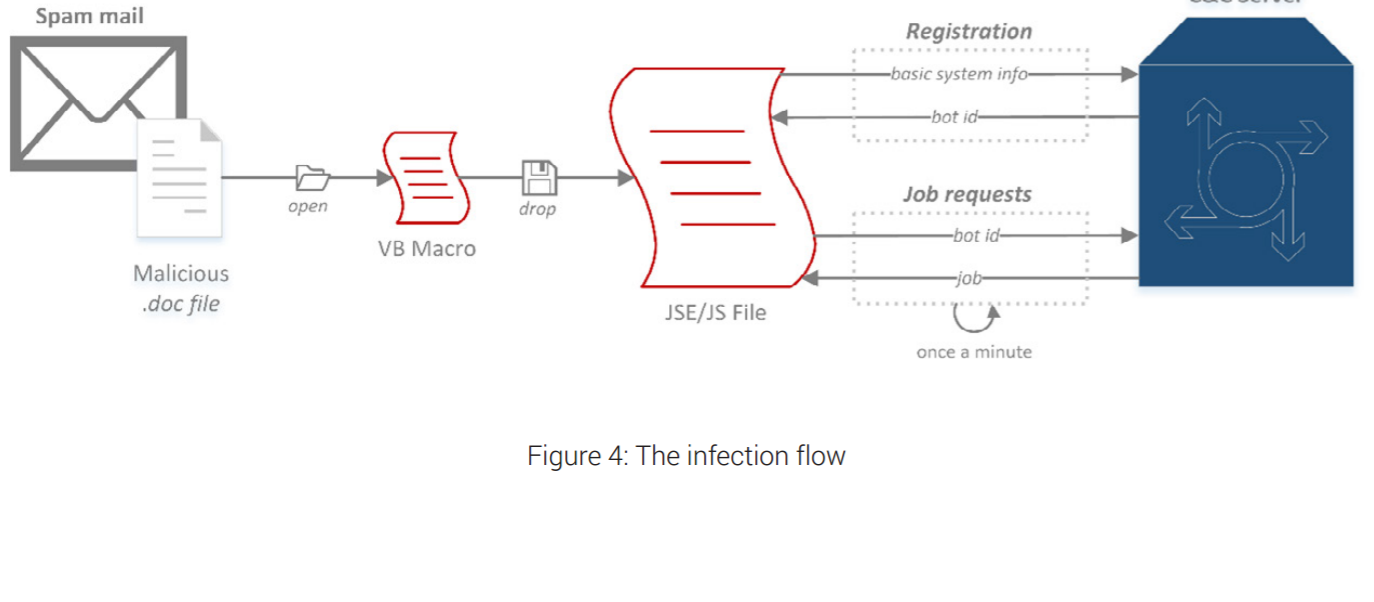
Experts from Bitdefender have uncovered the Netrepser Cyber espionage campaign that compromised more than 500 Government organizations worldwide. Security experts at Bitdefender uncovered a cyber espionage campaign that leverages a strain of malware dubbed Netrepser to target government organizations. Netrepser Trojan samples were first discovered by the Bitdefender in May 2016, according to experts the analysis […]
 Pierluigi Paganini
May 05, 2017
According to experts from the Fox-IT firm, the notorious Russian Snake APT group is ready to target also Mac users with a new variant of its malicious code. The sophisticated Russian Snake APT group is back and is leveraging on new malware to target Mac users.The Snake APT group, also known as Turla or Uroburos, has ported its Windows […]
 Pierluigi Paganini
May 05, 2017
Cisco Talos team discovered a RAT dubbed KONNI malware that target organizations linked to North Korea. Here you are an analysis of its evolution. Security researchers at Cisco Talos team have discovered a remote access Trojan (RAT) that target organizations linked to North Korea. The malware, dubbed by researchers “KONNI,” was undetected for more than 3 years and […]
 Pierluigi Paganini
May 04, 2017
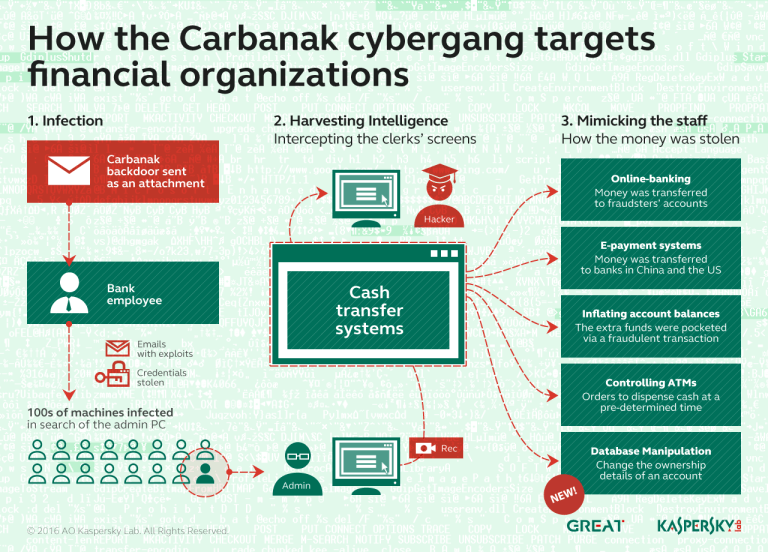
The notorious cyber crime gang Carbanak is back and it is continuing to refine its techniques and tactics and developed new tools for its attacks. The cyber crime gang Carbanak continues to refine its techniques and tactics. According to a new analysis conducted by the security firm Trustwave, the group has refined its intrusion strategy and […]