 Pierluigi Paganini
 May 03, 2017
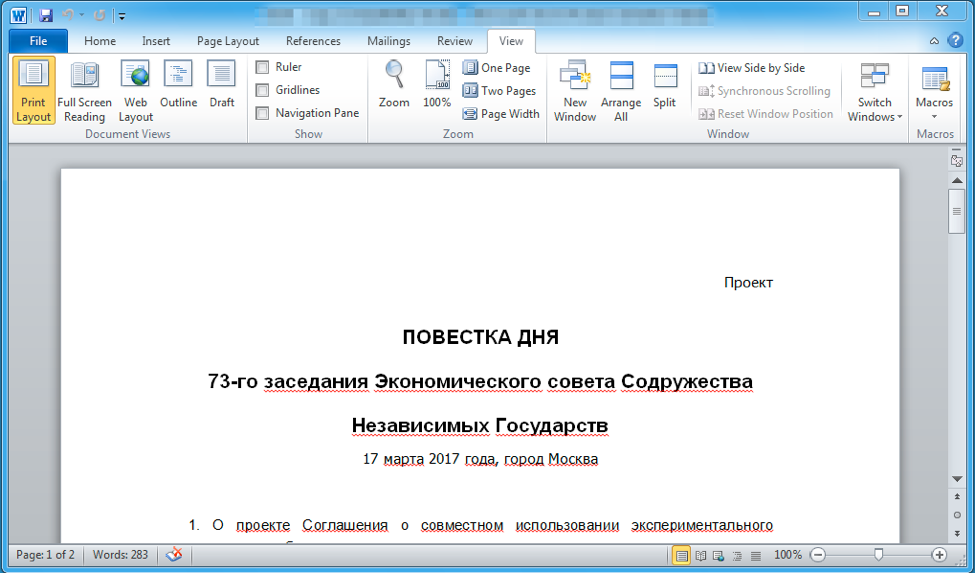
Malware researchers at security firm ProofPoint reported the Chinese TA459 APT has exploited the CVE-2017-0199 vulnerability to target Financial firms. The notorious cyber espionage group tracked as TA459 APT has targeted analysts working at major financial firms using the recently patched CVE-2017-0199 Microsoft Office vulnerability. Experts at Proofpoint published a detailed analysis of the espionage campaign conducted […]
 Pierluigi Paganini
May 03, 2017
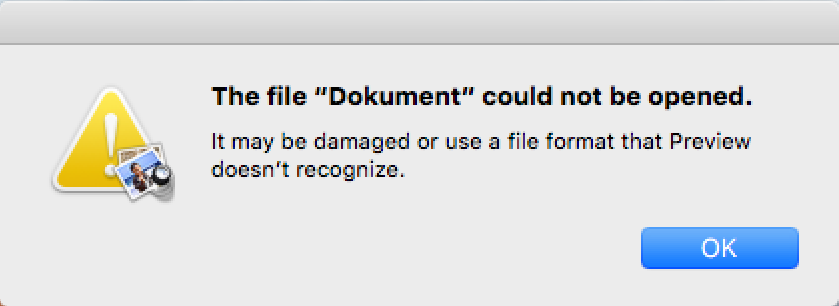
Bad news for Mac users, a new variant of the OSX.Dok dropper was discovered by researchers at Malwarebytes, it was spotted installing a new payload dubbed Bella backdoor. Once the DOK malware infects a macOS system, it gains administrative privileges and installs a new root certificate. The root certificate allows the malicious code to intercept all victim’s […]
 Pierluigi Paganini
May 02, 2017
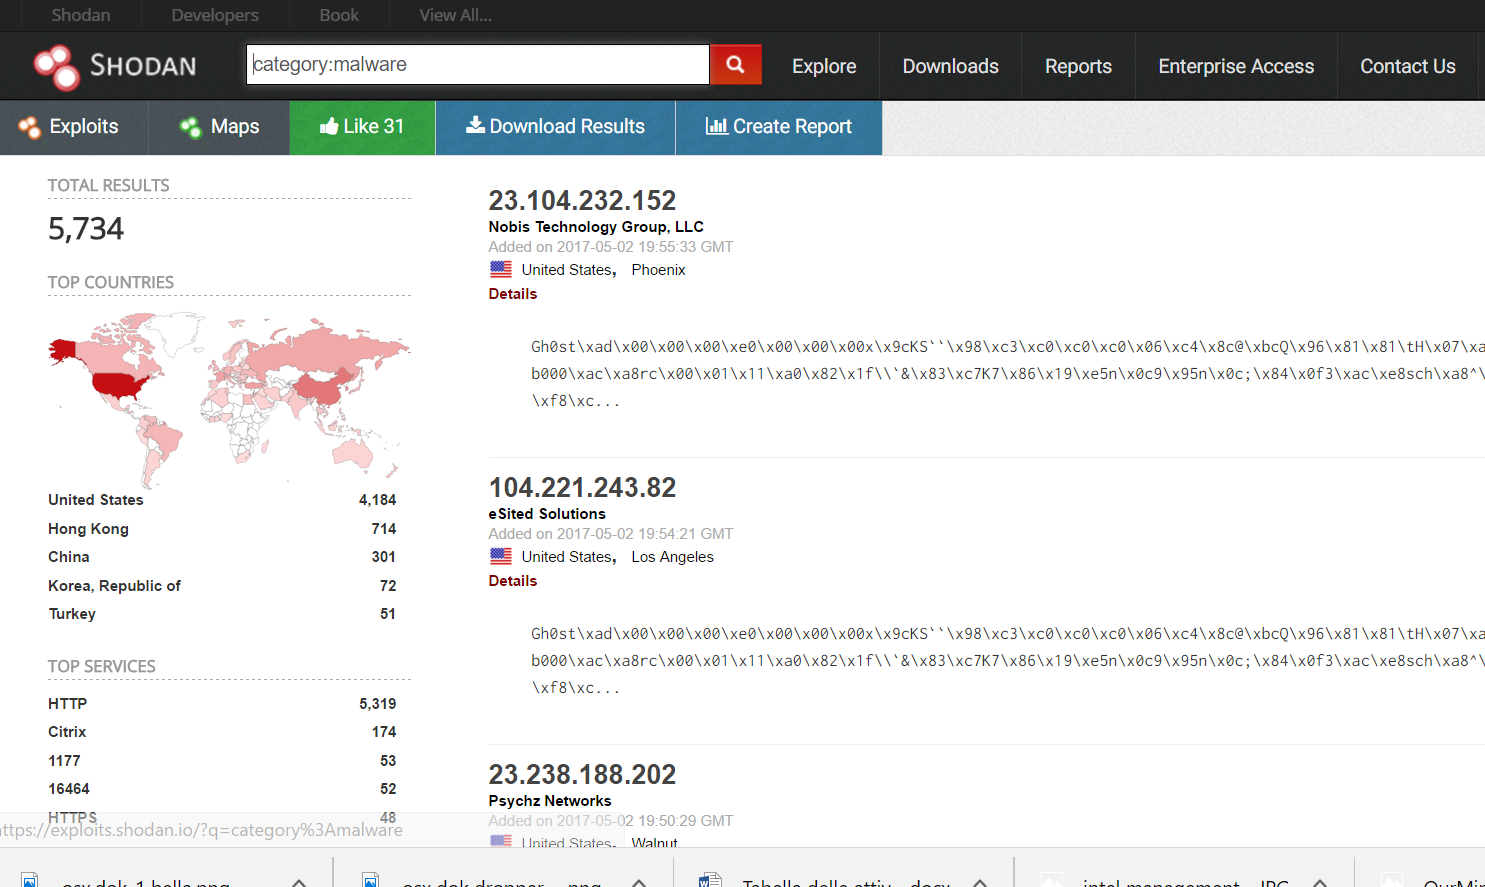
Shodan and security firm Recorded Future launched Malware Hunter, a service that allows scanning the Internet to identify botnet C&C servers. Malware researchers have a new powerful weapon in their arsenal, a joint project from Shodan and security firm Recorded Future dubbed Malware Hunter allow them to scan the Internet to identify botnet C&C servers. The malware […]
 Pierluigi Paganini
May 02, 2017
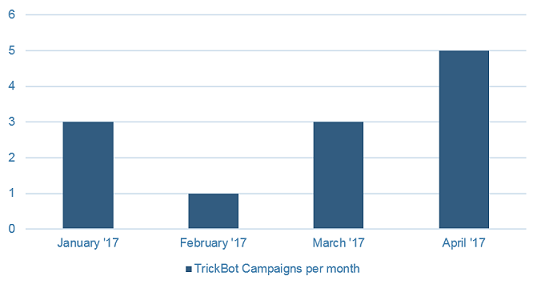
According to a new analysis conducted by the IBM’s X-Force security team, a new wave of attacks powered by the TrickBot banking Trojan have been targeting private banks in the UK, Australia, and Germany. The researchers observed new redirection attacks focused on new brands, including private banks, private wealth management firms, investment banking, and a retirement insurance and […]
 Pierluigi Paganini
April 30, 2017
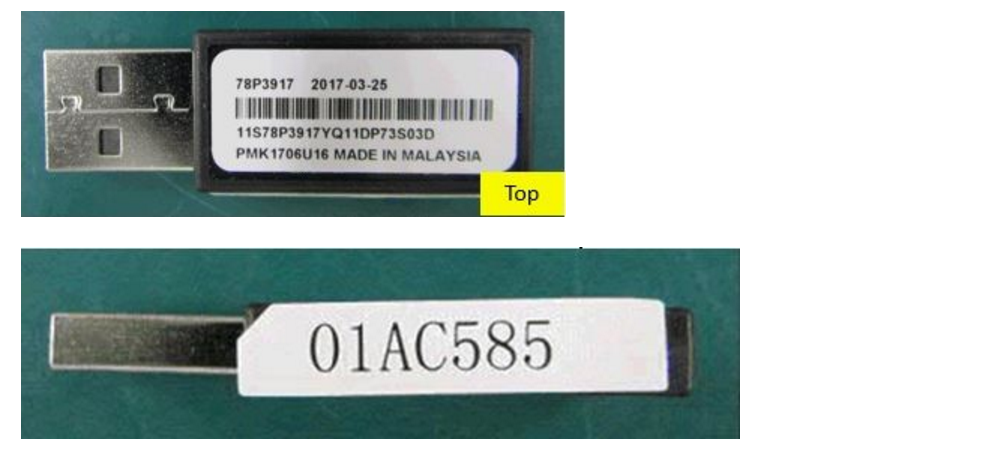
Some USB flash drives containing the initialization tool shipped with the IBM Storwize for Lenovo contain a malicious file. Some USB flash drives containing the initialization tool shipped with the IBM Storwize for Lenovo V3500, V3700 and V5000 Gen 1 storage systems contain a file that has been infected with malicious code. The Initialization Tool […]
 Pierluigi Paganini
April 28, 2017
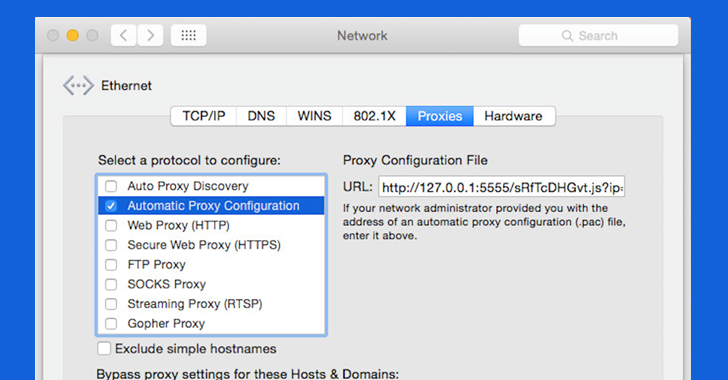
DOK Malware is a stealthy malicious code recently discovered by researchers at security firm CheckPoint, it affects almost ant Mac OS X version. Malware researchers at CheckPoint firm have discovered a new stealth Mac malware dubbed DOK that affects almost ant Mac OS X version. At the time of its discovery, the DOK malware has zero […]
 Pierluigi Paganini
April 27, 2017
Security experts from security firm Redsocks published an interesting report on how to crack APT28 traffic in a few seconds. Introduction APT28 is a hacking group involved in many recent cyber incidents. The most recent attack allegedly attributed to this group is the one to French presidential candidate Emmanuel Macron’s campaign. Incident response to this Advanced […]
 Pierluigi Paganini
April 27, 2017
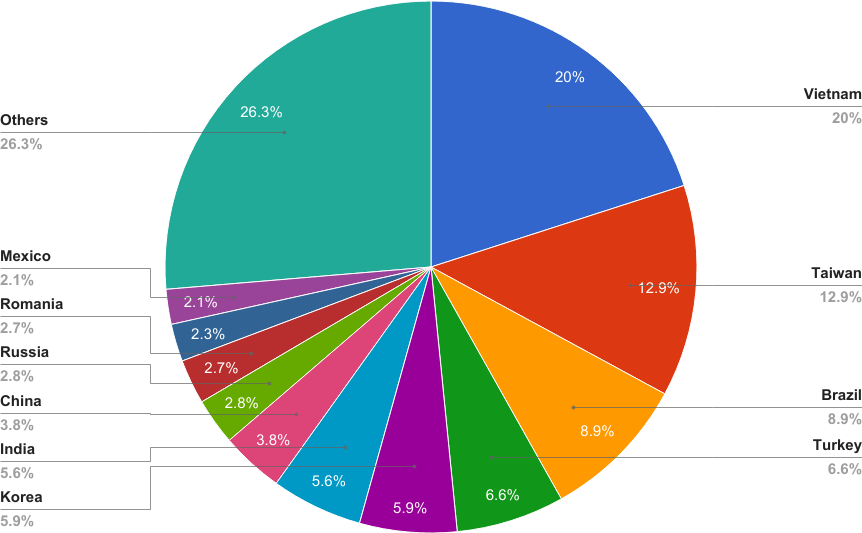
The mysterious Hajime Botnet continues to grow and reached 300,000 IoT Devices, the author also implemented a new attack method. Recently experts from Symantec spotted a new IoT botnet dubbed Hajime that is spreading quickly in the last months, mostly in Brazil and Iran. The Hajime malware was first spotted in October 2016, it implements the same mechanism […]
 Pierluigi Paganini
April 25, 2017
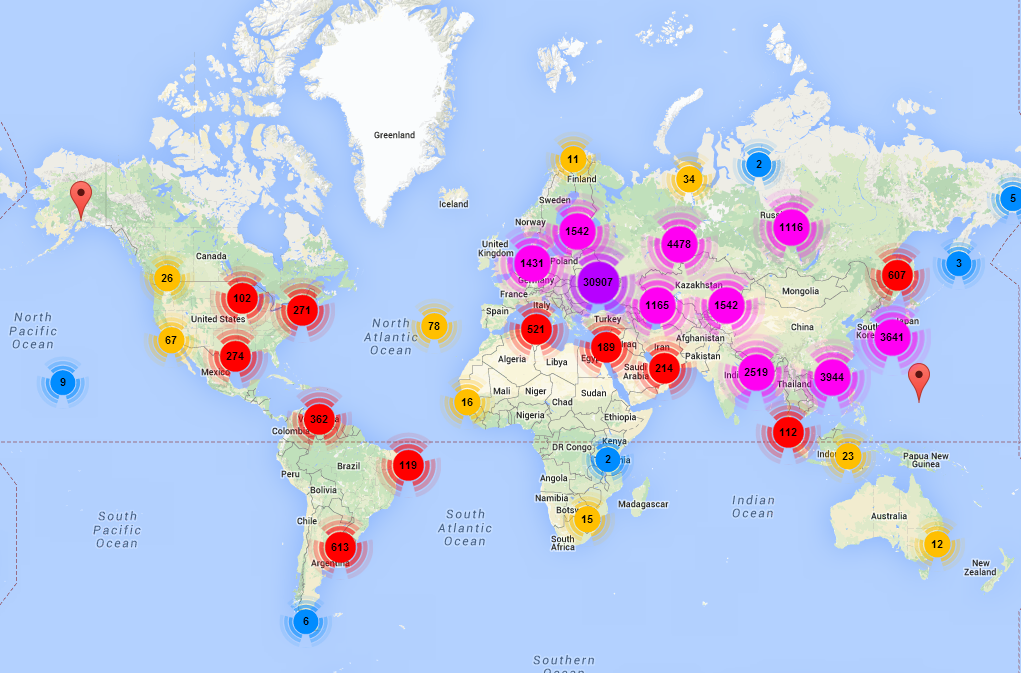
Malware researchers from security firm ESET have discovered a new Linux threat dubbed Shishiga malware targeting systems in the wild. Malware researchers from ESET have discovered a new Linux malware dubbed Linux/Shishiga targeting systems in the wild. The Linux/Shishiga malware uses four different protocols (SSH, Telnet, HTTP and BitTorrent) implements a modular architecture by using Lua scripts. […]
 Pierluigi Paganini
April 24, 2017
The Russian hacker Petr Levashov has been indicted in connection with the infamous Kelihos Botnet that was recently dismantled. It isn’t a good period for Russian cyber criminals, last week Roman Valeryevich Seleznev, aka “Track2”, was sentenced to 27 years in prison, he was convicted of causing $170 million in damage by hacking into point-of-sale systems. Today the […]