 Pierluigi Paganini
 May 27, 2017
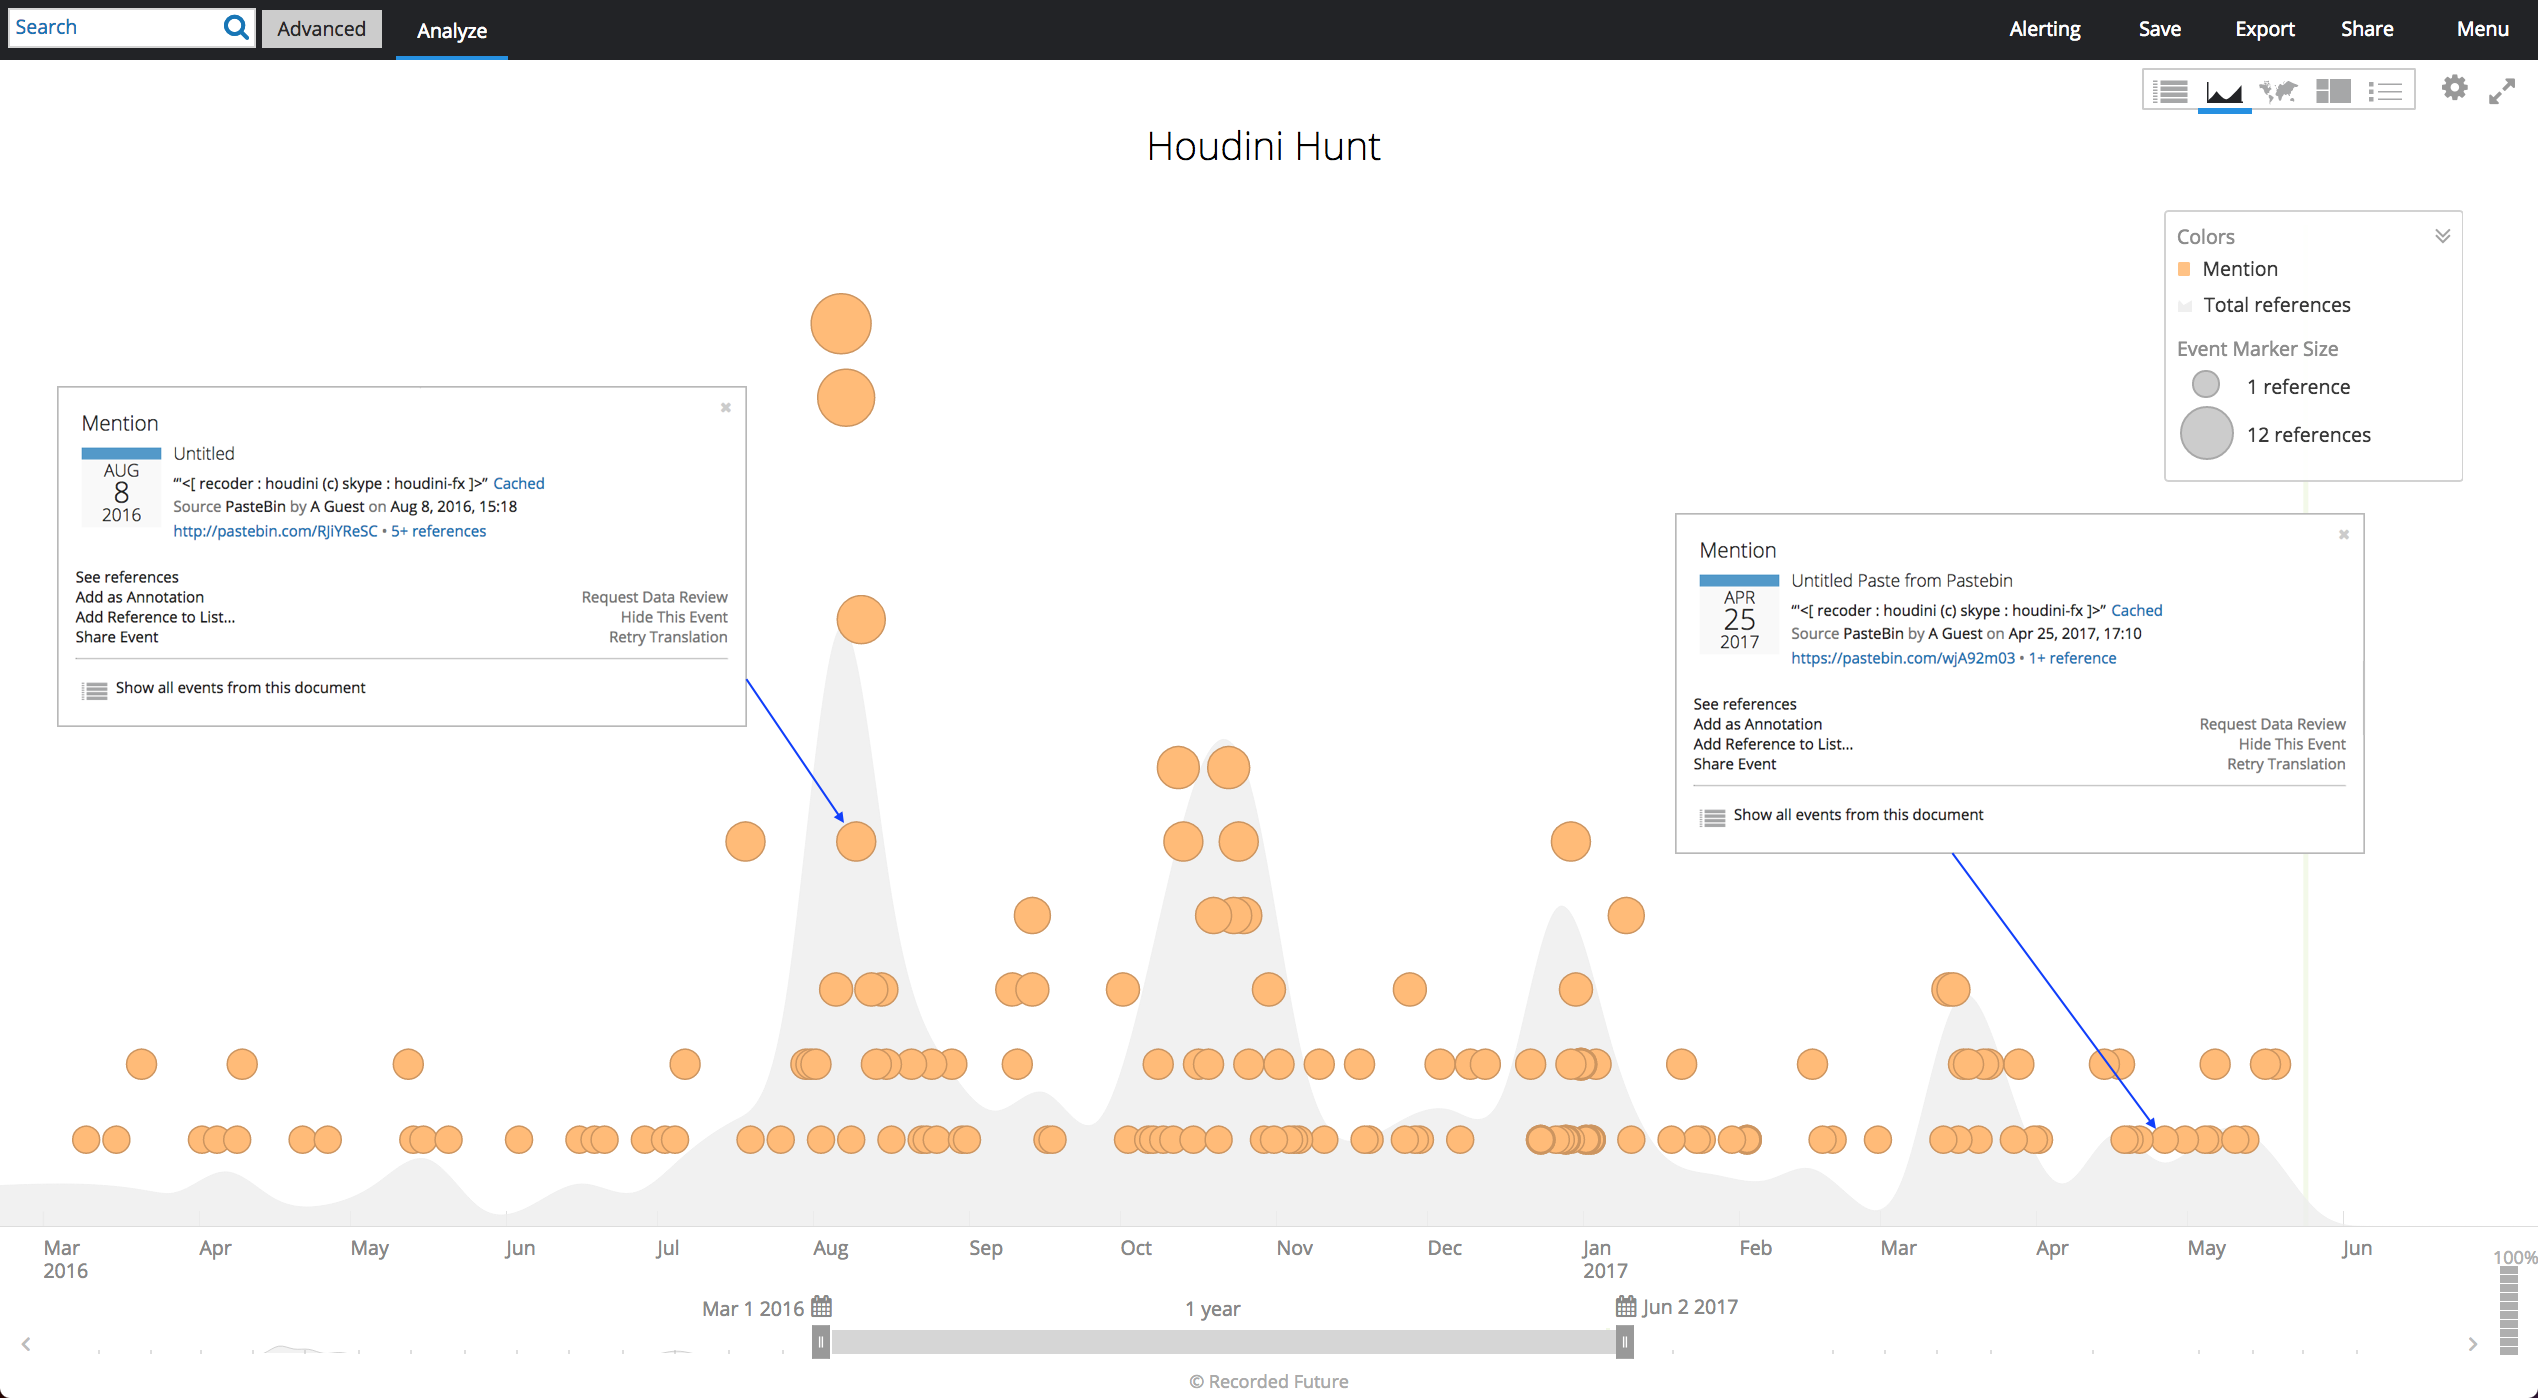
Security experts at Recorded Future tracked a German hacker for the propagation of the Houdini worm through Pastebin sites. A German hacker that goes online with the moniker Vicswors Baghdad is the responsible for the propagation of the Houdini malware on Pastebin sites. According to the expert at Recorded Future, the same threat actor appears to be […]
 Pierluigi Paganini
May 25, 2017
Researchers at ESET security firm have discovered that someone has released 200 master keys for the latest variants of the prominent Crysis ransomware. While security experts continue to investigate the WannaCry attack, someone has released 200 master keys for the latest variants of the prominent Crysis ransomware. The file encrypted by this version have the .wallet and […]
 Pierluigi Paganini
May 23, 2017
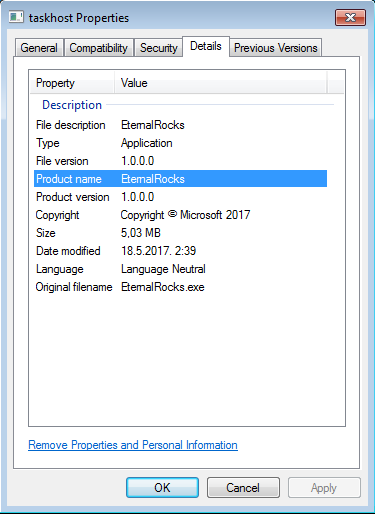
A security expert discovered a new worm, dubbed EternalRocks, that exploits the EternalBlue flaw to spread itself like WannaCry ransomware. The security expert Miroslav Stampar, a member of the Croatian Government CERT, has discovered a new worm, dubbed EternalRocks, that exploits the EternalBlue flaw in the SMB protocol to spread itself like the popular WannaCry ransomware. […]
 Pierluigi Paganini
May 22, 2017
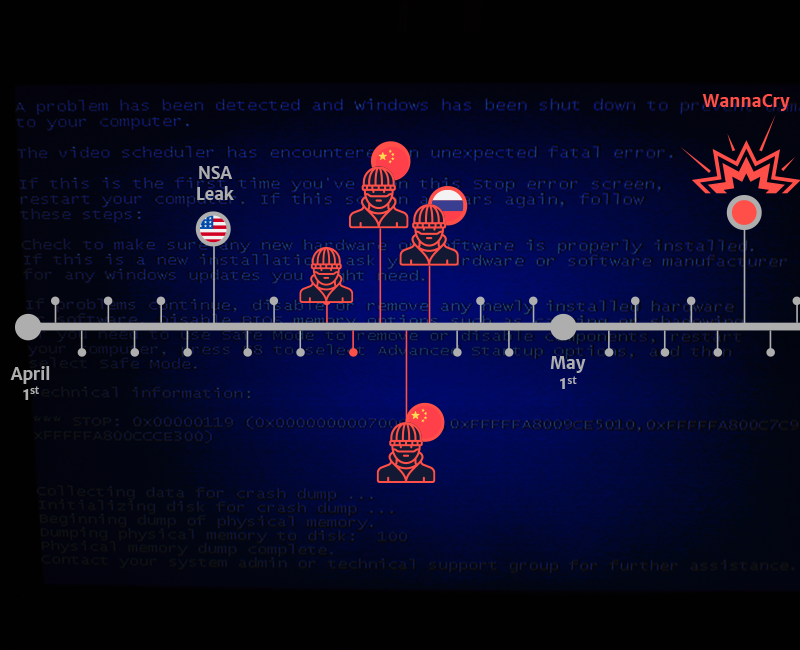
At least 3 different groups have been leveraging the NSA EternalBlue exploit weeks before the WannaCry attacks, here’s the evidence. In the last days, security experts discovered numerous attacks that have been leveraging the same EternalBlue exploit used by the notorious WannaCry ransomware. The Shadow Brokers hacker group revealed the exploit for the SMB vulnerability in April, but […]
 Pierluigi Paganini
May 22, 2017
Experts from Talos Team discovered changes made to the Terror exploit kit (EK) that allow it to fingerprint victims and target specific vulnerabilities. Recent changes made to the Terror exploit kit (EK) allow it to fingerprint victims and target specific vulnerabilities instead of carpet bombing the victims with many exploits at the same time, Talos […]
 Pierluigi Paganini
May 21, 2017
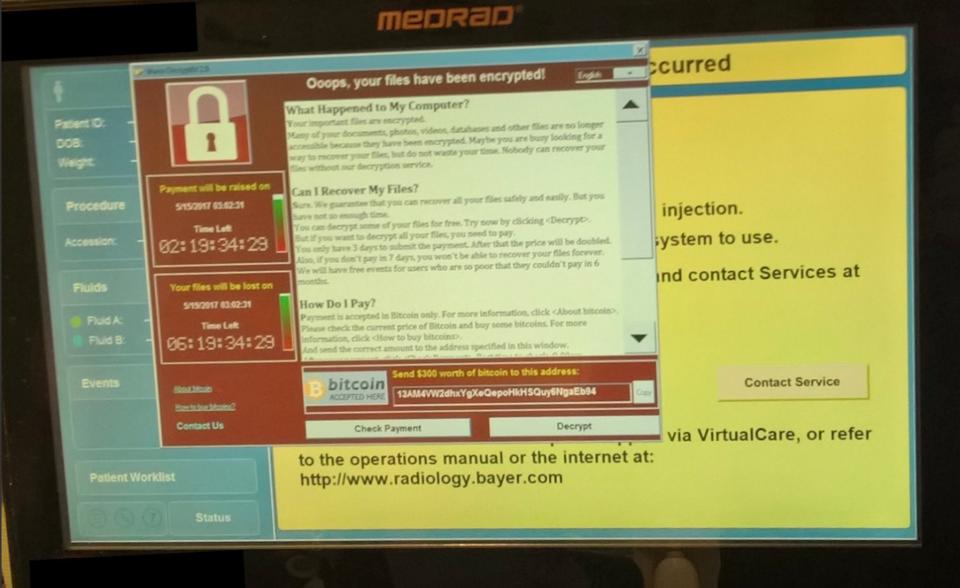
According to Forbes, the dreaded WannaCry ransomware has infected medical devices in at least two hospitals in the United States. WannaCry infected 200,000 computers across 150 countries in a matter of hours last week, it took advantage of a tool named “Eternal Blue”, originally created by the NSA, which exploited a vulnerability present inside the earlier […]
 Pierluigi Paganini
May 20, 2017
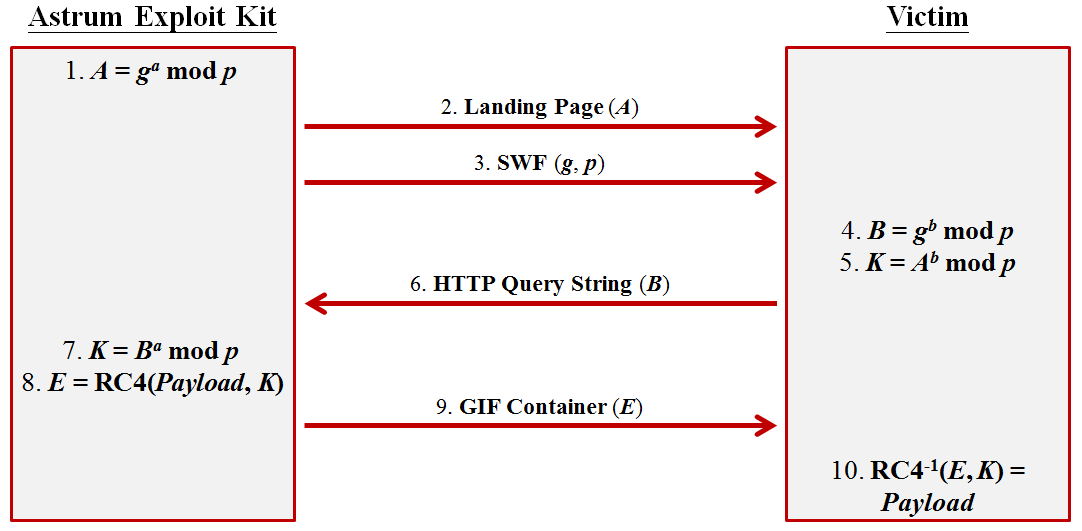
The Stegano exploit kit, also known as Astrum, continues to evolve, recently its authors adopted the Diffie-Hellman algorithm to hinder analysis. The Stegano exploit kit made was associated in the past with a massive AdGholas malvertising campaign that delivered malware, mostly Gozi and RAMNIT trojans. Experts at TrendMicro also observed the exploit kit in the Seamless malvertising campaign. “Astrum’s […]
 Pierluigi Paganini
May 20, 2017
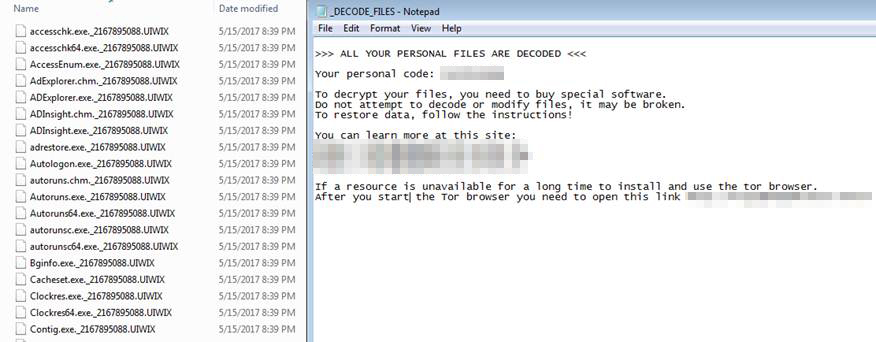
Security experts discovered a new ransomware family, dubbed UIWIX, that uses the NSA-linked EternalBlue exploit for distribution The effects of the militarization of the cyberspace are dangerous and unpredictable. A malicious code developed by a government could create serious problems for the Internet users, the recent WannaCry massive attack demonstrates it that used the EternalBlue Exploit to […]
 Pierluigi Paganini
May 19, 2017
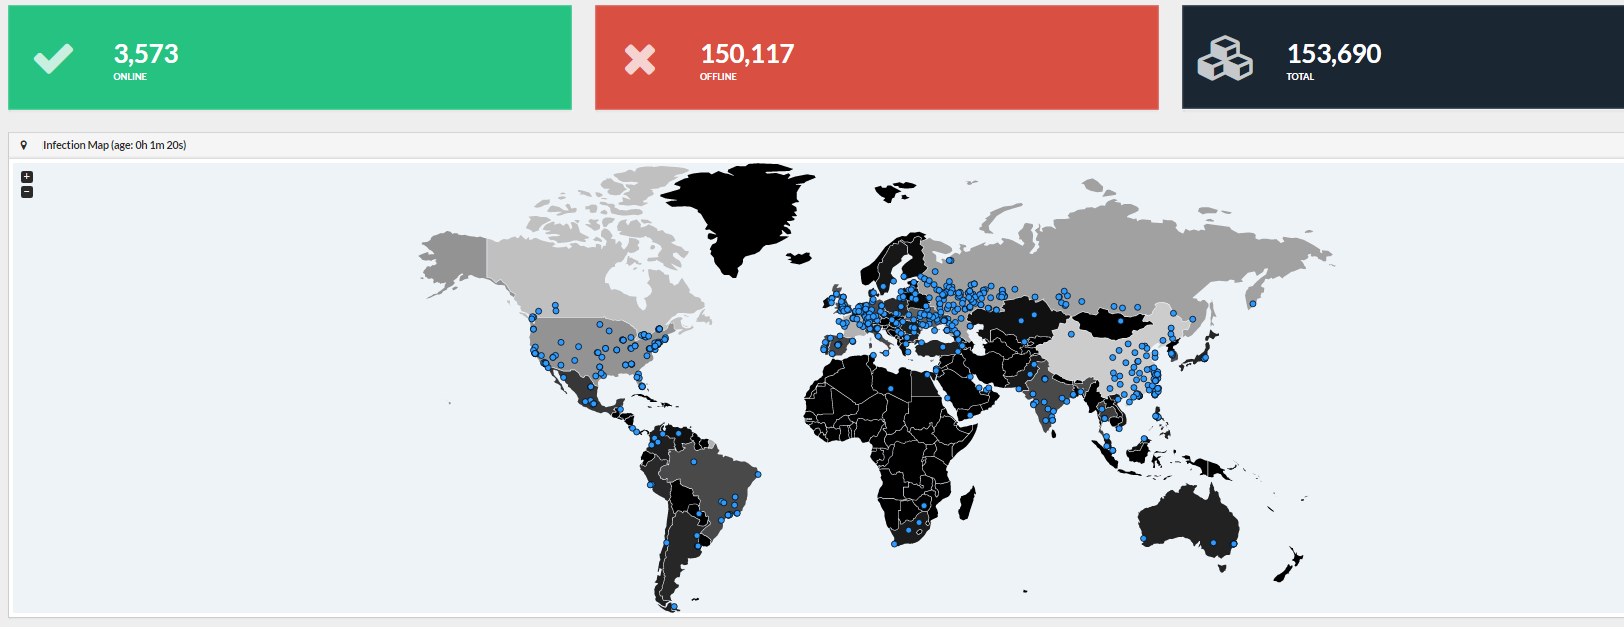
A security researcher developed a tool called wanadecrypt to restore encrypted files from Windows XP PCs infected by the WannaCry ransomware. The WannaCry ransomware made the headlines with the massive attack that hit systems worldwide during the weekend. The malicious code infected more than 200,000 computers across 150 countries in a matter of hours, it leverages the Windows […]
 Pierluigi Paganini
May 17, 2017
The tech giant Cisco announced an investigating on the potential impact of WannaCry malware on its products. Recent massive WannaCry ransomware attack highlighted the importance of patch management for any organization and Internet users. Another Tech giant, Cisco announced it is investigating the potential impact of WannaCry malware on its products, especially on its solutions that […]