 Pierluigi Paganini
 March 08, 2014
Cyber criminals are abusing even more Tor Network for illegal activities, from botnet management to money laundering, the number of services is increasing. Tor network is even more used by cyber criminals to cover their illegal activities, the Tor community has observed, for example an alarming increase in the number of malware that abuse of […]
 Pierluigi Paganini
February 08, 2014
Security experts at AppRiver detected a traffic spam spike linked to a new malware Campaign Targeting customers of Bank of America. Bank of America is being targeted by a new malicious campaign, cybercriminals are spreading a stealthy malicious financial malware to hit the clients of the financial institution. Security experts at AppRiver recently detected and blocked a set of […]
 Pierluigi Paganini
February 02, 2014
Researcher Dana Taylor is warning on the existence of two critical vulnerabilities in Oracle servers in the wild since a long time. Two serious vulnerabilities affect Oracle’s older database packages, allowing an attacker to remotely access a server bypassing authentication mechanism. Exploiting the flaws the attackers can browse the filesystem of the server accessing any files. […]
 Pierluigi Paganini
February 01, 2014
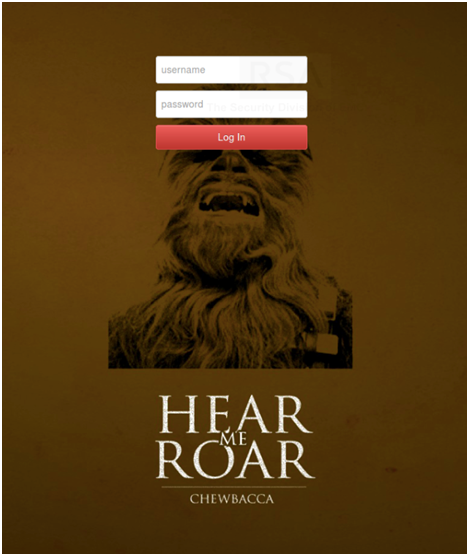
Researchers at RSA discovered a new variant of Tor-based malware ‘ChewBacca’, is able to infect Point-of-Sale stealing Credit Card data. The recent data breaches at US retailers Target, Neiman Marcus and Michaels have raised the alert level of malware-based attacks against POS systems. More than one hundred million Americans is victims of scams that mainly used a malware known as BlackPOS or […]
 Pierluigi Paganini
January 22, 2014
Microsoft has uprooted Tor Browser from more than 2 Million Systems to eradicate Sefnit botnet. It has done it silently without user agreement. It was August 2013 when security experts noted a spike in Tor traffic network caused by cybercriminals activities, the malware specialists discovered a botnet based on Mevade malware, in mid-August the number […]
 Pierluigi Paganini
January 19, 2014
Proofpoint discovered more Than 750,000 Phishing and SPAM Emails Launched From “Thingbots” Including Televisions, Fridge Recently security researchers from Proofpoint uncovered a cyber attack against the Internet of Things (IoT), more than 100,000 Refrigerators, Smart TVs and other smart household appliances have been hacked to send out 750,000 malicious spam emails. The nightmare comes true, dozens […]
 Pierluigi Paganini
January 15, 2014
Kaspersky experts discovered a java version of icefog espionage campaign that targeted at least 3 us oil, gas companies spreading a backdoor dubbed Javafog. Kaspersky Lab in September 2013 announced to have discovered Icefog team, an emerging group of cyber-mercenaries available for hire to conduct surgical hit and run operations against strategic targets. The cyber […]
 Pierluigi Paganini
January 14, 2014
Internet of Things, a business growing at a compound annual rate of 7,9%, which are the principal cyber threats to the popular paradigm? Another week is starting and this morning the topic that I’ve found everywhere is Internet of Things (IoT), it is a growing paradigm that will influence our life in the next future, […]
 Pierluigi Paganini
January 12, 2014
Intego Malware Research Team discovered that OSX Flashback trojan is still active with sinkholing activity. Mac users must be aware. Flashback Trojan is a cyber threat known since 2011, it is a trojan horse that targeted a Java vulnerability on Mac OS X machines, early 2012 it spread to infect up to 600,000 machines as […]
 Pierluigi Paganini
December 28, 2013
Security experts at Arbor Networks have found a couple of servers used to arrange a malicious campaign against PoS with Dexter malware. At the end of 2012, Israel based company Seculert notified about Dexter malware, used for parsing memory dumps of specific POS software related processes, looking for Track 1 / Track 2 credit card data. Dexter […]