


 Pierluigi Paganini
 October 05, 2026
MI5 warns UK universities that over 100 academics may have unknowingly worked on research funded by a Chinese institute linked to the MSS. On September 30, MI5 published a formal warning naming the China General Technology Research Institute, CGTRI, also called CAGT in some translations, as an outfit with very strong ties to China’s Ministry […]
 Pierluigi Paganini
October 03, 2026
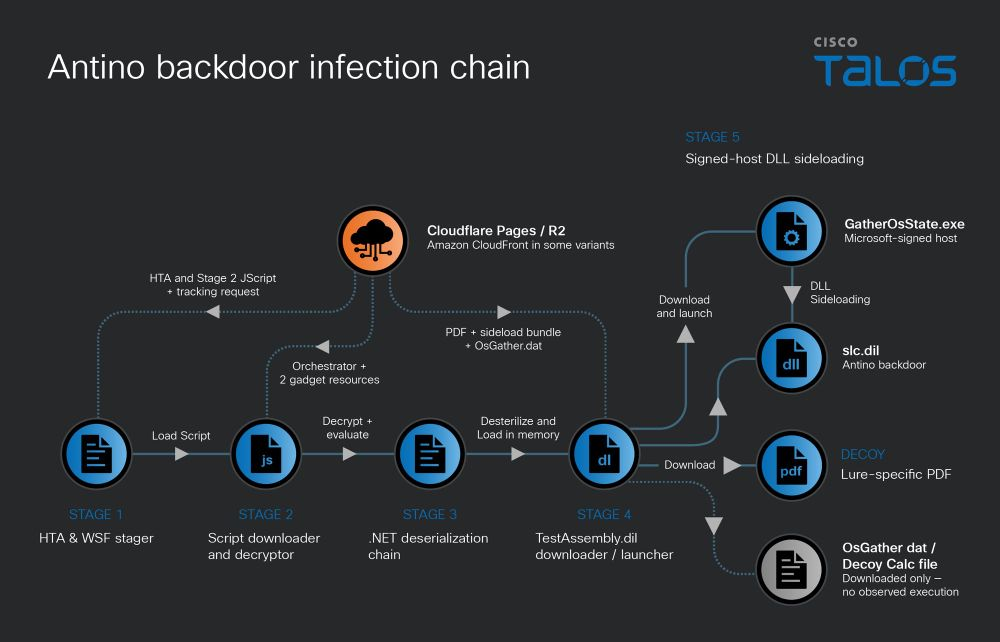
Cisco Talos details UAT-11587, a China-linked group using the Antino backdoor and Microsoft 365 as cover to spy on Asian governments. Cisco Talos has been tracking a cluster of espionage activity since September 2025 that it calls UAT-11587, and by July 2026 the group had hit at least 16 government and policy organizations across eight […]
 Pierluigi Paganini
September 20, 2026
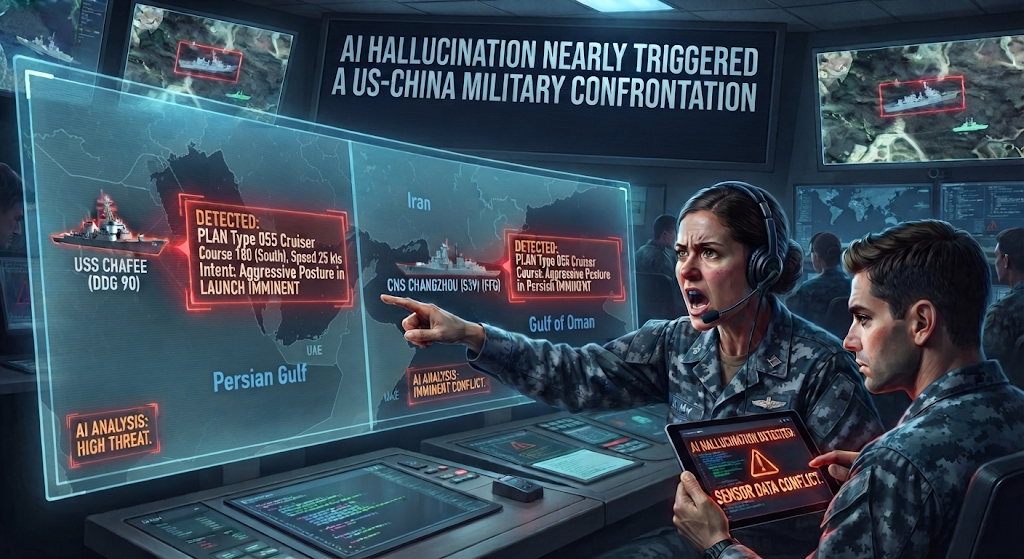
An AI-generated intelligence report falsely identified weapons on a Chinese ship, nearly triggering a US military operation during the Iran war. According to CNN, four sources familiar with the episode say an intelligence report circulated through the military claiming a Chinese vessel in the Middle East was carrying components for a nuclear weapons program. The […]
 Pierluigi Paganini
September 17, 2026
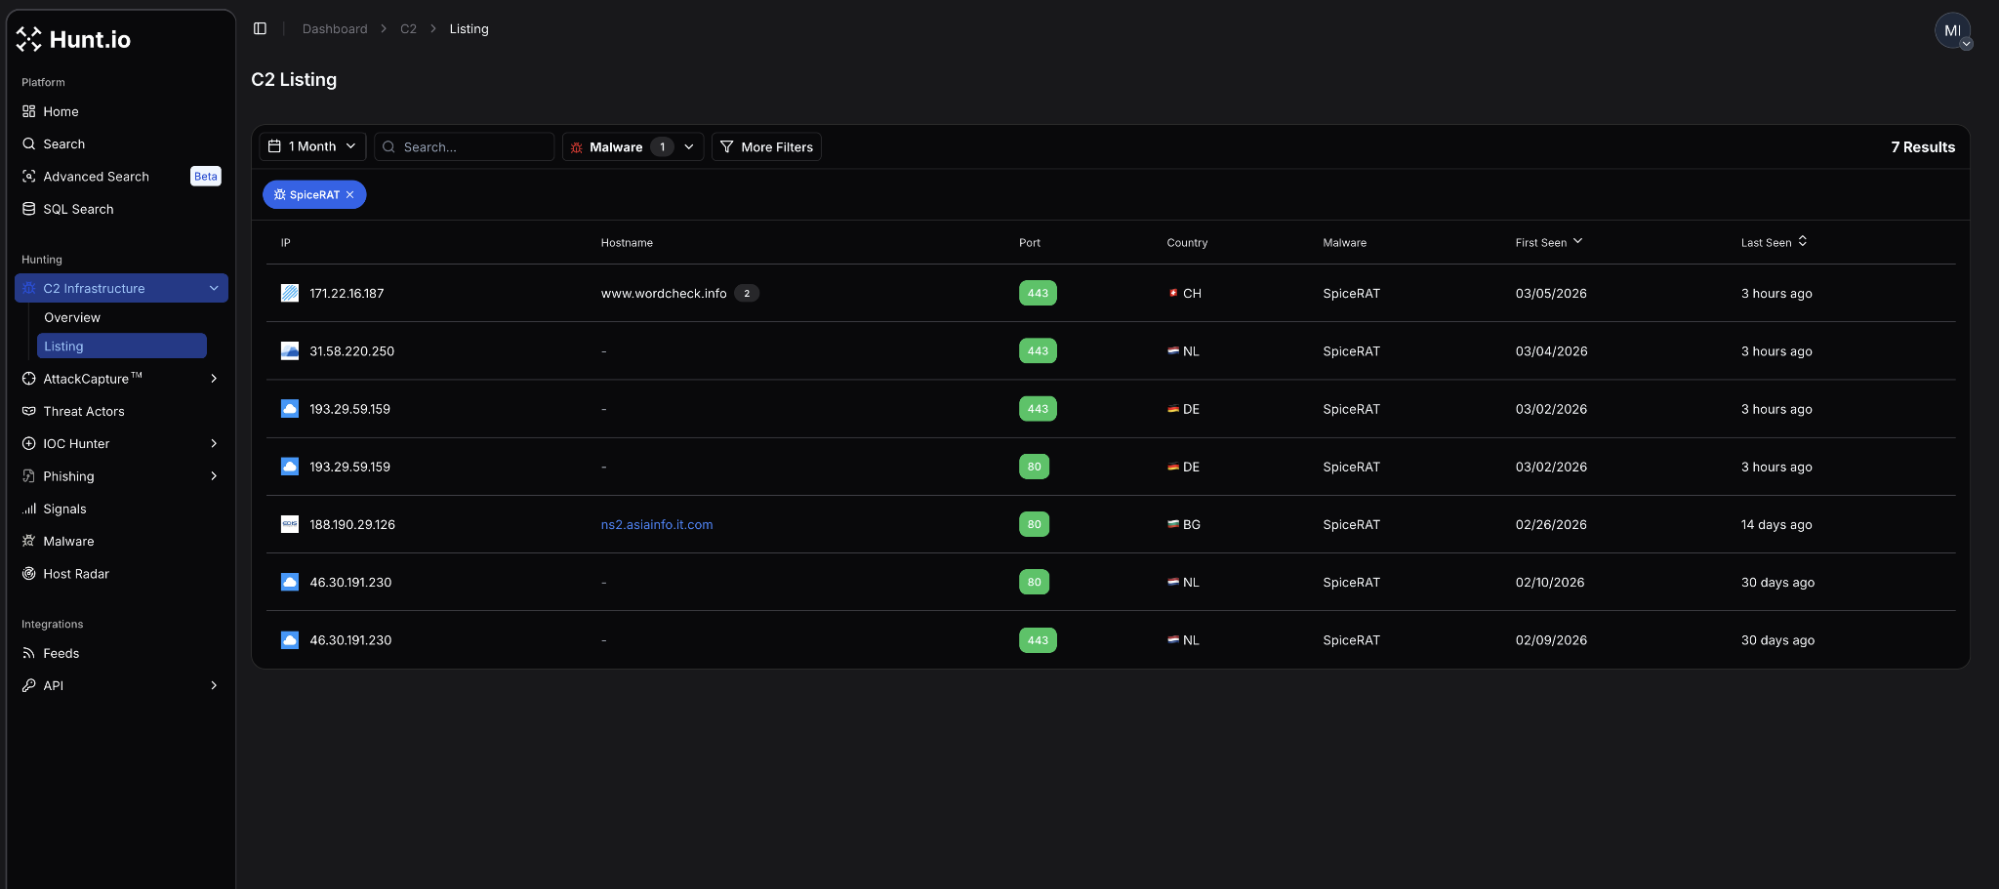
Hunt.io links SpiceRAT, NodeEdgeRAT and NomadRAT to a four-year SilkParasite campaign targeting governments and critical sectors in Central Asia. Hunt.io and researcher Guy Yasur have traced a tight cluster of SpiceRAT command‑and‑control servers that predate and extend Bitdefender’s August 2026 SilkParasite report. The work doesn’t dissect malware samples; it maps the network side of the […]
 Pierluigi Paganini
September 03, 2026
2,000 leaked files expose Bauman University’s hidden Department No. 4, which trained GRU-linked hackers and propagandists linked to APT28 and Sandworm. Leaked Documents Expose Bauman University’s Hidden Department That Trained Hackers, Propagandists, and Malware Developers for the GRU More than 2,000 internal documents from Bauman Moscow State Technical University have been reviewed by an international […]
 Pierluigi Paganini
August 31, 2026
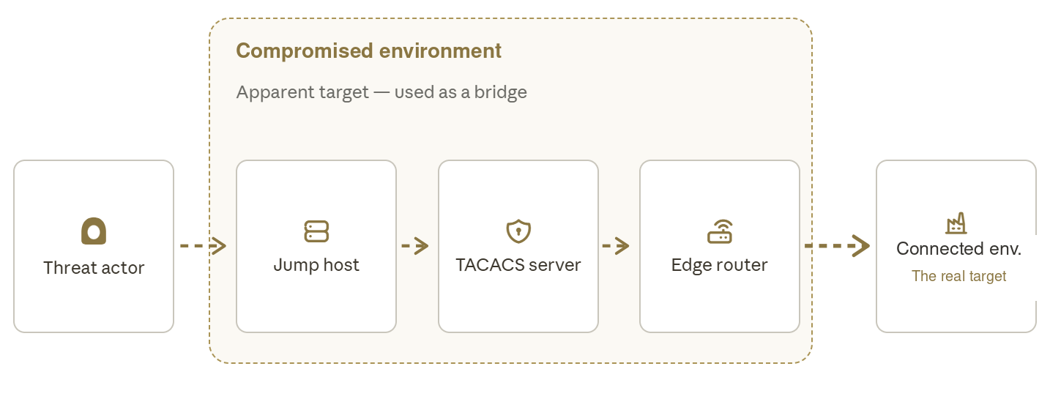
Fire Ant hijacked Cisco routers, stole credentials and altered logs to hide its tracks, using trusted infrastructure to reach high-value networks. Chinese-linked cyber espionage group Fire Ant has spent the past year quietly graduating from hacking individual computers to hacking the infrastructure that connects them. Sygnia’s new report traces how the group expanded from compromising […]
 Pierluigi Paganini
August 28, 2026
BlueDelta (APT28) uses webhook.site and Microsoft Edge to hide HOOKEDGE espionage traffic targeting European governments. Recorded Future’s Insikt Group documented a campaign by BlueDelta, the Russian GRU-linked group that overlaps with the group APT28, running an entire espionage operation against European government targets using webhook.site, a service built for developers to test HTTP requests, as […]
 Pierluigi Paganini
August 01, 2026
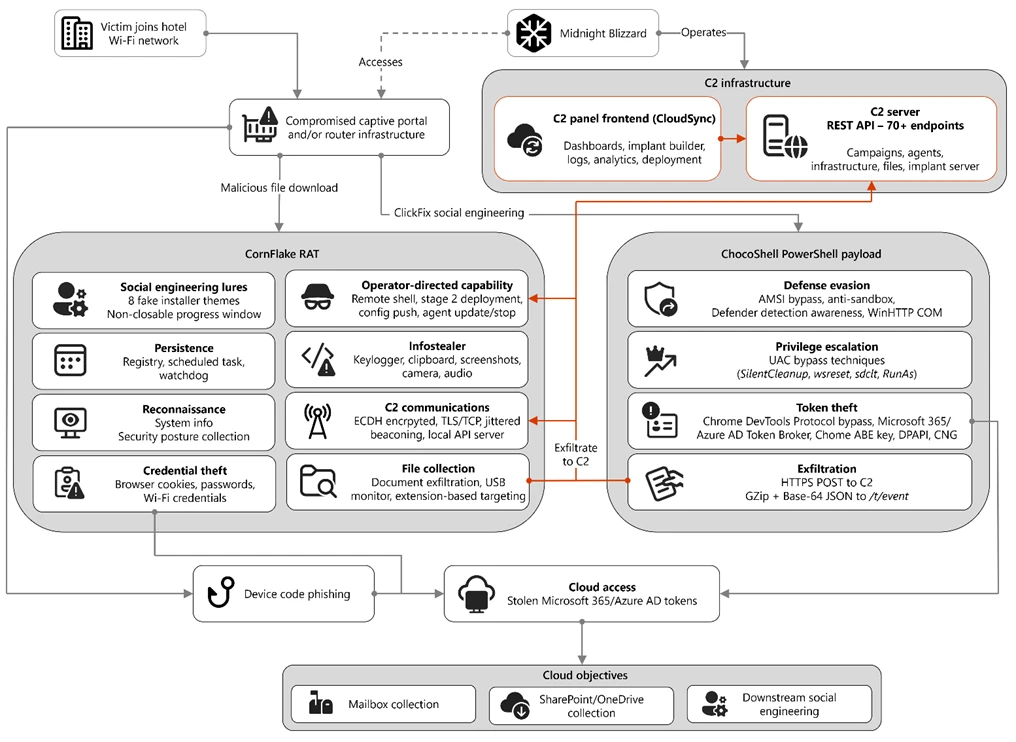
Microsoft says Russian hackers hijacked hotel Wi-Fi portals to spread malware and steal Microsoft 365 tokens from travelers. Microsoft Threat Intelligence disclosed CaptiveCrunch, a campaign it attributes to Storm-2945, an operational sub-cluster of Midnight Blizzard, the Russian SVR-linked group also known as APT29 and Cozy Bear. Since early May 2026, Storm-2945 has been manipulating DNS […]
 Pierluigi Paganini
July 24, 2026
US agencies warn Russian group Laundry Bear is exploiting a patched Zimbra flaw to steal email accounts from organizations running unpatched servers. The Cybersecurity and Infrastructure Security Agency (CISA), National Security Agency (NSA), Federal Bureau of Investigation (FBI) and other U.S. government and international partners published a joint advisory to warn that the Russia-linked APT […]
 Pierluigi Paganini
July 20, 2026
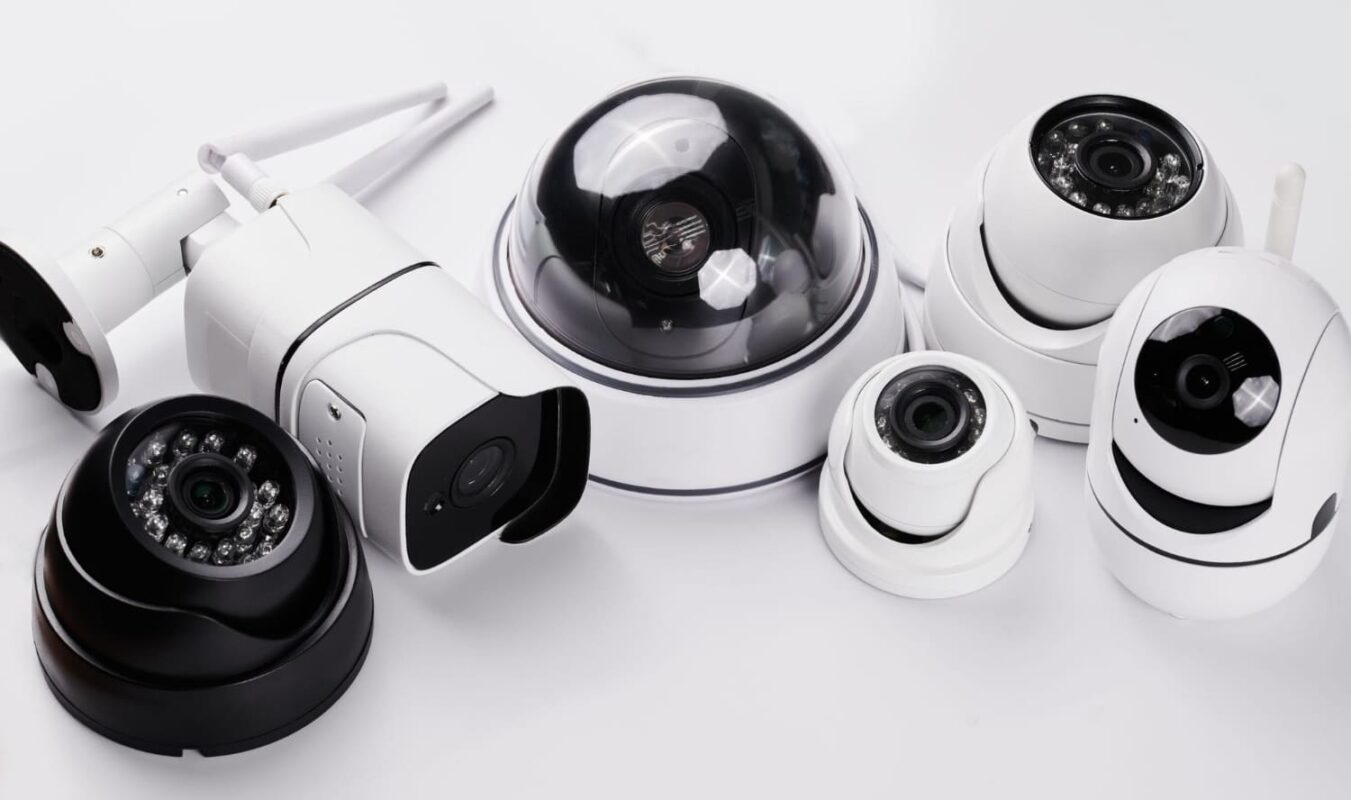
Dutch intelligence says Russia hacks IP cameras to monitor NATO military logistics and weapons shipments to Ukraine. The Netherlands’ AIVD and MIVD, the civilian and military intelligence services, published a joint advisory on July 10 confirming that at least one Russian intelligence service is systematically compromising internet-connected IP cameras across the Netherlands, other EU and […]







