


 Pierluigi Paganini
 August 31, 2026
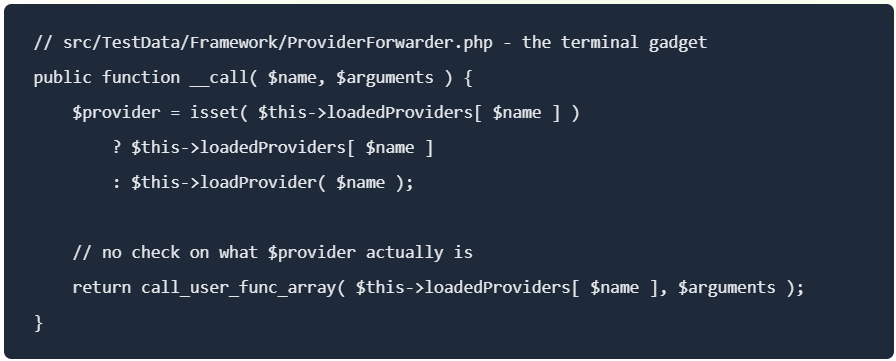
A critical GiveWP flaw lets unauthenticated attackers execute server commands. Version 4.16.7.2 fixes the PHP object injection chain. A critical vulnerability in GiveWP, one of the most widely used WordPress plugins for online donations and fundraising, can let an unauthenticated attacker execute commands on the server. Patchstack disclosed the flaw on August 28, after researcher […]
 Pierluigi Paganini
March 12, 2026
An unauthenticated SQL injection flaw (CVE-2026-2413) in the Ally WordPress plugin, used on 400K+ sites, could allow attackers to steal sensitive data. An unauthenticated SQL injection flaw, tracked as CVE-2026-2413 (CVSS score 7.5), in Ally plugin could allow attackers to steal sensitive data. The offensive security engineer Drew Webber at Acquia discovered the vulnerability on […]
 Pierluigi Paganini
May 28, 2024
Threat actors are exploiting a WordPress plugin to insert malicious PHP code in e-commerce sites and steal credit card data. Sucuri researchers observed threat actors using a PHP snippet WordPress plugin to install malicious code in WooCommerce e-stores and harvest credit card details. In the campaign spotted by the experts, attackers use a very obscure […]
 Pierluigi Paganini
July 18, 2023
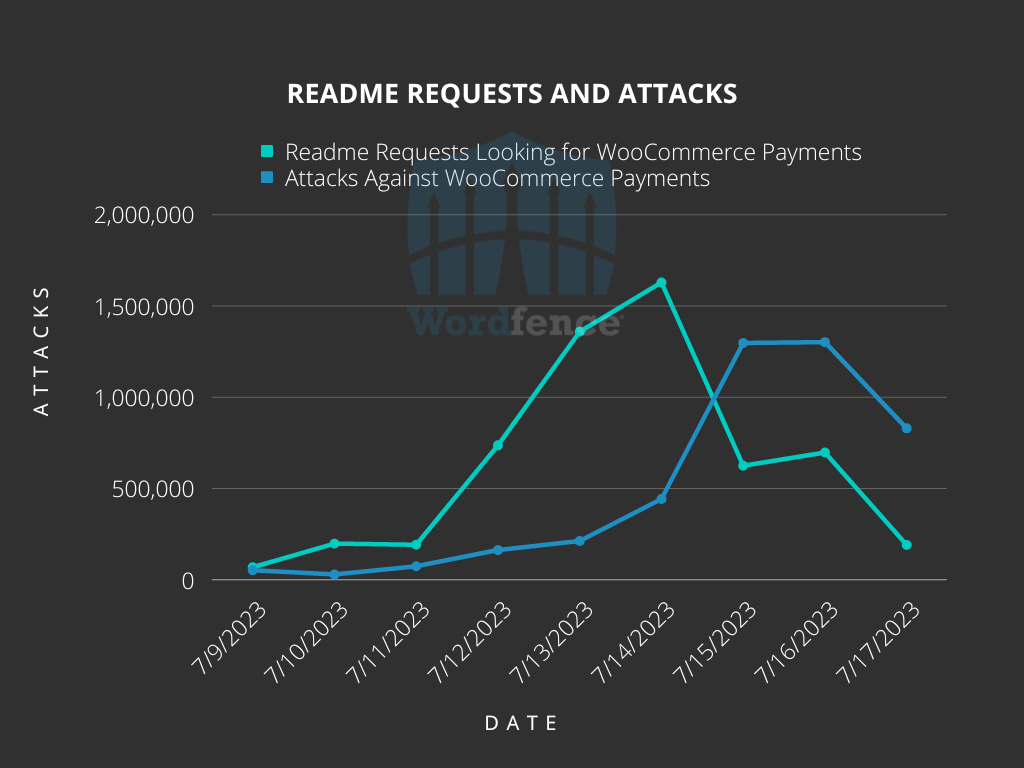
Threat actors are actively exploiting a critical flaw, tracked as CVE-2023-28121, in the WooCommerce Payments WordPress plugin. Threat actors are actively exploiting a recently disclosed critical vulnerability, tracked as CVE-2023-28121 (CVSS score: 9.8), in the WooCommerce Payments WordPress plugin. The flaw is an authentication bypass issue that can be exploited by an unauthenticated attacker to impersonate arbitrary […]
Pierluigi Paganini
March 31, 2023
Threat actors are actively exploiting a high-severity flaw in the Elementor Pro WordPress plugin used by more than eleven million websites WordPress security firm PatchStack warns of a high-severity vulnerability in the Elementor Pro WordPress plugin that is currently being exploited by threat actors in the wild. Elementor Pro is a paid plugin that is currently installed on […]
Pierluigi Paganini
December 25, 2022
Threat actors are actively exploiting a critical flaw in the YITH WooCommerce Gift Cards Premium WordPress plugin installed by over 50,000 websites. Hackers are actively exploiting a critical vulnerability, tracked as CVE-2022-45359 (CVSS v3: 9.8), affecting the WordPress plugin YITH WooCommerce Gift Cards Premium. The YITH WooCommerce Gift Cards Premium plugin allows websites of online stores to […]
Pierluigi Paganini
September 14, 2022
Threat actors are actively exploiting a zero-day vulnerability in the WPGateway premium plugin to target WordPress websites. The Wordfence Threat Intelligence team reported that threat actors are actively exploiting a zero-day vulnerability (CVE-2022-3180) in the WPGateway premium plugin in attacks aimed at WordPress sites. The WPGateway plugin is a premium plugin that allows users of […]
Pierluigi Paganini
February 10, 2022
WordPress plugin PHP Everywhere is affected by three critical issues that can be exploited to execute arbitrary code on affected systems. Wordfence experts found three critical remote code execution vulnerabilities in the PHP Everywhere WordPress plugin, all the issues have received a CVSS score of 9.9. The plugin that allows WordPress admins to insert PHP code […]
 Pierluigi Paganini
January 17, 2022
Researchers discovered a high-severity vulnerability in three different WordPress plugins that impact over 84,000 websites. Researchers from WordPress security company Wordfence discovered a high-severity vulnerability that affects three different WordPress plugins that impact over 84,000 websites. The vulnerability tracked as CVE-2022-0215 is a cross-site request forgery (CSRF) issue that received a CVSS score of 8.8. […]
Pierluigi Paganini
June 02, 2021
A critical zero-day vulnerability in the Fancy Product Designer WordPress plugin exposes more than 17,000 websites to attacks. Researchers from the Wordfence team at WordPress security company Defiant warn that a critical zero-day vulnerability, tracked as CVE-2021-24370, in the Fancy Product Designer WordPress plugin is actively exploited in the wild. Fancy Product Designer is a […]


Security / September 18, 2026

Artificial Intelligence / September 17, 2026
Hacking / September 17, 2026


