



 Pierluigi Paganini
 July 23, 2018
Researchers at CSE Cybsec ZLab analyzed a malicious code involved in a long-term espionage campaign in Syria attributed to a APT-C-27 group. A few days ago, the security researcher Lukas Stefanko from ESET discovered an open repository containing some Android applications. The folder was found on a compromised website at the following URL: hxxp://chatsecurelite.uk[.]to […]
 Pierluigi Paganini
July 10, 2018
Once USB Restricted Mode is enabled on a device, no data communications occur over the Lightning port, but experts found a way to reset the countdown timer. Recently Apple released the iOS 11.4.1 that introduced a new security feature, dubbed USB Restricted Mode, designed to protect your devices against USB accessories used by forensics experts and […]
 Pierluigi Paganini
July 06, 2018
This week Google released the July 2018 Android patches that address tens of vulnerabilities in the popular mobile operating system. Google released the July 2018 Android patches that address a total of 11 vulnerabilities, including three Critical issues and 8 High-risk flaws that affect the framework, media framework, and system. The critical vulnerabilities are remote code […]
 Pierluigi Paganini
July 06, 2018
Israeli military intelligence accused Hamas operatives of creating tainted apps to lure soldiers into downloading spyware onto their phones. According to a report published by the Israeli military, Hamas hackers are attempting to lure Israel Defence Forces (IDF) soldiers into installing tainted apps on their devices. Israeli military already blamed Hamas of similar attacks, but this […]
 Pierluigi Paganini
July 03, 2018
This week researchers demonstrated that most Android phones released since 2012 are still vulnerable to the RAMpage attack. In 2012, security researchers identified a bug in modern DRAM (dynamic random access memory) chips that could lead to memory corruption. In 2015, Google Project Zero researchers demonstrated “rowhammer“, a working exploit of this attack providing privilege […]
 Pierluigi Paganini
July 03, 2018
Some Samsung devices are randomly sending photos taken with the camera to contacts in the address book without permission. Do you have a Samsung smartphone? There is something you need to know. Some devices are randomly sending photos taken with the camera to contacts in the address book without permission. The problem affected Galaxy S9 and S9+ […]
 Pierluigi Paganini
July 01, 2018
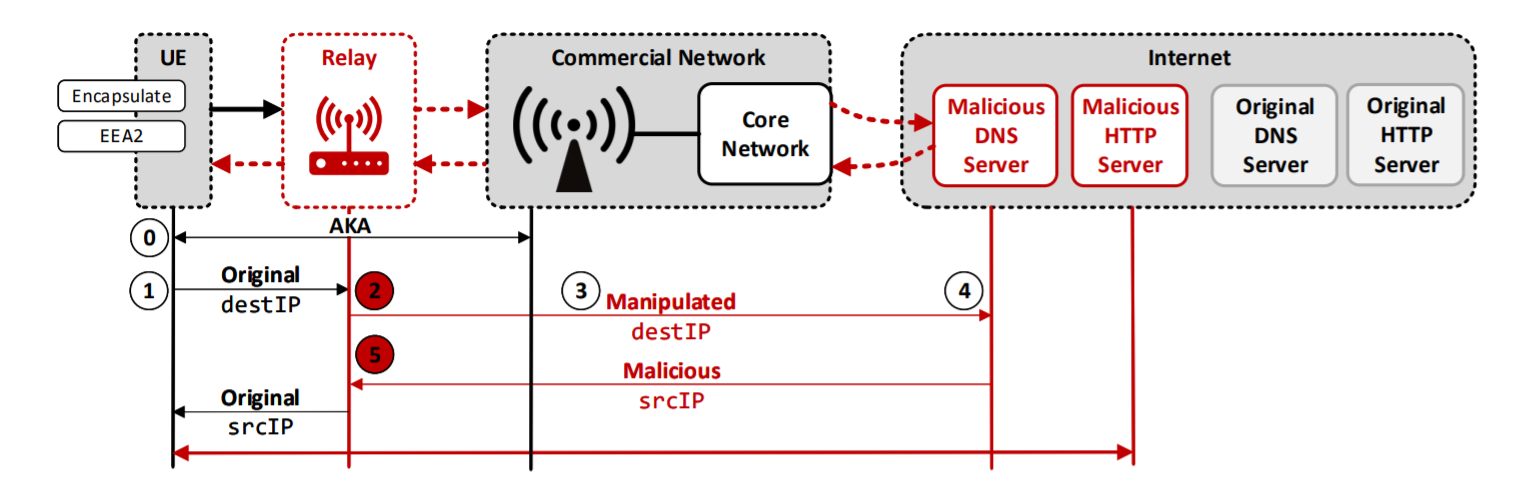
Security issues in the LTE mobile device standard could be exploited by persistent attackers to spy on users’ cellular networks and hijack data traffic. A team of from Ruhr-Universität Bochum and New York University Abu Dhabi has discovered some security issues in the LTE mobile device standard that could be exploited by persistent attackers (i.e. intelligence […]
 Pierluigi Paganini
June 26, 2018
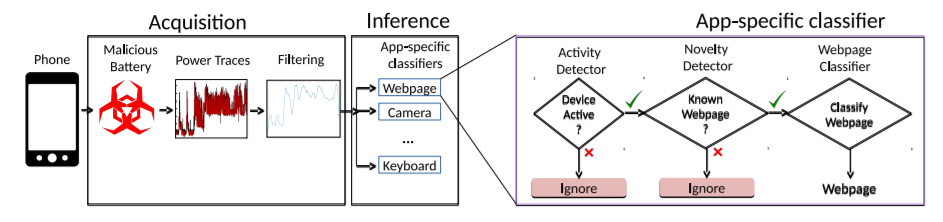
Security Researchers demonstrated how a “poisoned” cellphone battery in smartphones can be leveraged to “infer characters typed on a touchscreen We’ve heard about stealing information through blinking hard drive lights and computer speakers but would you believe the battery in your cell phone can also leak potentially sensitive information? Researchers at Technion Center for Security Science and Technology (CSST), Hebrew […]
 Pierluigi Paganini
June 24, 2018
A security researcher has devised a method to brute force a passcode on every Apple iPhone or iPad, even the up-to-date ones. Since iOS 8 rolled out in 2014, iPhone and iPad devices are protected with encryption, without providing passcode it is quite impossible to unlock the device. If the user enters more than 10 times […]
 Pierluigi Paganini
June 19, 2018
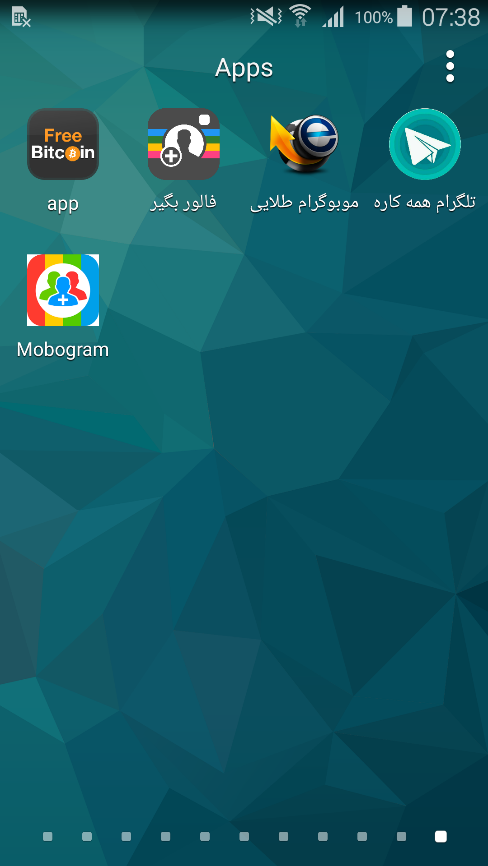
Malware researchers from ESET have discovered a new strain of Android RAT, tracked as HeroRat, that leverages Telegram protocol for command and control, and data exfiltration. HeroRat isn’t the first malware abusing Telegram protocol, past investigation reported similar threats like TeleRAT and IRRAT. The new RAT has been in the wild at least since August 2017 and in March […]
Malware / September 21, 2026
Uncategorized / September 21, 2026

Security / September 20, 2026

